TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.33K
Photos
435
Videos
3
Links
576

Showing posts older than #234 · Back to latest

Older Posts 20 shown
Post #233 622
CVE-2024-45519: RCE in Zimbra, critical rating 🔥

A bug in the postjournal service allows an attacker to remotely execute commands via email. According to Proofpoint, hackers are already trying to exploit the vulnerability.

Search at Netlas.io:
👉 Link: https://nt.ls/fea6Z
👉 Dork: http.favicon.hash_sha256:1afd891aacc433e75265e3ddc9cb4fc63b88259977811384426c535037711637

Vendor's advisory: https://wiki.zimbra.com/wiki/Zimbra_Security_Advisories
  • 🔥 6
  • 👍 4
  • 👾 3
Post #232 643
CVE-2024-8353: RCE in WordPress GiveWP Plugin, 10.0 rating 🔥🔥🔥

Due to Deserialization of Untrusted Data weakness, an attacker can inject malicious PHP code into the system. If you are using GiveWP, update it to last version as soon as possible.

Search at Netlas.io:
👉 Link: https://nt.ls/tpSXM
👉 Dork: http.body:"plugins/give/assets/dist"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/give/givewp-donation-plugin-and-fundraising-platform-3161-unauthenticated-php-object-injection
  • 🔥 5
  • 👾 5
Post #231 668
CVE-2024-42505, -42506, -42507: Multiple vulnerabilities in Aruba, 9.8 rating 🔥

Due to improper neutralization of special elements in commands, Aruba entities may be vulnerable to RCE, potentially creating a risk for enterprise networks.

Search at Netlas.io:
👉 Link: https://nt.ls/m0jnO
👉 Dork: http.favicon.hash_sha256:dfa04944308ed6c96563ff88cdb767ed5177c76c8a386f7a5803b534e9bff753

Vendor's advisory: https://support.hpe.com/hpesc/public/docDisplay?docId=hpesbnw04712en_us&docLocale=en_US
  • 🔥 5
  • 👾 2
Post #229 618
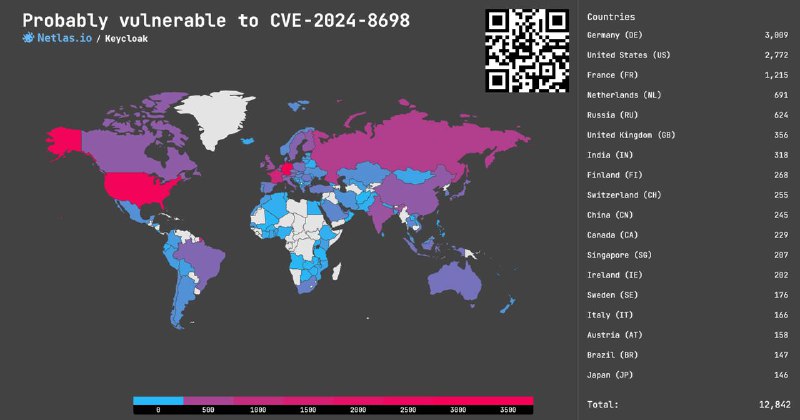
CVE-2024-8698: Privelege Escalation in Keycloak, 7.7 rating❗️

Improper SAML signature verification allows an attacker to create a document that is only partially signed. Due to the vulnerability, the entire document will be considered signed, which may lead to privelege escalation.

Search at Netlas.io:
👉 Link: https://nt.ls/LJfRK
👉 Dork: http.favicon.hash_sha256:47dcf1f1a8f1afd68297a294a263849069a7a62b2e86550241416c2cc56c5676

Read more: https://access.redhat.com/security/cve/CVE-2024-8698
  • 👾 4
  • 👍 3
  • 🔥 1
Post #227 708
CVE-2024-38812, -38813: Two vulnerabilities in VMware vCenter, 7.5 - 9.8 rating 🔥

Heap overflow and privilege escalation vulns on unpatched servers allow attackers to easily perform RCE using a specially crafted network packet.

Search at Netlas.io:
👉 Link: https://nt.ls/44tRg
👉 Dork: http.title:"ID_VC_Welcome" OR certificate.issuer.domain_component:"vsphere"

Vendor's advisory: https://support.broadcom.com/web/ecx/support-content-notification/-/external/content/SecurityAdvisories/0/24968
  • 🔥 4
  • 👾 3
Post #226
Netlas.io pinned «🔥 Netlas Private Scanner is Here! 🔥 Now you can perform super fast non-intrusive scan of any attack surface or even single IP address, and analyze up-to-date results 🔍 Other improvements: 🤝 Team features (sharing) added to the Discovery and Scanner 🐛 Fixed…»
Post #225 965
CVE-2024-38816: Path Traversal in Spring Framework, 7.5 rating❗️

An attacker can create a malicious HTTP request and use it to gain access to any file accessible by the Spring application process. However, this is easily blocked using the Spring Firewall, so don't forget to enable it.

Search at Netlas.io:
👉 Link: https://nt.ls/jT0JO
👉 Dork: tag.name:"spring"

Vendor's advisory: https://spring.io/security/cve-2024-38816
  • 🔥 3
  • 👾 3
  • 👍 1
Post #224 4.36K
🔥 Netlas Private Scanner is Here! 🔥

Now you can perform super fast non-intrusive scan of any attack surface or even single IP address, and analyze up-to-date results 🔍

Other improvements:
🤝 Team features (sharing) added to the Discovery and Scanner
🐛 Fixed the Discovery Download bug
🖥 Some minor updates

👉 Read more: https://docs.netlas.io/easm/scanner/
  • 👾 5
  • 🔥 3
  • ❤ 1
Post #223 3.58K
Reminder: The update begins in one hour. Netlas will be temporarily offline. We apologize for any inconvenience caused.
  • 👾 2
Post #222 731
🚧 Planned Update 🚧
The application will be unavailable for a period of time❗️

The update is scheduled to start on September 16, 2024, at 08:00 UTC ⏰. It is expected to take a couple of hours, and we will do our best to complete it as quickly as possible.

Please remember to save your work before this time.
  • 👾 3
  • 😭 1
  • 🙈 1
  • 💊 1
Post #220 716
CVE-2024-37288, -37285: RCE in Kibana, 9.9 rating 🔥🔥🔥

By improperly deserializing YAML, attackers can perform RCE. The attack is quite complex, but Elastic still recommends updating.

Search at Netlas.io:
👉 Link: https://nt.ls/cVF9O
👉 Dork: http.favicon.hash_sha256:30db4185530d8617e9f08858787a24b219ac5102321b48515baf5da7ac43b590

Read more: https://securityonline.info/critical-kibana-flaws-cve-2024-37288-cve-2024-37285-expose-systems-to-arbitrary-code-execution/
  • 👍 3
  • 👾 3
  • 🔥 2
Post #219 756
CVE-2024-44000: Unauthenticated Account Takeover in LiteSpeed Cache plugin for WordPress, 9.8 rating 🔥

A vulnerability in the debug log allows attackers to gain access to user sessions, potentially leading to complete control over a website.

Search at Netlas.io:
👉 Link: https://nt.ls/syLAy
👉 Dork: http.body:"plugins/litespeed-cache"

Read more: https://securityonline.info/cve-2024-44000-cvss-9-8-litespeed-cache-flaw-exposes-millions-of-wordpress-sites-to-takeover-attacks/
  • 👾 4
  • 🔥 3
  • 👍 1
Post #218 772
Using DNS History in Cybersecurity 🔍

DNS records are one of the most valuable sources of information for a researcher. Given the opportunity to observe them in retrospect, they become almost a silver bullet.

Our new article outlines potential use cases, as well as several tools that will allow you to take full advantage of DNS History in your work 🔥

👉 Read now: https://netlas.io/blog/dns_history_in_cybersecurity/

Enjoy reading!
netlas.io Using DNS History in Cybersecurity - Netlas Blog A detailed guide on how to use DNS History in cybersecurity. Use cases, best tools, and best practices.
  • 👾 3
  • 🔥 2
  • 👍 1
  • 👏 1
Post #217 704
Automated search for domain names with a specific TLD 🔥

How often have you researched companies that have their own TLDs? Listing all relevant domains would be very valuable...

The author of today's article noted that there is no single tool that lists all the required domain names. In order to automate these searches and simplify the building of an attack surface, he created the first utility to perform this task - tldfinder.

👉 tldfinder's GitHub: https://github.com/projectdiscovery/tldfinder
👉 Read more about tool: https://cloud.google.com/blog/topics/threat-intelligence/enumerating-private-tlds

In addition, we express our gratitude to N7WEra for finding a place for Netlas in his utility!
GitHub GitHub - projectdiscovery/tldfinder: A streamlined tool for discovering private TLDs for security research. A streamlined tool for discovering private TLDs for security research. - projectdiscovery/tldfinder
  • ❤ 3
  • 👍 3
  • 🐳 2
Post #216 673
CVE-2024-43425: RCE in Moodle, PoC is available 🔥🔥🔥

Due to incomplete sanitization in the “calculated questions” feature, attackers can transmit and execute arbitrary code, which can be used to disclose students’ confidential information or disrupt the entire learning process.

Search at Netlas.io:
👉 Link: https://nt.ls/6WaFx
👉 Dork: http.headers.set_cookie:"MoodleSession"

Read more: https://blog.redteam-pentesting.de/2024/moodle-rce/
  • 🔥 4
  • 👍 3
  • 👾 3
  • 🤓 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →