
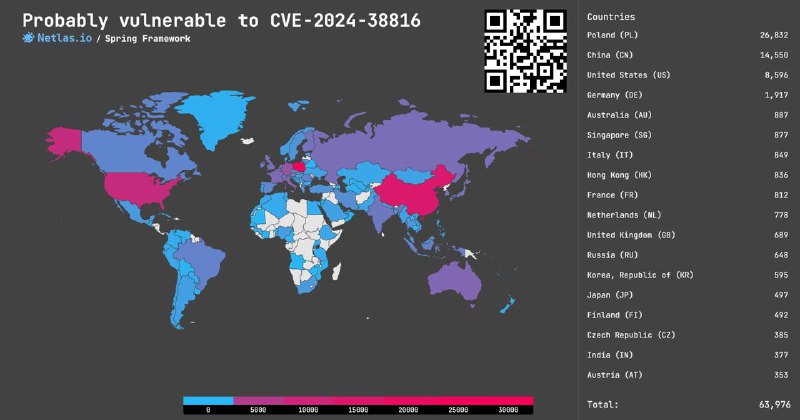
CVE-2024-38816: Path Traversal in Spring Framework, 7.5 rating❗️
An attacker can create a malicious HTTP request and use it to gain access to any file accessible by the Spring application process. However, this is easily blocked using the Spring Firewall, so don't forget to enable it.
Search at Netlas.io:
👉 Link: https://nt.ls/jT0JO
👉 Dork: tag.name:"spring"
Vendor's advisory: https://spring.io/security/cve-2024-38816
Post #225
965
- 🔥 3
- 👾 3
- 👍 1