TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.33K
Photos
436
Videos
3
Links
577

Showing posts older than #214 · Back to latest

Older Posts 20 shown
Post #213 686
CVE-2024-40766: Improper Access Control in SonicWall SonicOS, 8.6 rating❗️

An improper access control vulnerability in the SonicOS admin interface could allow an attacker to access sensitive information and even execute arbitrary code on an affected device.

Search at Netlas.io:
👉 Link: https://nt.ls/WTQRf
👉 Dork: http.headers.server:"sonicwall"

Vendor's advisory: https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2024-0015
  • ❤ 2
  • 🔥 2
  • 👾 2
  • 👍 1
Post #212 672
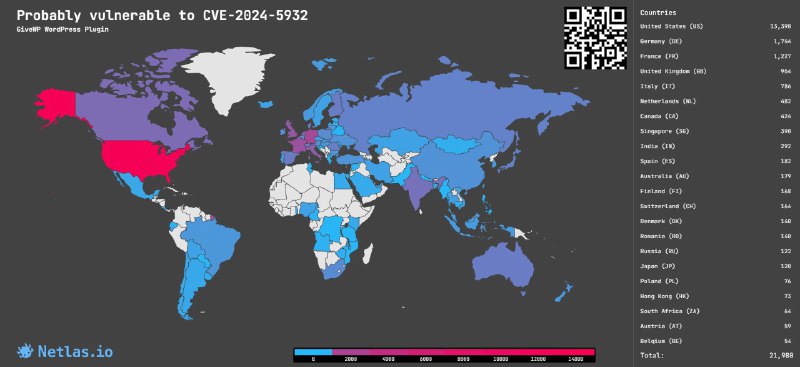
CVE-2024-5932: Deserialization of Untrusted Data in GiveWP plugin, 10.0 rating 🔥🔥🔥

Vulnerability discovered in the popular donation plugin leaves thousands of WordPress sites vulnerable to RCE and arbitrary file deletion.

Search at Netlas.io:
👉 Link: https://nt.ls/xS1vx
👉 Dork: http.body:"plugins/give/assets/dist"
  • 🔥 4
  • 👾 4
  • 👍 1
Post #211 801
CVE-2024-33533, -33535, -33536: Multiple vulns in Zimbra, 5.4 - 7.5 rating❗️

The vulnerabilities could allow an attacker to perform path traversal or create XSS injection, which could compromise sensitive data.

Search at Netlas.io:
👉 Link: https://nt.ls/0aGwL
👉 Dork: http.favicon.hash_sha256:1afd891aacc433e75265e3ddc9cb4fc63b88259977811384426c535037711637 OR \*.banner:"Zimbra"

Vendor's advisory: https://wiki.zimbra.com/wiki/Zimbra_Releases/10.0.8#Security_Fixes
  • 👾 5
  • 🔥 4
Post #209 677
Post #208 707
CVE-2024-22116: RCE in Zabbix, 9.9 rating 🔥

Lack of escaping for script parameters allows an attacker to execute arbitrary code.

Search at Netlas.io:
👉 Link: https://nt.ls/KoYW4
👉 Dork: http.favicon.hash_sha256:22b06a141c425c92951056805f46691c4cd8e7547ed90b8836a282950d4b4be2

Vendor's advisory: https://support.zabbix.com/browse/ZBX-25016
  • 🔥 4
  • 👾 3
  • 👏 1
Post #205 792
🚀 Netlas v.0.24.1 is live!

Our Attack Surface Discovery Tool now supports batch node addition and drag-and-drop for easier grouping. Plus, we’ve added a system theme property to control the dark/light mode.

Changelog is here: https://docs.netlas.io/changelog/
docs.netlas.io Changelog - Netlas Docs Explore the latest updates, enhancements, and fixes on the Netlas platform. Stay informed with our Changelog for all product and feature developments.
  • 🔥 3
  • 👍 2
  • 👾 2
  • ❤ 1
Post #204 776
Mastering Online Cameras Searching 📹

Intrigued by global events? Live cameras offer a solution. Millions of Internet-connected devices worldwide provide real-time views of live events, like public gatherings and conflicts💥

IoT search engines, Google dorking, and niche websites: learn how to search online cameras around the world 🔎

👉 Read now: https://netlas.io/blog/find_online_cameras/
netlas.io Mastering Online Camera Searches - Netlas Blog A guide on how to find exposed webcams anywhere in the world. Techniques, tools, and best practices. Examples of searching for the most popular devices.
  • 👍 7
  • ❤ 1
  • 🍓 1
  • 👾 1
Post #203 794
Best Attack Surface Visualization Tools 🗺

Visualization of the Attack Surface is the final stage in its discovery. In this article we will talk about tools that can make this process easier 🔍

👉 Read now: https://netlas.io/blog/best_attack_surface_visualization_tools/
netlas.io Best Attack Surface Visualization Tools - Netlas Blog Explore top tools that help visualize your attack surface, enabling better threat detection and improved security posture for your organization.
  • 👾 5
  • 🔥 3
  • 👍 2
  • ⚡ 1
  • 🫡 1
Post #201 921
Complete Guide on Attack Surface Discovery 🔍

Check out our latest article detailing the steps a cybersecurity researcher can follow to construct an Attack Surface using Netlas.io and other tools. Don't miss it! 🔥

👉🏻 Read now: https://netlas.io/blog/attack_surface_discovery_guide/
netlas.io Complete Guide on Attack Surface Discovery - Netlas Blog A comprehensive approach to mapping your attack surface, helping you identify vulnerabilities, assess risks, and implement effective security measures.
  • 🔥 5
  • 👾 5
  • 🍾 1
Post #200 1.01K
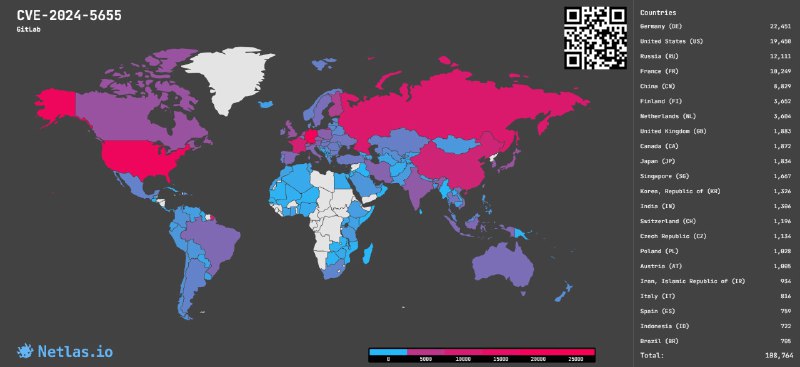
CVE-2024-6385: Improper Access Control in GitLab, 9.6 rating 🔥

The new vulnerability allows an attacker to run pipeline jobs with the rights of any other user.

Search at Netlas.io:
👉 Link: https://nt.ls/HvsUY
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef

Read more: https://www.bleepingcomputer.com/news/security/gitlab-warns-of-critical-bug-that-lets-attackers-run-pipelines-as-an-arbitrary-user/
  • 👍 4
  • 👾 4
  • 🔥 3
Post #199 819
CVE-2024-5441: Arbitrary file uploads in Modern Events Calendar (WordPress plugin), 8.8 rating❗️

The vulnerability allows an attacker to upload any file to the server of the affected site, which makes RCE possible. According to Wordfence, hackers are already trying to exploit this vulnerability.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/aC1J0
👉🏻 Dork: http.body:"plugins/modern-events-calendar"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/id/0c007090-9d9b-4ee7-8f77-91abd4373051?source=cve
  • 👾 5
  • 👍 4
  • 🔥 3
Post #198 747
CVE-2024-39929: Bypass of attachment verification in Exim❗

Due to incorrect parsing of a multiline RFC 2231 header filename, an attacker can bypass attachment verification and send an executable payload to the victim.

Search at Netlas.io:
👉 Link: https://nt.ls/gRdtH
👉 Dork: smtp.banner:"Exim" NOT smtp.banner:"Exim 4.98"

Read more: https://bugs.exim.org/show_bug.cgi?id=3099#c4
  • 🔥 5
  • 👍 2
  • 👾 2
Post #196 921
CVE-2024-6387 (and probably CVE-2006-5051): Unauthenticated RCE in OpenSSH 🔥

The vulnerability, discovered by Qualys researchers, allows an attacker to perform RCE on any OpenSSH server, provided that the operating system contains the glibc library.

Versions 8.5p1 to 9.8p1 ​​are affected, and versions <4.4p are also potentially vulnerable.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/ySN3C
👉🏻 Dork: tag.openssh.version:(>=8.5 AND <9.8) OR tag.openssh.version:(<4.4)

Read more: https://www.qualys.com/regresshion-cve-2024-6387/
  • 🔥 3
  • 👾 3
  • 👍 2
  • 🤔 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →