
CVE-2024-39931: Argument Injection in Gogs, 9.9 rating 🔥
The vulnerability published by SonarSource allows an attacker to delete or edit files/code stored on a vulnerable Gogs server.
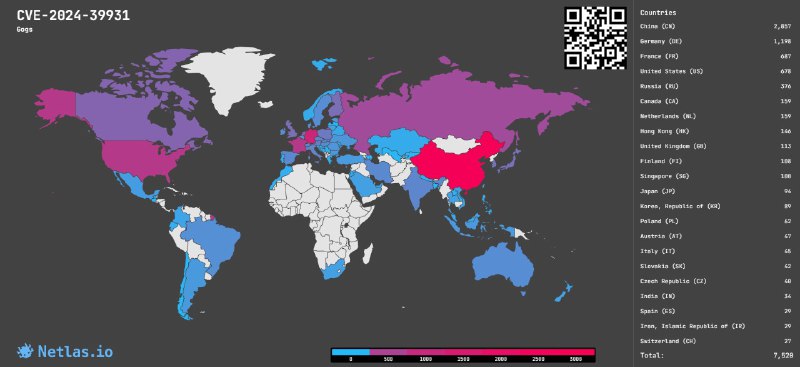
Search at Netlas.io:
👉 Link: https://nt.ls/adMql
👉 Dork: http.meta:"content=\"Gogs"
Read more: https://www.sonarsource.com/blog/securing-developer-tools-unpatched-code-vulnerabilities-in-gogs-1/
Post #197
800
- 🔥 4
- 👾 3
- 👍 2