TGViewer
Netlas.io Netlas.io @netlas · 2.33K subscribers
Post #229 618
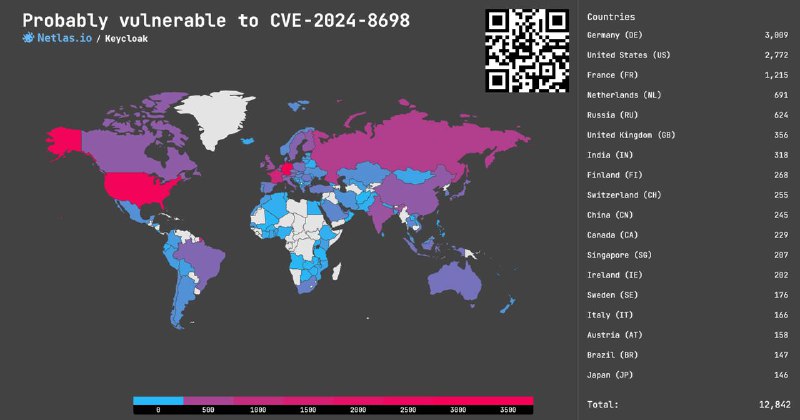
CVE-2024-8698: Privelege Escalation in Keycloak, 7.7 rating❗️

Improper SAML signature verification allows an attacker to create a document that is only partially signed. Due to the vulnerability, the entire document will be considered signed, which may lead to privelege escalation.

Search at Netlas.io:
👉 Link: https://nt.ls/LJfRK
👉 Dork: http.favicon.hash_sha256:47dcf1f1a8f1afd68297a294a263849069a7a62b2e86550241416c2cc56c5676

Read more: https://access.redhat.com/security/cve/CVE-2024-8698
  • 👾 4
  • 👍 3
  • 🔥 1
More from @netlas
  1. Sep 29, 2026CVE-2026-88771 & CVE-2026-887722: RCE and/or DoS in Citrix NetScaler ADC and NetScaler Gat…
  2. Sep 25, 2026CVE-2026-13016 and others: Multiple vulnerabilities in ServiceNow, up to 9.3 Rating 🔥 Rec…
  3. Sep 24, 2026CVE-2026-88804: Unauthenticated update of public UI settings leading to stored XSS in Ranc…
  4. Sep 23, 2026CVE-2026-87902: Path Traversal in WordPress leading to RCE, 9.2 Rating 🔥 Another newly di…
  5. Sep 22, 2026CVE-2026-93952: Improper Input Validation in VeloCloud Orchestrator, 10.0 Rating 🔥 A rece…
  6. Sep 21, 2026CVE-2026-13684 and others: Multiple vulnerabilities in Synology DSM, up to 9.8 Rating 🔥 S…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →