TGViewer
Channel Public Channel
Proxy Bar

Proxy Bar

@proxy_bar

Exploits, Hacking and Leaks

Чат группы - https://t.me/

Связь с администрацией и реклама:
@NULL_vm

Поддержать проект:
BTC bc1qmrt229eghjyj9wqa7nmr9j8zuq6khz6km2pker
Subscribers
21.5K
Photos
1.7K
Videos
107
Links
1.8K

Showing posts older than #3551 · Back to latest

Older Posts 20 shown
Post #3550 6.78K
back to the future ))
  • 🔥 29
  • 👍 28
  • 😱 8
Post #3549 7.43K
CVE-2026-47291: Integer Overflow Remote Code Execution in Windows HTTP.sys

Original text: “CVE-2026-47291: Remote Code Execution in the Windows HTTP.sys” — Yazhi Wang and Jonathan Lein, TrendAI Zero Day Initiative (July 10, 2026). Code blocks are reproduced verbatim from the original with attribution captions.

Executive Summary

CVE-2026-47291 is a critical remote code execution vulnerability in HTTP.sys, the kernel-mode HTTP protocol driver that underpins Internet Information…

https://core-jmp.org/2026/07/cve-2026-47291-rce-windows-http-sys/
  • 🔥 9
  • 👍 2
Post #3548 6.32K
Harnessing LLM Harnesses: AI Orchestration for Offensive Security Research

Original text: “Harnessing Harnesses – Climbing the LLM Hills” — Andy Gill, ZephrSec / blog.zsec.uk (27 Jun 2026).

Executive Summary

Most LLM workflow discussion centres on prompt engineering and model selection, yet in practice the biggest gains in capability, cost and reliability come from the orchestration layer sitting above the model—what Andy Gill (ZephrFish) calls…

https://core-jmp.org/2026/07/harnessing-llm-harnesses-offensive-security-ai-orchestration/
  • 🔥 5
Post #3547 5.39K
Process Parameter Poisoning: EDR Evasion via Windows Process Startup Parameters

Original text: “Process Parameter Poisoning” — Max Hirschberger & Ogulcan Ugur, SensePost / Orange Cyberdefense (6 July 2026). Code listings and figures are reproduced verbatim with attribution captions.

Executive Summary

Process Parameter Poisoning (P3) is a code injection technique that transfers shellcode into a foreign process via the startup parameters of CreateProcessW—specifically the lpCommandLine, lpEnvironment,…

https://core-jmp.org/2026/07/process-parameter-poisoning-edr-evasion-windows/
  • 🔥 4
Post #3546 4.87K
The Dark Side of WebAssembly: Cryptomining, Keyloggers, and Browser Exploitation

Original text: “El lado oscuro de WebAssembly” — Carlos Ávila, Telefónica Tech Blog (September 16, 2020). Images are reproduced verbatim with attribution captions.

Executive Summary

WebAssembly (WASM) is an open binary instruction format — announced in 2015 and broadly supported by browsers from 2017 onward — designed to let code written in C, C++, Rust,…

https://core-jmp.org/2026/07/dark-side-webassembly-cryptomining-keyloggers-browser-exploitation/
  • 👍 6
  • 🔥 3
  • 😱 1
Post #3545 5.1K
Debugging the Pixel 8 Kernel via KGDB

Original text: “Debugging the Pixel 8 kernel via KGDB” — Andrey Konovalov, xairy.io (Jul 28, 2025; revised Mar 11, 2026). Code, tables and figures below are reproduced verbatim with attribution captions.

Executive Summary

Debugging a running Linux kernel on a physical device is qualitatively different from debugging inside a virtual machine. Hypervisors expose built-in GDB…

https://core-jmp.org/2026/07/debugging-pixel-8-kernel-kgdb/
  • 🔥 8
  • 👍 3
Post #3544 5.9K
Januscape: Guest-to-Host Escape in KVM/x86
*
PoC
  • 👍 6
  • 🔥 5
  • 😱 5
Post #3543 7.35K
CVE-2026-43499 - ALL Linux distributions for 15 years
*
writeUP
*
exploit

#linux #lpe
  • 👍 14
  • 😱 10
  • 🔥 6
Post #3542 5.81K
CVE-2026-48282 Adobe ColdFusion's Remote Development Service (RDS)
*
PoC
  • 🔥 5
  • 😱 4
  • 👍 2
Post #3541 6.11K
How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike Command & Control Servers

Original text: “How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike Command & Control Servers” — Matthew, Embee Research (Dec 08, 2023). Images reproduced verbatim with attribution captions.

Executive Summary

Cobalt Strike shellcode is one of the most widely deployed payloads in commodity malware campaigns, yet its analysis remains non-trivial for practitioners new…

https://core-jmp.org/2026/07/ghidra-shellcode-analysis-cobalt-strike/
  • 🔥 6
  • 👍 2
Post #3540 5.55K
Breaking eBPF Security: How Kernel Rootkits Blind Observability Tools

Original text: “Breaking eBPF Security: How Kernel Rootkits Blind Observability Tools” — 0xMatheuZ, matheuzsecurity.github.io. Code blocks are reproduced verbatim with attribution captions.

Executive Summary

eBPF-based security tools — Falco, Tracee, Tetragon, GhostScan — have become the dominant approach to Linux kernel observability and runtime threat detection. They attach to syscall tracepoints and kernel events, stream…

https://core-jmp.org/2026/07/breaking-ebpf-security-kernel-rootkits-blind-observability-tools/
  • 🔥 3
  • 😱 1
Post #3539 5.63K
setresuid(⚡): Glitching Google’s TV Streamer from ADB to Root

Original text: “setresuid(⚡): Glitching Google’s TV Streamer from adb to root” — Raelize B.V. (May 17, 2026). Code blocks, tables, and figures are reproduced verbatim with attribution captions.

Executive Summary

Researchers at Raelize B.V., presenting at hardwear.io NL 2025, demonstrated a practical electromagnetic fault injection (EMFI) attack against Google’s TV Streamer 4K. Starting from an…

https://core-jmp.org/2026/07/setresuid-glitching-google-tv-streamer-adb-root/
  • 🔥 9
Post #3537 5.94K
How I Ruined My Vacation by Reverse Engineering WSC

Original text: “how i ruined my vacation by reverse engineering wsc” — es3n1n, blog.es3n1n.eu (May 8, 2025). Code blocks and figures are reproduced verbatim with attribution captions.

Executive Summary

es3n1n is the author of no-defender, a tool that disabled Windows Defender by calling Windows Security Center (WSC) COM APIs while posing as an authorized security…

https://core-jmp.org/2026/07/how-i-ruined-my-vacation-reverse-engineering-wsc/
  • 🔥 5
  • 👍 4
  • 😱 3
Post #3536 4.86K
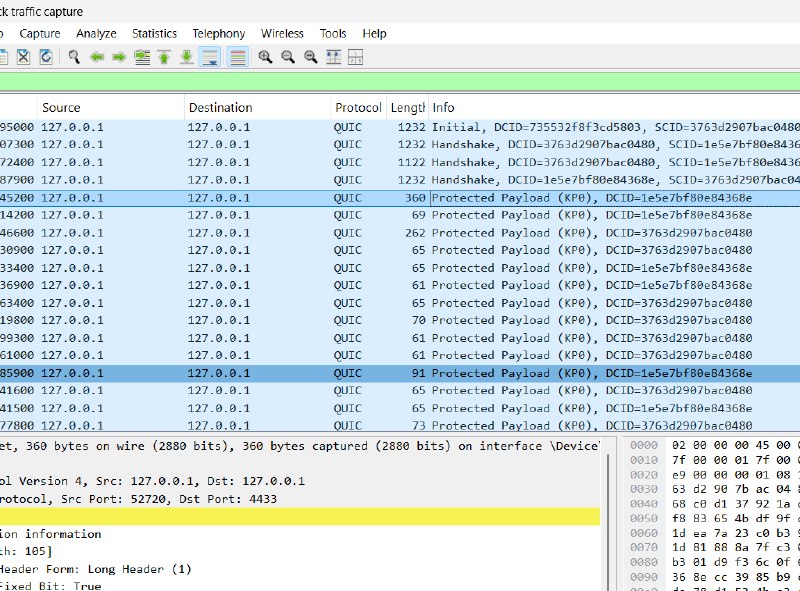
Building an Encrypted C2 Implant Using QUIC

Original text: “Building an Encrypted C2 Implant Using QUIC” — R.B.C (g3tsyst3m), G3tSyst3m’s Infosec Blog (April 30, 2026). Code blocks and figures are reproduced verbatim with attribution captions.

Executive Summary

This article by R.B.C (g3tsyst3m) walks through the construction of a minimal proof-of-concept C2 implant—crudeRAT—that uses the QUIC protocol as its transport layer. QUIC is…

https://core-jmp.org/2026/07/building-encrypted-c2-implant-quic/
  • 👍 4
  • 🔥 3
Post #3535 4.53K
The QNAP Pattern: Systemic Security Failures in QTS Plugin Architecture

Original text: “The QNAP Pattern” — Runic Labs. Code blocks, tables, and figures are reproduced verbatim with attribution captions.

Executive Summary

QNAP NAS devices suffer from a recurring class of architectural security failures that go well beyond individual CVEs. Researchers at Runic Labs analyzed four vulnerabilities spanning two plugins—Notes Station 3 and QmailAgent—and found that…

https://core-jmp.org/2026/07/the-qnap-pattern-systemic-security-failures-in-qts-plugin-architecture/
  • 🔥 2
Post #3534 4.8K
Callback Hell: Abusing Callbacks, Tail-Calls, and Proxy Frames to Obfuscate the Stack

Original text: “Callback hell: abusing callbacks, tail-calls, and proxy frames to obfuscate the stack” — klezVirus, personal security research blog (December 21, 2025). Code, tables and figures below are reproduced verbatim with attribution captions. Licensed under CC BY 4.0.

Executive Summary

This post by klezVirus explores a set of novel techniques for obfuscating call stacks…

https://core-jmp.org/2026/07/callback-hell-stack-obfuscation-proxy-frames/
  • 🔥 2
  • 👍 1
Post #3533 5.62K
если извлекать корень из числа с единицей измерения, единица тоже должна быть под корнем.
фокус в размерностях, так же можно сказать
5 метров = √25 метров = √0.025 километра и получить дичь ))),

математически смешно, но бухгалтер таки сядет))))
  • 👍 22
  • 😱 9
  • 🔥 7
Post #3531 6.72K
прикольный пиратский AI-каталог
*
мемный PoC
  • 👍 20
  • 🔥 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →