
Breaking eBPF Security: How Kernel Rootkits Blind Observability Tools
Original text: “Breaking eBPF Security: How Kernel Rootkits Blind Observability Tools” — 0xMatheuZ, matheuzsecurity.github.io. Code blocks are reproduced verbatim with attribution captions.
Executive Summary
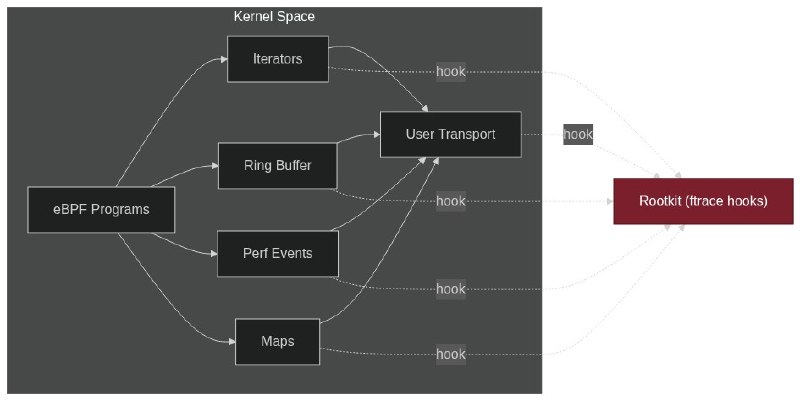
eBPF-based security tools — Falco, Tracee, Tetragon, GhostScan — have become the dominant approach to Linux kernel observability and runtime threat detection. They attach to syscall tracepoints and kernel events, stream…
https://core-jmp.org/2026/07/breaking-ebpf-security-kernel-rootkits-blind-observability-tools/
Post #3540
5.55K
- 🔥 3
- 😱 1