TGViewer
Channel Public Channel
Proxy Bar

Proxy Bar

@proxy_bar

Exploits, Hacking and Leaks

Чат группы - https://t.me/

Связь с администрацией и реклама:
@NULL_vm

Поддержать проект:
BTC bc1qmrt229eghjyj9wqa7nmr9j8zuq6khz6km2pker
Subscribers
21.5K
Photos
1.7K
Videos
107
Links
1.8K

Showing posts older than #3531 · Back to latest

Older Posts 20 shown
Post #3530 6.4K
CVE-2026-48558 SimpleHelp OIDC (OpenID Connect) Authentication Bypass
*
PoC
*
WriteUp
  • 👍 11
  • 🔥 2
Post #3529 5.79K
HDD Firmware Hacking Part 1

Original text: “HDD Firmware Hacking Part 1” — Ryan Miceli, icode4.coffee (May 14, 2026). Code blocks and screenshots are reproduced verbatim with attribution captions.

Executive Summary

Reverse engineering and modifying hard drive firmware sounds exotic, but the primitives turn out to be surprisingly accessible once you know where to look. In this first installment, security…

https://core-jmp.org/2026/07/hdd-firmware-hacking-part-1/
  • 👍 11
  • 🔥 9
  • 😱 2
Post #3527 5.49K
Breaking Out of Chrome’s Sandbox: A Native Messaging Backdoor Observed in Italy

Original text: “Breaking Out of Chrome’s Sandbox: A Native Messaging Backdoor Observed in Italy” — Andrea Draghetti, D3Lab (June 22, 2026). Code blocks, tables, and figures below are reproduced verbatim with attribution captions.

Executive Summary

In June 2026, Italian security firm D3Lab documented a targeted malware campaign distributing a compound browser threat via invoice-themed phishing…

https://core-jmp.org/2026/07/breaking-out-of-chromes-sandbox-native-messaging-backdoor-italy/
  • 🔥 5
Post #3526 5.29K
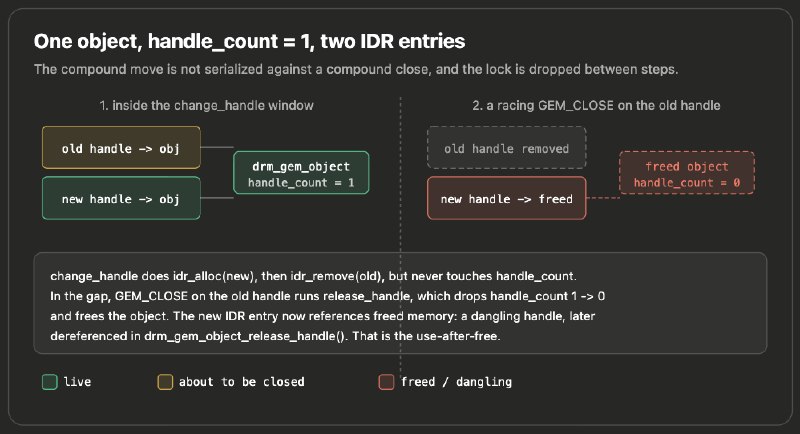
Unprivileged Root via Use-After-Free in Linux DRM GEM change_handle (CVE-2026-46215)

Original text: “Unprivileged root via a use-after-free in DRM GEM change_handle (CVE-2026-46215)” — cyberstan, cyberstan.co.uk (12 April 2026). Code blocks and figures below are reproduced verbatim with attribution captions.

Executive Summary

CVE-2026-46215 is a use-after-free (UAF) race condition in the Linux kernel’s Direct Rendering Manager (DRM) GEM subsystem, triggered through the drm_gem_change_handle_ioctl() interface. The ioctl…

https://core-jmp.org/2026/07/unprivileged-root-via-use-after-free-in-linux-drm-gem-change_handle-cve-2026-46215/
  • 🔥 4
Post #3525 5.04K
Disposable Tooling: Generating Mythic C2 Agents End-to-End With LLMs

Original text: “Disposable Tooling: Building LLM-Generated Mythic Agents from Prompt to Deployment” — Adam Chester, SpecterOps (Jun 24, 2026). Figures are reproduced with attribution captions and the agent summary table is reproduced verbatim; the prose below is an independent summary.

Executive Summary

Building a working agent for a command-and-control framework like Mythic has traditionally been…

https://core-jmp.org/2026/07/llm-generated-mythic-agents-disposable-tooling/
  • 🔥 3
Post #3524 4.92K
Ура, первые артефакты
коробок создан, data файл отдельно, detached header отдельно, metadata отдельно иLUKS2/argon2id на месте.

#check
  • 🔥 10
  • 👍 6
Post #3522 5.63K
IDT Table Hijacking under VBS/HVCI/kCET in Windows 11

Original text: “IDT Table Hijacking under VBS/HVCI/kCET in Windows 11” — author not clearly listed (Exploit Pack), Exploit Pack blog (June 26, 2026). Figures and the descriptor-format table below are reproduced with attribution captions.

Executive Summary

Modern Windows 11 stacks several kernel-protection layers on top of each other: Virtualization-Based Security (VBS), Hypervisor-protected Code Integrity (HVCI),…

https://core-jmp.org/2026/06/idt-table-hijacking-vbs-hvci-kcet-windows-11/
  • 🔥 7
Post #3521 5.29K
Pack2TheRoot (CVE-2026-41651): Local Root on Linux via a PackageKit Race Condition

Original text: “Privilege Escalation: Getting Started with the Pack2TheRoot (CVE-2026-41651) Vulnerability to Escalate Privileges” — aircorridor, Hackers Arise (May 1, 2026). Commands and figures below are reproduced verbatim with attribution captions.

Executive Summary

A high-severity vulnerability nicknamed Pack2TheRoot (CVE-2026-41651) was publicly disclosed and affects the default installation of many Linux distributions. The flaw lives in…

https://core-jmp.org/2026/06/pack2theroot-cve-2026-41651-linux-privilege-escalation/
  • 🔥 4
Post #3520 5.16K
Dissecting and Exploiting Linux LPE Variant: DirtyClone (CVE-2026-43503)

Original text: “Dissecting and Exploiting Linux LPE Variant: DirtyClone (CVE-2026-43503)” — Eddy Tsalolikhin and Or Peles, JFrog Security Research (25 Jun 2026). Code, figures and the PoC video below are reproduced verbatim with attribution captions.

Executive Summary

CVE-2026-43503, nicknamed DirtyClone, is a high-severity (CVSS 8.8) local privilege escalation in the Linux kernel. It is the…

https://core-jmp.org/2026/06/dirtyclone-cve-2026-43503-linux-lpe/
  • 🔥 8
Post #3519 5.15K
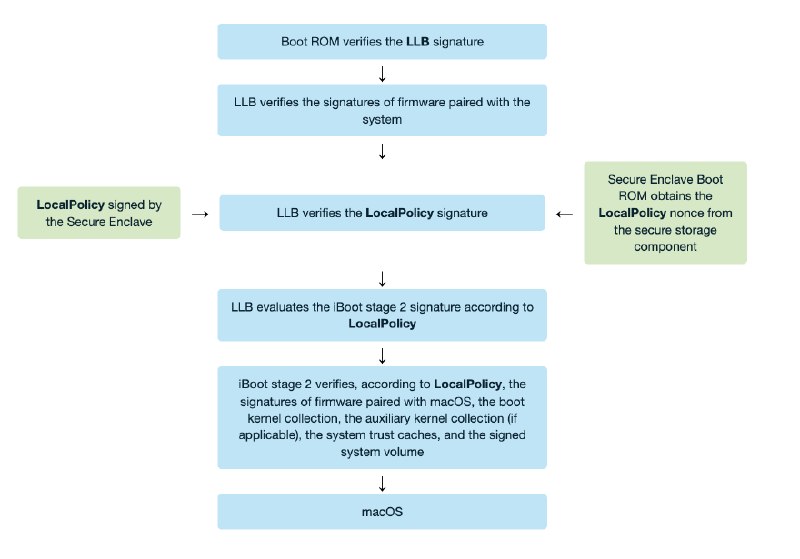
iBoot SMMU Bypass and Kernelcache Struct Forgery on Apple Silicon

Original text: “iBoot SMMU Bypass and Kernelcache Struct Forgery” — author not clearly listed, Ghost Wolf Lab (Jun 25, 2026). Code, tables and figures below are reproduced verbatim with attribution captions; Chinese text in the diagrams, code comments and table has been translated into English.

Executive Summary

Apple Silicon’s security model rests on a chain…

https://core-jmp.org/2026/06/iboot-smmu-bypass-kernelcache-struct-forgery/
  • 😱 4
  • 🔥 3
Post #3518 4.76K
From context_handle to type confusion: A Windows RPC Vulnerability Pattern

Original text: “From context_handle to type confusion” — k0shl, Whereisk0Shl (2026-06-26). The prose below is a paraphrase; all code listings, IDL descriptor bytes and crash dumps are reproduced verbatim with attribution captions.

Executive Summary

Context handles are one of the most common building blocks in Microsoft RPC. Inside rpcrt4 a context handle behaves like an…

https://core-jmp.org/2026/06/from-context-handle-to-type-confusion-windows-rpc-2/
  • 👍 4
  • 🔥 3
Post #3517 4.93K
IPV6_FRAG_ESCAPE
*
Linux LPE - Reliable Jail/Container Escape

exploit
  • 👍 12
  • 🔥 5
Post #3516 5.19K
ФРИИ и Metascan запускают совместный фонд для инвестиций в проекты в сфере кибербезопасности 🔐
Сделали сильный продукт, но сложно расти дальше? Не получается выстроить системные продажи, выйти в крупные компании или масштабировать бизнес?

Мы ищем B2B-проекты с готовым продуктом и помогаем не только привлечь инвестиции, но и пройти следующий этап роста.

Что получают команды:

— Инвестиции от 5 до 100 млн рублей
— Экспертиза Metascan и доступ к корпоративным клиентам
около 100 компаний, среди которых энтерпрайз, банки, ритейл
— Системная помощь в продажах и масштабировании
работа с трекерами ФРИИ, настройка процессов продаж, архитектурные ревью

ФРИИ – один из крупнейших венчурных фондов и акселераторов России.
Среди портфельных компаний Flowwow, ПравоТех, DocsinBox, Aimoto, PimSolution и др

Metascan – команда практиков в кибербезопасности и offensive security.

Если вы развиваете CyberSec-проект и готовы к следующему этапу роста:
👉 оставляйте заявку
  • 🔥 8
  • 👍 7
  • 😱 3
Post #3515 4.3K
Sleeping Beauty II: CFG, CET, and Stack Spoofing

Original textby Maor Sabag

Sleeping Beauty II: CFG, CET, and Stack Spoofing

A tale of CFG bitmaps, shadow stacks, and teaching an implant to sleep in places it was never meant to survive.

In Part I, we built StealthPalace: a Crystal Palace RDLL wrapper for Adaptix with IAT hooking and Ekko-style sleep obfuscation. It worked…

https://core-jmp.org/2026/06/sleeping-beauty-ii-cfg-cet-and-stack-spoofing/
  • 🔥 4
Post #3514 4.31K
Sleeping Beauty: Putting Adaptix to Bed with Crystal Palace

Original post by Maor Sabag

Sleeping Beauty: Putting Adaptix to Bed with Crystal Palace

Introduction

Adaptix C2 ships a default agent DLL. Out of the box, it’s a standard PE – it gets loaded into memory with RWX permissions everywhere, no IAT hooking, no sleep obfuscation, nothing fancy. If you’re doing red team work, that’s…

https://core-jmp.org/2026/06/sleeping-beauty-putting-adaptix-to-bed-with-crystal-palace/
  • 🔥 4
Post #3513 5K
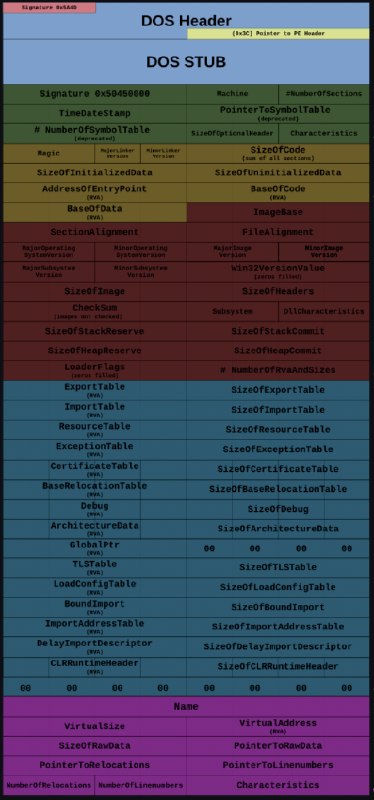
Portable Executables

Original text by Sp1d3rM

NTRODUCTION

One of the most famous file formats in computer history probably is the Portable Executable, popularly known as .exe. There is more to it than just being the binary file format of choice for Windows systems. In this chapter, we will deep-dive into what are portable executables? Where they live?…

https://core-jmp.org/2026/06/portable-executables/
core-jmp Portable Executables Deep dive into Windows PE file format—headers, sections, and loader mechanics. Explains how security products (AV/EDR) detect malware via static analysis: entropy, import hashes, section anomalies, and suspicious API patterns. Essential for red-team tradecraft…
  • 🔥 11
Post #3512 4.61K
From context_handle to type confusion: A Type Confusion Pattern in Windows RPC Servers

Original text: “From context_handle to type confusion” — k0shl, Whereisk0Shl (Jun 26, 2026). Code blocks and crash dumps below are reproduced verbatim with attribution captions.

Executive Summary

Windows RPC servers routinely expose several different context-handle types within the same interface — for example a generic open/close handle alongside a typed object handle. A context handle…

https://core-jmp.org/2026/06/from-context-handle-to-type-confusion-windows-rpc/
  • 🔥 1
Post #3511 4.98K
A 27-Year-Old Authentication Bypass in OpenBSD’s PPP Stack (CVE-2026-55706)

Original text: “A 27-Year-Old Authentication Bypass in OpenBSD’s PPP Stack” — Argus, Argus Blog (2026-06-16). Kernel source snippets and console output below are reproduced verbatim with attribution; the surrounding analysis, the attack-chain diagram and the proof-of-concept are original to core-jmp.org.

Executive Summary

OpenBSD’s synchronous-PPP layer contained a textbook length-confusion bug in its PAP (Password Authentication…

https://core-jmp.org/2026/06/openbsd-ppp-pap-authentication-bypass-cve-2026-55706/
  • 👍 3
  • 🔥 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →