TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3257 · Back to latest

Older Posts 20 shown
Post #3256 87
🔴 Hackers Abuse Stolen BigCommerce App Key to Steal Master of Malt Customer Data

Master of Malt reported a customer data breach after attackers allegedly compromised an application key linked to Ribon, a third-party BigCommerce app managed by Be A Part Of that identifies itself as a Fastr brand.

BigCommerce notified the retailer of the incident on September 18, 2026, prompting Master of Malt to reach out to affected customers within hours.

The company said attackers used the stolen Ribon application credential to access customer information stored in BigCommerce from 17:21 BST on September 13 to 21:12 BST on September 17, when the compromised key was revoked.
Post #3255 95
🔴 Critical MaxKB AI Agent Flaw Lets Prompt Injection Execute System Commands

A critical vulnerability in the MaxKB AI knowledge-base platform could let attackers exploit prompt injection and run operating system commands on vulnerable deployments, including directly on the underlying host in some configurations.

This flaw, tracked as CVE-2026-77521 and GHSA-f36j-f34j-h3rx, affects MaxKB versions up to and including 2.10.3-lts. The issue has received a maximum CVSS v3.1 score of 10.0 for public or embedded assistants that can be accessed without authentication. The patch for this vulnerability is included in MaxKB version 2.10.5-lts.
Post #3254 104
🔴 Linux BambooToken Malware Uses MQTT C2 for Remote Shell Access and File Exfiltration

A Linux variant of the BambooToken backdoor uses MQTT as its command-and-control channel, enabling operators to profile compromised hosts, execute shell commands, and transfer files through broker-mediated topics.

Analysis of a statically linked x86-64 ELF sample shows that its configuration, task routing, and network payloads are obfuscated with separate XOR routines.

The examined sample, SHA-256 bf0681e43f51e98fe7ec24bf73a43facc66b0feb325a3a835f8f01b2861b926e, is a 2.4 MB stripped C++ executable.
Post #3253 112
🔴 Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal

A malicious npm package named "indexed-btree" has been observed hiding its malicious behavior within application code rather than using lifecycle scripts, indicating that threat actors are likely shifting tactics in response to recent security controls.

"Indexed-btree is a malicious npm package mimicking the legit sorted-btree package, an ordinary B-tree/indexing utility," Checkmarx said. "Unlike the common attacks we've seen in the supply chain space, this package does not rely on preinstall / postinstall at all. Instead, it runs entirely from application code at runtime."
Post #3252 104
🔴 New Windows Defender zero-day blocks Microsoft antivirus updates

Over the weekend, security researcher Abdelhamid Naceri (also known as Nightmare Eclipse) released another Microsoft Defender zero-day exploit that blocks antivirus updates.

Naceri named it BigDiskBuster and said it is similar to another Defender zero-day known as UnDefend, which he released in April and that allowed standard users to block definition updates.

The security researcher added that BigDiskBuster works on all supported Windows versions and that it needs to run in the background to block Defender updates.
Post #3251 90
🔴 SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing

The threat actor known as SideCopy has been observed using spear-phishing lures to target academic institutions in India, expanding their strategic focus beyond government entities.

"SideCopy campaign operations typically initiate through spear-phishing campaigns that leverage the abuse of mshta.exe to execute malicious scripts and circumvent standard security protocols," Trellix researchers Boggavarapu R S S Srinivas Gupta and Ravishankar N C said in a technical report.

"This delivery mechanism facilitates the deployment of a remote access trojan (RAT), which serves as the central pillar of their offensive infrastructure."
Post #3250 97
🔴 WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session

A new flaw in WordPress core let an anonymous visitor leave a comment that planted a hidden script on the page. If a logged-in administrator later opened that page, the script could run code on the site's server.

WordPress fixed the flaw, tracked as CVE-2026-93485 and dubbed "Comment2Shell," on September 17 in version 7.1.1 and told site owners to update right away. There is no sign it has been used in attacks, and it is not on the U.S. government's list of actively exploited software flaws.
Post #3249 101
🔴 Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a now-patched security flaw impacting Zyxel GS1900 series switches to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation.

The vulnerability, tracked as CVE-2026-7273 (CVSS score: 8.8), is a stack-based buffer overflow vulnerability that could result in arbitrary operating system (OS) command execution.

"A stack-based buffer overflow vulnerability in the CGI program of the Zyxel GS1900 series switch firmware could allow a LAN-based, unauthenticated attacker to exploit the flaw and potentially execute OS commands via a crafted HTTP request," Zyxel said in an advisory released in June 2026.
Post #3248 107
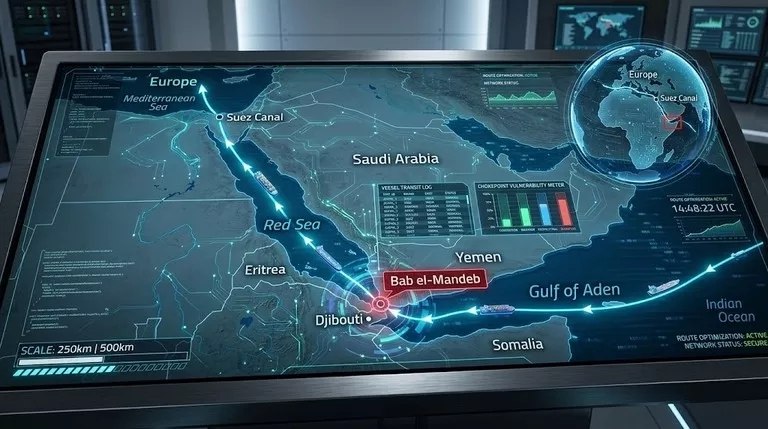
🔴 Bab el-Mandeb: The New Digital Chokepoint Threatens Trade

The Red Sea crisis is no longer just about missiles, drones, and merchant ships. Now, with the Houthis' growing ability to compromise the safety of shipping, Bab el-Mandeb is also becoming a digital flashpoint, where maritime security, telecommunications, satellite navigation, and strategic infrastructure converge in a single risk scenario. By mid-September 2026, the situation had returned to pressure: a Reuters reconstruction of Ansar Allah's military evolution revealed that the movement now possesses the capacity to exert pressure on a much larger scale, using missiles, drones, and other systems. However, geography makes the issue even more salient: Bab el-Mandeb connects the Gulf of Aden to the Red Sea and, through Suez, to European and global trade routes.
Post #3247 116
🔴 Is the quantum slow in arriving? The US is offering $215 million in prizes

The U.S. Department of Energy has launched the Quantum Genesis Q competition with an anticipated funding of up to $215 million. Participants are challenged to build a fault-tolerant quantum computer with at least 100 logical qubits, capable of performing hundreds of millions of operations with error correction. The DOE expects to obtain not just another experimental processor with a large number of physical qubits, but a system suitable for solving real-world scientific problems.
Post #3246 134
🔴 PDF is no longer enough: now AI can turn a scientific article into an agent

The researchers presented Paper2Agent, a system that transforms a standard scientific article into a functioning AI agent. Instead of reading a PDF, searching for source code, and manually configuring programs, the researcher can ask a question in natural language, ask for a calculation to be reproduced, or apply the described method to new data. The authors consider this approach a potential new way to publish computational research, although the system does not currently replace traditional articles.

Paper2Agent doesn't work like a chatbot simply loaded with the article text. The system collects the publication itself, additional materials, datasets, source code, and ready-made workflows, then transforms the authors' methods into a set of executable tools. As a result, the AI ​​can not only summarize the content, but also perform the calculations described in the study.
Post #3245 176
ClickFix Campaign Deploys Node.js Malware With Dynamic Polygon C2 Discovery

Security researchers have uncovered ChainScript, a previously undocumented Node.js remote-access trojan that uses the Polygon blockchain to dynamically locate its command-and-control (C2) infrastructure.

🔗 Read More
Post #3244 145
🔴 BRUKER CORPORATION — METAENCRYPTOR RANSOMWARE CLAIM

Threat actor Metaencryptor claims Bruker Corporation (a Massachusetts-based scientific and analytical instruments company) as a ransomware victim.

The underground listing alleges:

* A Metaencryptor leak-site victim entry targeting Bruker
* Impact framed against US scientific / tech manufacturing systems
* No confirmed encryption volume, exfiltration inventory, or ransom demand published in open sources at review time
Post #3243 106
🔴 Meta’s Muse is outpacing ChatGPT’s early mobile launch

Meta’s latest AI app, Muse, could be the social giant’s next major hit, new data suggests. According to just- released estimates from market intelligence provider Apptopia, Muse’s app on mobile devices has been downloaded more times during its first 12 days on the market than ChatGPT was in the 12 days after its debut. (This data compares the U.S. and Canada markets only.)

Muse also has more daily active users than ChatGPT had at the time, the firm found.
Post #3242 81
🔴 THREAT ACTOR CLAIMS SALE OF ROCKWELL COMPACTLOGIX ACCESS IN ARIZONA

A threat actor is advertising what they claim is unauthorized remote access to a Rockwell Automation CompactLogix industrial controller located in Gila Bend, Arizona.

The underground listing alleges:

* Target device: Rockwell Automation 5069-L330ER/A (motion-capable CompactLogix)
* Full read/write access to I/O tags and diagnostic data
* Access via a VNC surface on port 5900 (credentials required)
* Network path described as Verizon Business
* Asking price: 30 XMR via escrow
Post #3241 65
🔴 Rust Team Members and Popular Crate Owners Targeted via Video Calls

The Rust project warned last week that an ongoing social engineering campaign is targeting Rust-lang team members and the owners of popular crates to hijack developer credentials and deploy malicious packages.

The crates.io team and the security response working group issued the warning. According to the alert, attackers lure targets into video calls under the guise of job offers or contract opportunities.

Once on the call, the target is tricked into installing software under the pretext of a missing audio codec or executing malicious code pasted to their clipboard.
Post #3240 79
🔴 A BYD Shark 6 Hack Shows the Risks of Connected Cars

A BYD Shark 6 was remotely hacked, exposing vehicle controls, location tracking and cabin audio, raising serious connected-car security concerns.

A journalist drove a BYD Shark 6 down a country road outside Canberra while a hacker sitting on the shoulder killed the headlights with a keystroke. That’s not a hypothetical. It’s what happened during a two week test by Four Corners and a cybersecurity researcher named Dan Hreszczuk.

Hreszczuk runs Fortify Labs in Canberra and specialises in car security. His job was simple: find out what BYD, or anyone with access to BYD’s systems in China, could see and do to the vehicle remotely. He didn’t expect it to be quick.
Post #3239 77
🔴 CrowdSec Confirms Source Code Stolen in Supply Chain Attack

French cybersecurity firm CrowdSec has confirmed that approximately 300 private and public repositories were compromised and source code was stolen from them.

The company provides open source, crowdsourced threat intelligence, including a lightweight security engine to detect and block attacks targeting servers, networks, and applications.

Last week, the French outfit learned that source code had been stolen from its GitHub repositories in May 2026.

CrowdSec has confirmed the report, noting that both private and public code was exfiltrated, and that roughly 300 repositories were affected, including approximately 170 private ones.
Post #3238 79
🔴 CHINA MILITARY / DEFENSE EQUIPMENT DATA FOR SALE — ~127 FILES / ~300MB CLAIM

A threat actor is advertising a sensitive military-data package covering Chinese defense manufacturing, aerospace, electronics, and related industrial activity — about 127 files totaling roughly 300MB, listed for around $4,500.

The underground listing alleges material such as:

* J-10C fighter aircraft technical details
* PL-15E / PL-10E air-to-air missiles, CM-400AKG/B air-to-ground missile, GB1 laser-guided bomb
* Technical proposals for Sky Dragon 50 and 100 missile-defence systems
* Z-10ME attack helicopter material
* CETC CSC-005H UAV system, XY-I UAV, and CETC anti-UAV systems
* UAV-borne KZ100 electronic-intelligence and jamming equipment
* CETC YLC-8E and YLC-18 surveillance radar material
* Broader air-defence / anti-UAV solution documentation
Post #3237 91
🔴 Huawei challenges Nvidia: one million AI chips connected in a single supercomputer

Huawei decided to attack Nvidia's lead not with a single record crystal, but with the scale of the entire computing system. At Huawei Connect 2026, the company previewed the launch of two Ascend 960 accelerators and revealed the architecture that will unite up to a million AI processors in a single cluster.

The Ascend 960DT is now expected to be available in the first quarter of 2027, three quarters earlier than originally planned, and the Ascend 960PR in the third quarter, one quarter earlier. Huawei plans to refresh the lineup annually: the 960 will be followed by the Ascend 970 in 2028 and the Ascend 980 in 2029.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →