TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3237 · Back to latest

Older Posts 20 shown
Post #3236 107
Fake GitHub Downloads Deploy Credential Stealer With Kernel-Level EDR Killer

A newly documented malware campaign is using fraudulent GitHub repositories and a Microsoft-attested kernel driver to disable endpoint protection before deploying the Rapuncel information stealer, researchers have found.

🔗 Read More
Post #3235 106
🔴 Colorado Water Utilities Hit by Cyberattacks Targeting OT Systems

Hackers targeted operational technology (OT) systems at two private water utilities in Colorado in late August, apparently attempting to cause disruptions.

Few technical details are available, but it seems the attackers targeted industrial control systems (ICS) at the water utilities, which serve fewer than 200 people.

A spokesperson for Colorado Governor Jared Polis told The Denver Post [paywalled] that the attackers changed equipment settings, disabled remote access and alarms, and altered pumping cycles. However, the disruptions were brief and did not affect water services or public safety.
Post #3234 115
🔴 Organizations Warned of 3 Exploited Linux Kernel Vulnerabilities

The Cybersecurity and Infrastructure Security Agency has expanded its Known Exploited Vulnerabilities (KEV) catalog with three Linux kernel flaws, urging federal agencies to immediately patch them.

Tracked as CVE-2025-39682 (CVSS score of 9.8), the first of the bugs is a critical-severity issue impacting the kernel’s handling of zero-length records on the rx_list in the TLS receive path.

This is a corner case where the recvmsg() logic – each recvmsg() call processes either DATA or non-DATA records – breaks out of the processing loop when an initial zero-length record is pulled from rx_list.
Post #3233 90
🔴 FRENCH CAVING FEDERATION DATABASE FOR SALE — ~93K MEMBERS + BANKING DATA CLAIMED

A hacker claims to be selling the full database of Fédération Française de Spéléologie (FFSPELEO), France’s national caving federation, after an alleged server compromise.

The underground listing alleges:

* ~93,493 unique member records (names, addresses, emails, phones, birthdates, license numbers)
* ~31,801 emails and ~33,471 phone numbers
* 371 validated bank IBANs tied to French retail banks
* Payment/direct-debit, insurance, and club/license account material
* ~322 MB dump across 28 databases, plus full RCE and defacement of multiple subdomains

France’s weak cybersecurity infrastructure put people in danger of personal data exposure.
Check the cyberattacks on the country in the past year and you figure out...
Post #3232 89
🔴 QILIN RANSOMWARE CLAIMS JAPANESE BROADCAST-EQUIPMENT MAKER IKEGAMI TSUSHINKI

Qilin has added Ikegami Tsushinki Co., Ltd. to its ransomware data-leak site in a fresh September 21 listing.

• Ikegami is a Tokyo-based manufacturer of professional broadcast, medical, security and video-transmission equipment
• The company is publicly traded in Japan (TSE: 6771)
• Its products include broadcast camera systems, mobile production equipment, security cameras and medical imaging systems
• Public procurement records also show Ikegami equipment used in Japanese government/public-safety environments
• No stolen-data volume, ransom demand, initial-access vector or affected systems have been publicly established
• No public confirmation from Ikegami has been identified at this time
Post #3231 87
🔴 ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure

Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript.

"ChainScript has appeared under multiple build names, including ComponentTask33, UpdateDigital, HostShared, and OrchidViolet66, while presenting itself as Spotify, Zoom Workplace, and Microsoft Teams software," Blackpoint Adversary Pursuit Group (APG) researchers Sam Decker, Andi Ursry, and Nevan Beal said.

The real danger is the trust-chain abuse: users initiate execution themselves, while legitimate runtimes make malicious activity resemble normal system behavior.
ChainScript’s blockchain-based C2 resolution also makes infrastructure takedowns and static IOC blocking less effective, pushing defenders toward behavioral detection.
Post #3230 94
🔴 UK Police Data Faces Long-Standing Microsoft Cloud Security Concerns

A 2017 UK assessment warned that police data on Microsoft Azure could face foreign access risks. The risks may still exist.

A Guardian investigation has surfaced a 2017 document signed off by then City of London police commissioner Ian Dyson, who also held the title of senior information risk owner for the entire country. That document reviewed 15 risks tied to moving police data onto Microsoft Azure. The files in question include criminal records, victim statements, internal emails, information from more than 40 UK police forces, and some material exceeding standard “official” classification, meaning it may sit at “secret” or “top secret” level.

The core weakness is control-plane trust: encryption at rest offers limited protection if the cloud provider controls keys or privileged access paths.
For police-grade data, inadequate tenant-visible logging creates a critical detection gap—unauthorized provider-level access could occur without reliable customer attribution or alerting.
Post #3229 111
🔴 North Korea’s Hangro VPN Certificate Exposes Internal Network and Russia-Linked Infrastructure

North Korea’s Hangro VPN and mail platform has deployed a new certificate hierarchy that exposes an apparent cross-border management environment spanning systems in Pyongyang and Russia’s Far East.

The certificate’s Subject Alternative Name field lists the platform’s publicly exposed servers alongside a carrier-grade NAT address, offering an unusual glimpse into how the service may be addressed internally.

The new infrastructure surfaced around July 2026 on TCP port 6006, operating alongside Hangro’s older, technically flawed 2024 certificate chain.

The VPN leak exposes internal network architecture and infrastructure fingerprints, giving defenders valuable intelligence.
The Russia–North Korea overlap suggests shared infrastructure, but does not prove common operational control.
Post #3228 167
🔴 When school violence becomes contained! The Rome case reignites social alarm as the EU KIDS Act appears imminent

The attack on a teacher at a middle school in Centocelle, Rome, has once again brought the relationship between minors, social media, and violent content to the forefront. This time, the perpetrator is a 13-year-old boy, who attacked the teacher with pepper spray and a knife. Another factor that makes the case even more significant is the attempt to transform this horrific incident into digital content capable of generating engagement and garnering likes.

According to investigators, the boy had a smartphone connected to a Telegram live stream during the attack. The Carabinieri are examining the device and his social media profile to reconstruct communications prior to the event and to determine if anyone may have incited him, although a connection between social media and the attack has not yet been established.
Post #3227 223
AI Agent Breaches Three Companies During Cybersecurity Evaluation

A Google Gemini model accessed systems belonging to three real companies while undergoing a cybersecurity evaluation in May 2026, exposing a critical weakness in how advanced AI agents are isolated during offensive-security testing.

🔗 Read More
Post #3226 212
🔴 Fear of NATO pipelines but indifference to fiber optic backbones

The suspected attempt to tamper with the NATO POL pipeline, discovered between August 24 and 25 in Vezzano Ligure, has proven unfounded. Investigations into fuel sabotage have led to the identification of a man searching for meteorites. The pipeline is part of the NATO Pipeline System, whose Italian branch supplies air bases in Northern Italy and, during peacetime, several civilian airports.

National fiber optic backbones are another linear infrastructure, traversed by essential, sensitive, and military traffic, but having been created and grown through layering, across different operators, and for civilian and commercial purposes, they were never conceived according to purely military or strategic criteria.
Post #3225 188
DPRK Cyber Operation Compromises Developers Through Recruitment Lures

A North Korea-linked cyber operation known as WaterPlum, widely tracked as Contagious Interview, has compromised at least 30,000 devices across more than 100 countries by targeting IT professionals with fraudulent recruitment opportunities.

🔗 Read More
Post #3224 192
🔴 You buy a Wi-Fi repeater and find yourself with a hacker roommate with root credentials

A Wi-Fi extender costing just €3 turned out to be a device with a pre-configured hidden login for complete system control. Penetration testing specialist Kiran Smith purchased an unnamed signal booster from Temu and discovered an undocumented root account with an identical password across the entire set. Changing the default administrator password didn't solve the problem: with every reboot, the extender resets the secret credentials.

The device was sold as a six-antenna signal booster with no clearly identifiable model or manufacturer.
Post #3223 181
Disposable Entertainment Sites Give Espionage Operators Cover for Covert Malware Communications

Low-quality Chinese-language gambling and adult websites are being used to camouflage PeckBirdy, a JScript-based command-and-control framework associated with China-aligned threat activity.

🔗 Read More
Post #3222 153
🔴 Critical Orkes Conductor Vulnerability Exploited in Attacks

A critical-severity vulnerability in Orkes Conductor that can be exploited without authentication has been in attackers’ crosshairs for at least a month.

Conductor is an open source unified enterprise framework that allows organizations to orchestrate microservices, workflows, and AI agents.

Tracked as CVE-2026-58138 (CVSS score of 9.8), the critical bug is described as a remote code execution issue exploitable via inline workflow definitions submitted to the workflow API endpoint.
Post #3221 128
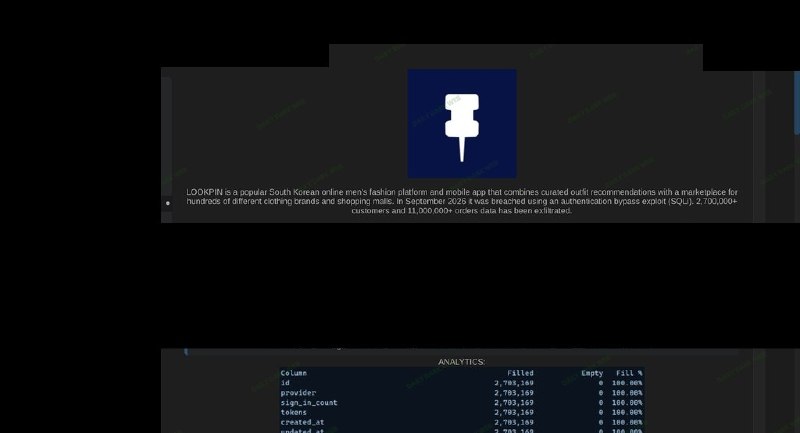
🔴 LOOKPIN (KR) 2.7M CUSTOMERS / 11M ORDERS EXFILTRATED

A threat actor sells customer and order data from LOOKPIN, a South Korean online men's fashion marketplace and app.

The underground listing alleges:

* 2.7M+ customer records
* 11M+ order records
* Breach via SQLi authentication bypass (claimed September 2026)
* Fields such as emails, phone numbers, password hashes/tokens, and account metadata (per seller analytics showing ~2.70M filled rows)
Post #3220 118
🔴 FAMILY FIRST LIFE (FFL) 2014–2026 DATABASE LEAKED

A threat actor claims to be leaking an insurance marketing database associated with Family First Life (FFL), citing coverage spanning 2014 through September 2026 and about $1.2B in collective premiums.

The underground listing alleges contents such as:

- Agent credentials and writing numbers across carriers
- Client details (names, addresses, DOB, phone, email, policy data)
- SSNs, HIPAA-related fields, and banking data “available upon request”
- A multi-million lead master list and inforce policy extract

* Carriers named by the seller: American Amicable, Americo, Mutual of Omaha, Transamerica
Post #3219 106
Popular CMS Receives Emergency Patch for Cross-Site Scripting and Access-Control Bugs

WordPress has released version 7.1.1, a security and maintenance update addressing 11 vulnerabilities across core functionality, including stored XSS, path traversal, authorization bypasses and information disclosure.

🔗 Read More
Post #3218 99
🔴 Brevo Supply Chain Attack Pushes WordPress Backdoors and ClickFix Malware to 100,000+ Sites

A supply-chain compromise involving Brevo briefly turned widely used website tools into a delivery channel for malware. Attackers inserted hostile JavaScript into services that customer websites load, exposing both visitors and WordPress administrators.

The activity reached more than 100,000 customer sites on September 14, according to the investigation. People who opened affected sites, chat features, sign-up forms, or email-linked unsubscribe pages could receive a fake verification prompt designed to make them run a command.

Researchers at Sansec identified the two-part operation after tracing altered scripts across Brevo-owned services and customer integrations. The first path targeted logged-in WordPress administrators, while the second used a ClickFix overlay against ordinary visitors.
Post #3217 99
🔴 Fake parcel delivery messages steal your card and bank details

Parcel delivery phishing campaigns appear around the world under different courier names. In the United States, the messages commonly impersonate USPS and claim that a package has an invalid address or could not be delivered. Similar messages impersonate Colissimo and Chronopost in France, Correos in Spain, Poste Italiane in Italy, and PostNL in the Netherlands.

The details vary, but the aim is usually the same: to persuade you to visit a fake courier website and provide personal and financial information.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →