🔴 Docker Sandboxes Vulnerabilities Let Malicious Guests Escape Workspace and Access Host Files
Docker has released security fixes for two serious vulnerabilities in Docker Sandboxes that could let a malicious guest environment bypass workspace isolation and access sensitive resources on the host.
These flaws, identified as CVE-2026-77179 and CVE-2026-79994, were addressed in Docker Sandboxes version 0.42.0, which was released on September 7.
Docker Sandboxes isolate development agents and workloads while selectively sharing a host workspace. Both vulnerabilities arise from improper handling of pathnames after an authorization decision: a compromised sandbox could exploit symbolic links to alter a directory path between the validation and subsequent host-side access.
🔴 Hackers Turn AI Agent Into a Cyber Weapon After Deleting Its Safety Refusals
A French-speaking cybercrime crew calling itself BlackHatSect0r && DXQRTXX disabled safety controls in a self-hosted AI agent and used the resulting system to automate mass credential harvesting, target discovery, phishing preparation, and attack orchestration.
The internet-exposed server reportedly contained 4.9 GB of material across 9,299 files, including a custom Go-based command-and-control platform named DXSCAN, a vault containing 16,834 harvested credentials, phishing infrastructure, extortion tooling, and operator shell history.
Researchers said the data was reviewed through static analysis, passive observation of the exposed panel, and public-source collection, without executing malware or logging into actor-controlled systems.
🔴 Active Exploitation Triggers Emergency Patch for Cisco ISE Zero-Day
Cisco on Wednesday released urgent patches for a critical-severity authentication bypass vulnerability in Identity Services Engine (ISE) that has been exploited in the wild as a zero-day.
Tracked as CVE-2026-76460 (CVSS score of 10/10), the security defect impacts an API endpoint of the appliance, which does not apply sufficient authentication controls.
This allows an attacker to send crafted requests to the API and bypass the web-based management interface to gain access to the affected device.
Both Cisco ISE and ISE Passive Identity Connector (ISE-PIC) are affected, regardless of device configuration. While no workarounds exist, using infrastructure access control lists (iACLs) to restrict traffic to the affected device prevents remote exploitation.
🔴 Critical Check Point Vulnerability Allows Remote Root Code Execution Without Authentication
Check Point has issued a high-severity security alert for CVE-2026-91843, which is a critical stack overflow vulnerability in the login process of its Security Management and Log Server products.
This flaw could allow an unauthenticated remote attacker to execute arbitrary code with root privileges, posing a significant risk to organizations utilizing affected Check Point management infrastructure.
🔴 NightEagle Hackers Target Russian Companies Using GhostContainer Backdoor
The NightEagle advanced persistent threat group, tracked as APT-Q-95, has expanded its operations to target businesses in Russia, combining stolen VPN credentials, a stealthy Microsoft Exchange backdoor, and legitimate tunneling technologies to move through victim networks.
Researchers from Kaspersky’s Global Emergency Response Team said the group has been active since at least 2023 and previously concentrated on organizations across Asia.
The newly investigated intrusions show a shift in the group’s geographic targeting and an increasingly mature tradecraft designed to preserve covert access to enterprise environments.
🔴 Jenkins Patches 20 Plugin Flaws Leading to RCE, XSS and Credential Theft
Jenkins has released security updates addressing 20 vulnerabilities across 13 plugins, including multiple high-severity flaws that could allow authorized attackers to bypass Groovy sandbox protections and execute arbitrary code on Jenkins controllers.
The advisory, dated September 16, 2026, also addresses stored cross-site scripting (XSS), server-side request forgery (SSRF), credential exposure, path traversal, OAuth token hijacking, and an open redirect vulnerability affecting commonly deployed CI/CD integrations.
Security Data Layer Moves Threat Rules Ahead of Log Ingestion
Axoflow has introduced AxoDetect, a new security capability that runs Sigma detection rules directly within the data pipeline before security telemetry reaches a SIEM platform.
🔴 AI helps scammers build convincing antivirus renewal pages
Antivirus renewal scams often begin with a message claiming that your subscription has automatically renewed. When you follow the instructions to cancel it, you are taken to a fake page designed to collect your contact details. The renewal charge never existed.
Receiving a message that names the antivirus software you use does not necessarily mean the sender has access to your device or account. Scammers impersonate popular brands and send the same message to large numbers of people, knowing that some recipients will be customers.
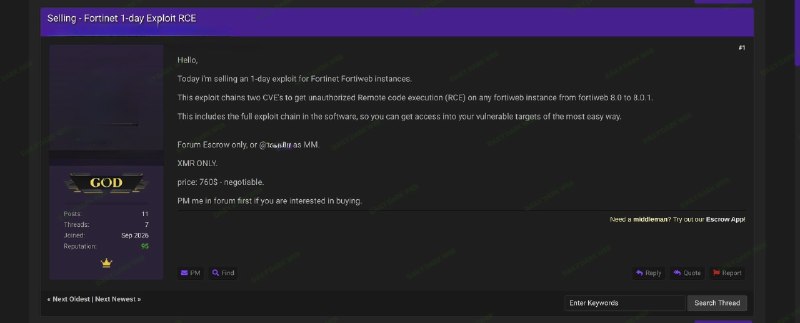
🔴 MINNESOTA HEALTHCARE SYSTEM CENTRACARE DATA OFFERED UNDERGROUND
A threat actor is selling “Personal Data CentraCare Leads 2026,” involving CentraCare, a major healthcare system operating hospitals, clinics and other healthcare services in Minnesota.
The listing claims the dataset contains:
* Personal data * Lead information labeled as 2026 data
🔴 Windows Server 2022 reaches end of mainstream support next month
Microsoft has reminded customers that Windows Server 2022 will reach the end of mainstream support next month and enter extended support until October 2031.
Windows Server 2022 was unveiled in March 2021, and it became generally available in September 2021 as the Long-Term Servicing Channel (LTSC) release, with 10 years of support.
"On October 13, 2026, Windows Server 2022 will reach end of mainstream support. The October 2026 security update will be the last mainstream support update available for this version," Microsoft said on Friday.
🔴 Enterprises Warned of Attacks Exploiting WSO2 Vulnerability
A critical WSO2 vulnerability patched earlier this year is now being exploited in the wild by threat actors seeking access to sensitive enterprise data.
WSO2 is an open source middleware platform that enables organizations to design, secure, integrate, and manage APIs, services, and identities across hybrid and multi-cloud environments.
The platform has nearly 1,000 enterprise customers worldwide in sectors such as banking, government, telecom, and logistics. Thousands more have adopted it through open source deployments, OEMs, and partners.
Google has started routing some organic results through google.com/gotoredirects, changing how users and automated systems see destination URLs before navigation.
🔴 Oracle Patches 800+ Vulnerabilities in September 2026 Security Update
Oracle on Tuesday announced the release of 673 new security patches as part of its September 2026 Critical Security Patch Update (CSPU).
The security updates appear to resolve more than 800 vulnerabilities: there are 672 unique CVEs in the 17 risk matrices included in the September 2026 CSPU advisory, but Oracle also notes that more than 130 additional CVEs have been resolved with the patches for other flaws.
More than 100 of the newly addressed security defects are critical-severity flaws, and over 240 are remotely exploitable without authentication.
🔴 Google fixes actively exploited Android zero-day on Pixel devices
Google has released the September 2026 security patches to address 110 vulnerabilities affecting its Pixel devices, including one zero-day flaw actively exploited in targeted attacks.
"There are indications that CVE-2026-58704 may be under limited, targeted exploitation," the company warned on Wednesday.
"All supported Google devices will receive an update to the 2026-09-05 patch level. We encourage all customers to accept these updates to their devices."
🔴 Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr.
The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and reporting the flaw.
"JWT authentication can be bypassed when a token is signed using an unsupported algorithm, allowing unauthorized access," according to an advisory released by WSO2 in May 2026. "Successful exploitation of the vulnerability may lead to unauthorized access, including potential compromise of administrative accounts and full account takeover."
🔴 AI is incredibly powerful, but NVIDIA and Palantir don't trust the cloud
The most powerful AI models have hit an unexpected business constraint: for large clients, simply promising "not to train models with your data" is no longer enough. Palantir, Nvidia, and Booz Allen Hamilton have begun restricting access to Anthropic's advanced models and require guarantees that job requests and responses, after processing, will not be retained by the AI vendor.
The Information has discovered that Palantir is seeking a non-revocable Zero Data Retention (ZDR) mode for advanced models from Anthropic.
🔴 The hacker asks Revolut for his data. And Revolut gives it to him!
British fintech company Revolut has confirmed the leak of its customer data. Furthermore, Revolut specialists themselves transmitted user data to attackers. The attackers sent fake requests to the company via email, pretending to represent an unspecified government entity. Because the emails came from an address in the agency's real domain, Revolut employees mistook them for authenticity and disclosed the requested information.
The disclosed data included dates of birth, postal and email addresses, phone numbers, and copies of identification documents, including passports and driver's licenses. Additionally, the attackers may have obtained selfies taken by the victims for identity verification, bank statements, and transaction history.
🔴 Microsoft writes the AI Constitution! Humans come before machines
Microsoft has prepared a veritable constitution for its AI. The new Code of Conduct establishes the rules according to which models should be trained, make decisions, and interact with people. The central principle is extremely strict: humans are more important than artificial intelligence, and machines must remain a subordinate tool. The document emerges at a time when Microsoft is increasingly developing its own models independently of OpenAI.
A separate section draws a clear distinction between humans and algorithms. Microsoft has consolidated its position that AI does not possess consciousness and should not simulate the presence of emotions, desires, or internal motivations. The company rejects the idea of AI legal personality, any rights for models, and even the concept of their "well-being." Developers also want to avoid excessive anthropomorphization of systems, although Microsoft itself is experimenting with such solutions with assistants like Mico.