TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3177 · Back to latest

Older Posts 20 shown
Post #3176 135
🔴 GENTLEMEN RANSOMWARE GROUP ADDS 42 NEW VICTIMS

The Gentlemen ransomware group has published a major new wave of victims spanning healthcare, aviation, energy, manufacturing, education, food, finance and infrastructure organizations across multiple countries.

Notable names include:

* 🇨🇦 Air Canada
* 🇨🇴 Ecopetrol
* 🇮🇩 Pertamina
* 🇺🇸 AnMed
* 🇺🇸 Nutex Health
* 🇺🇸 Safeware
* 🇺🇸 Peachtree Group
* 🇺🇸 Cedars Foods
* 🇺🇸 Wada Farms
* 🇺🇸 CRB Group
* 🇮🇳 BGR Energy Systems
* 🇯🇵 Sarku Japan
* 🇯🇵 Tentac
* 🇧🇬 Apteki Mareshki
* 🇩🇪 MedSkin Solutions Dr. Suwelack AG

The leak site also lists dozens of additional organizations across Europe, Latin America, Asia and North America.

Some of the more significant claims include:

* Ecopetrol — 2TB released
* AnMed — 2TB released
* Pertamina — 1.2TB+ claimed, including HR, employee, banking, tax, legal and SCADA-related material
* Air Canada — 51,409 “critical files” claimed
Post #3175 95
🔴 FLORIDA DMV DATA LEAK — SHINYHUNTERS CLAIMS 52GB+ RELEASED

ShinyHunters has updated its leak-site entry for the State of Florida DMV, claiming negotiations failed and that more than 52GB of compressed data is now available for download.

This follows a breach that Florida officials have already confirmed.

FLHSMV says the incident was discovered on September 4 and involved compromised credentials belonging to a Plant City Police Department user that had been improperly stored on a personal electronic device. Officials say the unauthorized access was quickly contained and is no longer ongoing.

ShinyHunters has separately claimed access to Florida driver and vehicle information and is now presenting a 52GB+ archive on its leak site.
Post #3174 88
🔴 471,000 LEDGER CUSTOMER RECORDS OFFERED FOR $20,000

A threat actor sells a 2026 database belonging to Ledger, the French cryptocurrency hardware-wallet company.

The hacker claims approximately 471,000 records containing:

* Email addresses
* First and last names
* Physical addresses
* Phone numbers

The database is being offered for $20,000.
Post #3173 85
🔴 CenterPoint Energy confirms customer data stolen in cyberattack

CenterPoint Energy disclosed a breach compromising some customers’ personal information after an attacker leaked data stolen from the utility company.

An investigation started after the company discovered an online post from a threat actor claiming to have stolen 7.49 million records.

CenterPoint Energy is a Houston-based public utility company that provides electric and natural gas services and operates power generation facilities.
Post #3172 82
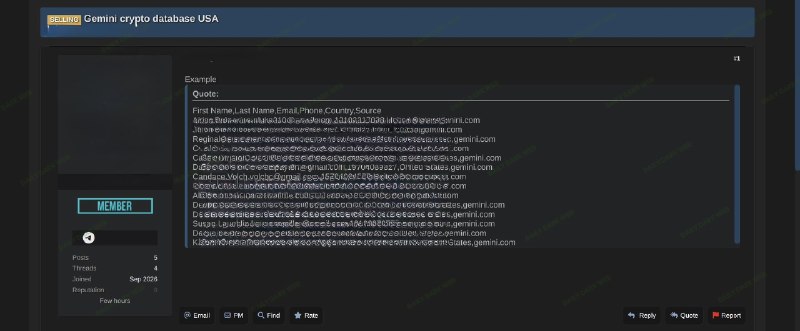
🔴 GEMINI CRYPTO CUSTOMER DATABASE OFFERED FOR SALE

A threat actor is selling a customer database belonging to Gemini, the U.S.-based cryptocurrency exchange.

The exposed data includes:

* Full names
* Email addresses
* Phone numbers
* Location data

The seller claims the records primarily belong to users in the United States.
Post #3171 92
Malicious Markup Hidden in Messages Can Expose Archived Conversations

Security researchers Denis and Aleksander Rostilov of ExPatch discovered a stored cross-site scripting vulnerability in the HTML export functionality of Telegram Desktop. The issue allowed malicious JavaScript to be embedded in a message and executed later when an exported conversation was opened in a browser.

🔗 Read More
Post #3170 81
🔴 $1 Million Sandbox Challenge Uncovers Linux Kernel Flaws

A two-week focused sandbox bug-bounty program resulted in 1,285 filings, but none that could access customer data.

The Vercel sandbox, a Firecracker‑based microVM environment, is an isolation tool for untrusted AI‑agent code. For two weeks (August 18 until September 1), Vercel operated a focused bug-bounty program with a $1 million reward pot. It called the program a ‘challenge’ – a challenge to HackerOne hackers (black box targeting) and Trail of Bits engineers (white box targeting) to escape the sandbox.
Post #3169 83
🔴 PAKISTAN DEFENSE PRODUCTION DATA FOR SALE — NAVY AND INTERNATIONAL DEFENSE INTELLIGENCE CLAIMED

A threat actor is advertising a 670MB dataset originating from Pakistan’s Directorate General Munitions Production, under the Ministry of Defence Production.

The seller claims the archive contains:

* Confidential email-channel data
* Pakistan Navy information
* Internal DGMP documents
* Pakistan–Türkiye–China defense cooperation material covering 2025–2035
* Information related to a U.S. arsenal
* Internal China–Pakistan Economic Corridor documentation
Post #3168 80
Eight Out of Ten Local Company Sites Show Security Weaknesses

A cybersecurity study of 102 publicly accessible sites operated by Singapore-based businesses found that 80.4% contained at least one identifiable security weakness, while one-third were classified as high or critical risk.

🔗 Read More
Post #3167 84
🔴 The Great AI Comedy: First They Plundered the Internet, Now They Accuse the Chinese of Stealing

Experts from the U.S. Cybersecurity and Infrastructure Protection Agency ( CISA ), the NSA , and the FBI have stated that Chinese AI companies are large-scale distilling of American AI models to train their own systems. Billions of tokens and millions of requests to Claude, GPT, Gemini, and Grok are being discussed. Almost simultaneously, Anthropic experts revealed details of seven such campaigns targeting Claude. The largest of these is linked to Alibaba, which sent over 151 million requests to the models from May to July 2026.

Distillation itself is a common learning method, in which a more powerful model acts as a "teacher" and its responses are used to train a younger model. However, American agencies claim that DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI are applying this technique without the permission of the American companies and on a large scale.
Post #3166 78
🔴 DDRop Attack Forces Intel TDX Confidential VMs Into Debug Mode and Exposes Memory

A newly disclosed hardware attack dubbed DDRop can undermine Intel Trust Domain Extensions (TDX) by manipulating DDR5 memory traffic, allowing an attacker with physical server access to force confidential virtual machines into debug mode and extract private memory in plaintext.

Researchers from KU Leuven, ETH Zurich, Google, Durham University, and other institutions released proof-of-concept code, hardware designs, firmware, and attack tooling for DDRop in a public GitHub repository.

The project targets Intel TDX, Intel Scalable SGX, and AMD SEV-SNP three major trusted execution environment technologies designed to protect workloads from an untrusted hypervisor or cloud operator.
Post #3165 85
🔴 Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds

With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig show that skilled human operators can move just as swiftly after gaining initial access.

In one instance highlighted by the cloud security company, the threat actor pivoted from a vulnerable Marimo notebook to an SSH bastion host in eight seconds using a custom Python toolkit they "wrote and debugged by hand" without any AI agent in the loop.

"Eight seconds is the kind of speed we expect to see in AI-assisted attacks," the Sysdig Threat Research Team said. "This operator got there on skill alone, and along the way walked straight past a trap that every agentic threat actor (ATA) we've profiled against this same CVE fell into. Not only can skilled human attackers move at machine speed, but they can also often better evade defenders' detections."
Post #3164 90
🔴 Red Heron Hackers Exploit Critical Gitea RCE to Steal Source Code and Deploy Linux Rootkit

A Chinese-speaking threat actor known as Red Heron has exploited a critical remote code execution (RCE) vulnerability in Gitea to steal private source code, harvest credentials, establish persistent access, and move laterally within victim infrastructures.

Researchers from the Acronis Threat Research Unit (TRU) have linked this operation to a newly documented Linux implant called JITTERLY, which contains an embedded LD_PRELOAD rootkit named SIXZUT.
Post #3163 94
🔴 WordPress Events Calendar Vulnerabilities Let Hackers Take Over 600,000 Websites

Two critical unauthenticated vulnerability chains in the widely used The Events Calendar WordPress plugin could allow attackers to execute code and fully compromise affected websites remotely. These flaws, identified by Wordfence Argus, impact plugin versions up to 6.17.4 and have been patched in version 6.17.4.1.

The Events Calendar is active on over 600,000 WordPress websites, making these vulnerabilities a significant risk for organizations that use the plugin for publishing event schedules, registrations, and community content.
Post #3162 88
🔴 Hackers Actively Exploit Critical WooCommerce Plugin Vulnerability to Upload PHP Backdoors

Threat actors are actively exploiting a critical vulnerability in the WooCommerce Wholesale Lead Capture plugin that lets unauthenticated attackers upload malicious PHP files and potentially seize full control of vulnerable WordPress sites.

The vulnerability , tracked as CVE-2026-27540, affects plugin versions 2.0.3.1 and earlier and has received a CVSS severity score of 9.8 out of 10.
Post #3161 99
🔴 Apple Patches 200 Vulnerabilities With New iOS 27, macOS Golden Gate 27 Releases

Apple announced patches for a record number of vulnerabilities across its desktop and mobile operating systems, including more than 200 flaws patched with the latest major releases: iOS 27 and macOS Golden Gate 27.

iOS 27 and iPadOS 27 include fixes for about 126 security flaws, 20 of which affect the kernel.

macOS Golden Gate 27 addresses 210 vulnerabilities, roughly 100 of which are shared with the iOS 27 release.

macOS Tahoe 26.7 patches 153 unique CVEs, including 26 security defects in the kernel that could lead to memory corruption, privilege escalation, system termination, and information leaks.
Post #3160 109
🔴 Former AT&T store worker jailed after moonlighting as a SIM-swap gang's inside man

44-year-old Kenneth Carter from Portland, Oregon, used to work in an AT&T retail store. But now he has been sentenced to 16 months in a federal prison.

That should be plenty of time for him to rue the day he agreed to increase his monthly income by helping a SIM swap gang in their attempt to steal over half a million dollars.

According to Carter's own plea agreement, the scam ran from May 2018 to November 2019 and involved at least three co-conspirators alongside Carter.
Post #3159 100
🔴 Suspected Black Axe gang leaders face cybercrime charges in the US

Five alleged leaders of the Black Axe cybercrime syndicate, known for its involvement in global-scale cyber-enabled financial fraud, have been extradited to the United States to face wire fraud and money laundering charges.

Prosecutors accuse Perry Osagiede, Franklyn Osagiede, Osariemen Clement, Collins Otughwor, and Musa Mudashiru of coordinating an internet fraud campaign from Cape Town from 2011 to 2021 that involved advance fee schemes and romance scams.

The five accomplices allegedly used multiple aliases, social media and online dating websites, and voice over internet protocol (VoIP) phone numbers to talk to victims in the United States and trick them into sending money after making them believe they were in a romantic relationship.
Post #3158 98
🔴 California: No more kids glued to their phones! No more endless feeds and chatbot companions

It is precisely from California, the heart of the global race for artificial intelligence and home to giants such as OpenAI, Anthropic, NVIDIA, Meta and Google, that a crackdown on AI-powered chatbots and endless social media feeds comes, with the aim of protecting the health and well-being of the little ones.

California has decided to cut children off from several digital mechanisms that force them to sit on their phones for hours or to be tethered to AI chatbots . Governor Gavin Newsom signed a package of 13 laws to protect minors in the digital environment . The restrictions include endless recommendation feeds, autoplaying content, and even children's toys with AI chatbots.
Post #3157 116
🔴 Search results are sending people to fake Bitrefill checkouts

Bitrefill is a legitimate company that sells gift cards for popular stores like Amazon, Deliveroo, Apple, Nintendo, and thousands of others. They also sell eSIMs, and mobile top-ups. You can pay on their website for all of these with cryptocurrency.

The scam is designed to catch people searching for Bitrefill or something it sells, like a gift card. Victims see a search result that appears to lead to Bitrefill but actually points to a lookalike domain. The fake site then takes them through what appears to be a normal purchase. The fake sites are not operated by or affiliated with Bitrefill; scammers have copied its branding and checkout process.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →