TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3157 · Back to latest

Older Posts 20 shown
Post #3156 117
🔴 LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server

A critical vulnerability in LiteSpeed Web Server Enterprise could let a low-privilege website user gain root access on a shared-hosting server, cPanel warned in an advisory published on September 14.

On such servers, many customers' sites run on a single machine, and an attacker with one of those hosting accounts could exploit the flaw to access or alter other sites and the server itself, according to the advisory.

cPanel said it had received notice of the flaw, which affects versions before 6.3.7, and urged administrators to update to that release, which LiteSpeed published on September 11.
Post #3155 127
🔴 Non-Zero-Day VPN Flaw Left Japan‘s Government Shared Network Platform Exposed: 246,000 Records at Risk

Japan‘s Digital Agency disclosed a VPN breach exposing 246,000 government employee records across 23 ministries. Detected June 25, publicly disclosed September 11.

Japan‘s Digital Agency disclosed that attackers exploited a vulnerability in a VPN device to access its Government Solution Service (GSS), potentially leaking personal information belonging to approximately 246,000 government employees, public officials, and contractors. The breach was detected on June 25 and confirmed as a VPN exploitation on July 9, meaning the public disclosure came 78 days after the initial detection and 63 days after the intrusion method was identified.
Post #3154 134
🔴 Root RCE Zero-Day in Cisco Secure Email Gateway Under Active Exploitation

Cisco warned customers on Monday that a zero-day vulnerability affecting Secure Email Gateway appliances has been exploited in the wild.

The vulnerability is identified as CVE-2026-76461 and has a CVSS score of 9.8. Cisco describes it as an email parsing issue in AsyncOS software that can be exploited remotely and without authentication to execute arbitrary commands on the underlying operating system with root privileges.

The tech giant explained that the critical flaw can be exploited to execute malicious SQL statements by sending them to the targeted user inside a specially crafted email.
Post #3153 147
Remote-Access Trojan Masquerades as Trusted System Utility Through Memory Injection

A newly analyzed AsyncRAT campaign uses a five-stage infection chain combining a malicious batch file, concealed PowerShell, a signed AutoIt interpreter and process injection to run the remote-access trojan from memory.

🔗 Read More
Post #3152 134
🔴 Hackers target exposed Vite dev servers to steal AWS, Azure secrets

A mass-scanning campaign targeting internet-exposed Vite development servers is attempting to steal cloud credentials and configurations from AWS and Azure deployments.

The operation leverages an exploit for CVE-2026-39364, a high-severity vulnerability that allows bypassing file read/access controls in Vite versions 7.1.0 through 7.3.2, as well as the 8.x branch before 8.0.5.

The flaw was disclosed on April 7 and allows an unauthenticated attacker to manipulate query parameters in an HTTP GET request to bypass security restrictions and retrieve files in plaintext from locations that should normally be out of their reach.
Post #3151 107
🔴 ClickFix attacks are tricking Mac and Windows users into hacking themselves

If you clicked on an HBO Max ad on Reddit over the past week, you might want to check your computer for malware.

These so-called “ClickFix” attacks have quickly become one of the rising cybersecurity threats of 2026, and they’re getting both sneakier and compromising people’s devices with greater frequency. Until recently, ClickFix attacks were a rarity, capitalizing on people searching the web for quick tech fixes. They have since evolved into a massive international effort to hack into people’s computers.
Post #3150 98
🔴 Amazon Prime Video takes on TikTok with short-form news clips

Amazon Prime Video is coming after TikTok with the addition of short-form news clips. The company said on Monday that it’s expanding its news coverage to include on-demand news clips offering both local and national stories. These will be available on TVs and other living room devices, but will soon roll out to the web and Prime Video’s mobile apps, the company said.

The clips will be available in the News destination within the Prime Video app in its Trending Topics and the Local News carousels. They join Prime Video’s existing local, national, and world news coverage from a number of major providers, which are available to everyone in the U.S. regardless of whether they have a Prime subscription.
Post #3149 83
🔴 126,000 SSNs LEAKED AFTER GREENBERG TRAURIG EXTORTION ATTACK

A new analysis of data leaked by Silent Ransom Group claims the Greenberg Traurig incident may be significantly larger than the law firm’s initial public description suggested.

Greenberg Traurig previously confirmed that an unauthorized actor accessed a limited number of documents and posted data on the dark web. The firm also disclosed that Social Security information was exposed.

Now, DataBreaches.net reports that analysis of the leaked material identified approximately 126,000 unique Social Security numbers.
Post #3148 80
Unauthenticated Threat Lets Intruders Steal Secrets From Vulnerable Code Platforms

A critical vulnerability in GitLab’s repository commits API is already being targeted in the wild, with attackers probing exposed self-hosted instances less than 24 hours after disclosure.

🔗 Read More
Post #3147 97
🔴 Google’s new search redirects make links harder to check before you click

Google is changing how some links in its search results work.

Instead of linking directly to the destination, Google has started routing some search result links through opaque google.com/goto?url=... redirects. The url parameter does not show a readable version of the destination but uses a custom, Google-specific encoding.
Post #3146 104
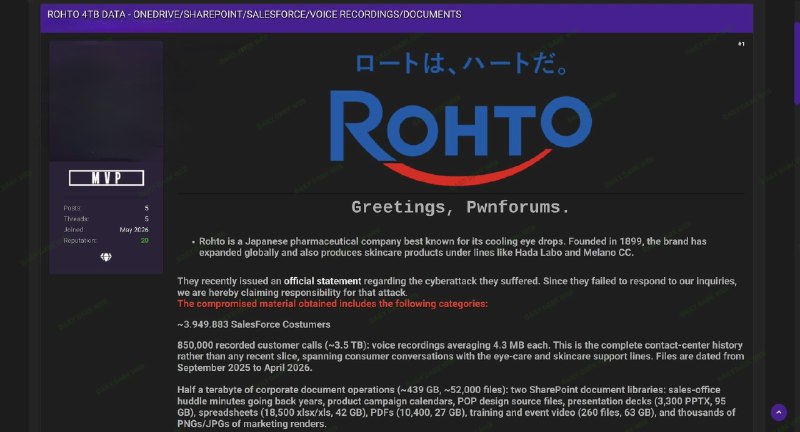
🔴 4TB OF ROHTO PHARMACEUTICAL DATA OFFERED FOR SALE

A threat actor is advertising approximately 4TB of data belonging to Japanese pharmaceutical giant Rohto Pharmaceutical.

The seller claims the archive includes:

* OneDrive data
* SharePoint data
* Salesforce information
* Voice recordings
* Internal documents

The timing is notable: Rohto publicly disclosed on September 11 that it identified possible unauthorized third-party access to its mail-order system on September 10 and is still investigating the scope.
Post #3145 106
🔴 Chinese Hackers Exploit Critical Tencent Software Flaw for One-Click Code Execution

A critical-severity vulnerability in Sogou Input Method has been exploited by a Chinese threat actor to deploy a backdoor, Gen Threat Labs reports.

Developed by Tencent, Sogou Input Method is one of the most popular Chinese-language input method editors (IMEs) for Windows and is used by hundreds of millions of users.

It is a collection of executables that communicate using a custom protocol scheme named sgbiz. When a URL is opened, the protocol handler (biz_helper.exe) parses the URL and dispatches it to the appropriate component.
Post #3144 88
🔴 Superhuman acquires YC-backed notetaker Fathom as productivity platforms push for agentic work

Superhuman is joining the cadre of productivity platforms launching notetakers — but rather than building one internally, it is acquiring Y Combinator-backed Fathom.

AI-powered productivity platforms aim to automate work. Typically, that automation is triggered when a user types prompts and creates workflows. It would be even better, however, if AI could proactively start work, and for that, the topics and action items discussed in meetings are key. Hence the desire by Superhuman and similar platforms to move into notetaking.
Post #3143 88
🔴 T-MOBILE DATABASE OFFERED ON UNDERGROUND FORUM

A new underground-forum listing is a database associated with T-Mobile US.

T-Mobile is one of the largest wireless carriers in the United States, making any credible new exposure potentially significant given the scale and sensitivity of telecom customer data.
Post #3142 106
🔴 Dutch NCSC Warns: Critical Check Point VPN Flaws Put Networks at Risk

Two critical Check Point VPN flaws score 9.8 and could enable remote code execution. Patch now and restrict VPN access before exploitation begins.

The Dutch NCSC warns that two critical vulnerabilities in Check Point VPN products, both rated CVSS score of 9.8, could soon be actively exploited. If you use Check Point VPN, you should patch it immediately.

CVE‑2026‑85102 resides in the VPN negotiation process and lets an unauthenticated attacker bypass security checks and run their own code on the gateway. CVE‑2026‑85103 is a heap overflow in the certificate ASN.1 decoder that also leads to remote code execution on Security Gateways and Security Management Servers.
Post #3141 90
🔴 Telus Warns Customers of Account Breaches

Telus, one of Canada’s largest telecom providers, is notifying some customers that their accounts have been breached and their personal information has been accessed.

In data breach notifications sent to customers whose consumer telecom accounts were affected, Telus said the intrusions occurred between February 2025 and June 2026.

According to the company, the attacker used compromised credentials to access Telus accounts and the information they store, including names, account numbers, phone numbers, billing addresses, email addresses, partial payment card numbers, subscription details, and payment history.
Post #3140 107
🔴 Revolut discloses data breach exposing financial info, passports

Fintech company Revolut has disclosed a data breach after sharing data from an undisclosed number of customers with a threat actor impersonating a government agency.

Revolut operates in over 160 countries and regions and offers banking, money management, and investment services to more than 80 million customers worldwide, including 800,000 business customers.

In emails sent to affected customers, the company said that the attacker requested the personally identifiable information (PII) via email using a government agency's domain.
Post #3139 113
🔴 ConnectWise Patches ScreenConnect Vulnerability Exploited in Worm-Like Attacks

ConnectWise has released urgent patches for a critical-severity vulnerability in the ScreenConnect remote access and support software that has been exploited in worm-like attacks.

Tracked as CVE-2026-84869 (CVSS score of 9.9/10), the security defect is described as a missing authorization and improper privilege management issue.

The bug creates “a condition in the ScreenConnect client that may allow files to be transferred and executed through an active remote session without authorization or Host confirmation in certain circumstances,” ConnectWise explains in its advisory.
Post #3138 128
🔴 Microsoft: September updates break audio on some Windows PCs

Microsoft has confirmed that USB audio devices may fail on some Windows systems after installing the KB5124008and KB5124012 September 2026 security updates.

This known issue affects only devices running Windows 11, version 24H2 or later, and is limited to USB Audio Class 1.0 devices.

"After installing the September 8, 2026, Windows security update [..], some USB Audio Class 1.0 devices might fail to start or produce audio," Microsoft said in a Friday update to the release health dashboard.
Post #3137 128
🔴 That CAPTCHA could steal your PC! 5,400 sites are already infected

Cybersecurity experts at Netskope have detected a large-scale malicious campaign in which attackers use over 5,400 compromised websites to deliver the ClickFix payload. The malicious code is stored in BNB Smart Chain (BSC) smart contracts, making it significantly more difficult to disrupt the hackers' infrastructure.

According to information obtained by researchers, most of the compromised sites run on WordPress and PrestaShop and belong to small businesses. However, it is not yet known how the attackers initially gained access to these resources.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →