TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3137 · Back to latest

Older Posts 20 shown
Post #3136 129
🔴 Proteins Never Existed in Nature: Artificial Intelligence Opens a New Frontier

Artificial intelligence has learned to design proteins that don't necessarily have to resemble those created by nature. Researchers have developed the PottsMPNN system , which searches for appropriate amino acid sequences for a given structure while not attempting to reproduce known natural proteins with the utmost precision. This approach opens up a much broader scope for the creation of molecules with novel properties.

Modern protein design works largely in the opposite direction to the famous AlphaFold. AlphaFold receives a sequence of amino acids and attempts to determine the three-dimensional structure the protein will assume. When creating a new protein, researchers can first imagine the required structure and then select an amino acid sequence capable of stably folding into it.
Post #3135 125
🔴 Programmers came first. Now OpenAI is moving to financial investors!

After programmers, OpenAI is now targeting one of the most expensive office jobs ever: financial investor.

The company has launched a special version of ChatGPT for the financial sector , capable of performing a significant part of the work of junior investment bankers, who on Wall Street can earn up to $200,000 a year, including bonuses.

ChatGPT for Financial Services is primarily geared toward investment banks and analytics departments. OpenAI developed the service in collaboration with Morgan Stanley and Evercore, investigating which tasks bankers spend the most time on routine, manual work. A similar transition has already occurred in development, where the company has transformed Codex into a system capable of executing lengthy tasks in parallel.
Post #3134 129
🔴 HackerHood Discovers New Bug in FortiClient VPN: Beware of Saved Passwords

Convenience features designed to simplify the user's life often hide non-trivial security pitfalls.

This is the case with the "Save Password" option present in many VPN clients , which allows you to avoid re-entering your credentials each time you connect, but which raises legitimate questions: how are stored credentials protected? Where are they stored locally? And above all, how robust is the mechanism used to prevent their recovery by an attacker?
Post #3133 164
🔴 AI scares even its creators! Amodei calls for a slowdown, while Altman and Musk support him

Dario Amadei, head of Anthropic, after the idea of ​​a sort of moderation in research and the development of artificial intelligence, doubles down by reporting the following:

“I won't lie to you: There are real dangers. For too long, the industry has lied to people about the risks of this technology. We at Anthropic have never done that, but much of the industry has,” Amodei told CBS's “Sunday Morning.” He added, “I don't think banning it completely is the right approach. First, I don't think it's acceptable to permanently give up the incredible benefits and medical treatments. Second, this technology will be developed in other countries, including authoritarian ones.” He was referring to the Open Weight models released by Chinese players and jeopardizing the business of large American players based on reselling APIs.
Post #3132 179
Cybercriminal Jailed in U.S. Over Ransomware Scheme

Ukrainian national Oleksii Oleksiyovych Lytvynenko, 44, has been sentenced to four years in a U.S. federal prison for his role in a ransomware operation that targeted more than 1,000 organizations worldwide.

🔗 Read More
Post #3131 180
🔴 Former Google DeepMind team creates Faraday AI, surpassing Anthropic and OpenAI in scientific tasks

British startup Inherent , founded by former Google DeepMind employees, has unveiled its AI agent Faraday, capable of autonomously verifying the credibility of scientific publications. The developers claimed that the system significantly outperformed larger models like Anthropic and OpenAI, despite using only 27 billion parameters.

Inherent emerged from stealth mode just a few weeks ago, simultaneously raising $50 million in an early round of funding , and has now revealed the first details of its development.
Post #3130 189
Fintech Firm Handed Sensitive Customer Records to an Impostor

Revolut has confirmed that sensitive customer information was disclosed to an unauthorized party after a fraudulent request appeared to originate from a legitimate government agency.

🔗 Read More
Post #3129 218
🔴 Be careful! Your infected PC now has a price! AI values ​​it and criminals put it up for sale

Researchers at Group-IB have discovered a Python framework called BraZetsu , which turns infected Windows systems into merchandise for other criminals. The malware collects data about the victim, assesses the value of the compromised machine using generative artificial intelligence , and then access to it can be purchased on the criminal marketplace Infected Marketplace.

According to experts, BraZetsu is behind the Infected Marketplace (also known as Banco de Infects) criminal platform, where attackers can purchase initial access to infected hosts and remotely launch their tools and malware. Access to the platform requires a deposit of $5.80.
Post #3128 233
🔴 Bullets instead of rockets: the US has found a way to shoot down drones at negligible cost

A cheap drone can force an air defense system to spend money on an interceptor that's worth far more than its target. Auriga Space proposes to change the economics of air defense: the American startup uses a mobile installation capable of accelerating projectiles beyond the speed of sound without rocket engines or fuel reserves.

The first field test took place in the Mohave Desert in California at a temperature of approximately 38°C. The developers placed the electromagnetic accelerator inside a transport container approximately three meters long and conducted more than 12 launches at speeds exceeding Mach 1. Auriga Space separately tested the possibility of conducting burst launches away from stationary power infrastructure.
Post #3127 205
AI-Powered Intrusion Campaigns Expand With Automated Attack Workflows

Cyber operations are becoming increasingly automated as criminal and state-linked groups deploy AI-powered workflows to handle reconnaissance, credential attacks, malware development and large-scale information theft.

🔗 Read More
Post #3126 210
🔴 OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers

The "major malicious attack" that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published by researchers Spencer Kitts, Thomas Larsen, and Sydney Von Arx.

On May 12, Maciej Mensfeld, senior product manager for software supply chain security at Mend.io, disclosed details of a coordinated cyber attack that targeted the package manager for the Ruby programming language with hundreds of junk gems, prompting the maintainers to suspend new user sign-ups for about four days.

In a follow-up analysis, Socket highlighted a campaign dubbed GemStuffer that involved a cluster of more than 150 gems that used the package registry as a data exfiltration channel and staged public data scraped from U.K. local government democratic services portals. At that time, the software supply chain security company noted the activity shares the "same abuse pattern" as the broader RubyGems spam-publishing incident.
Post #3125 204
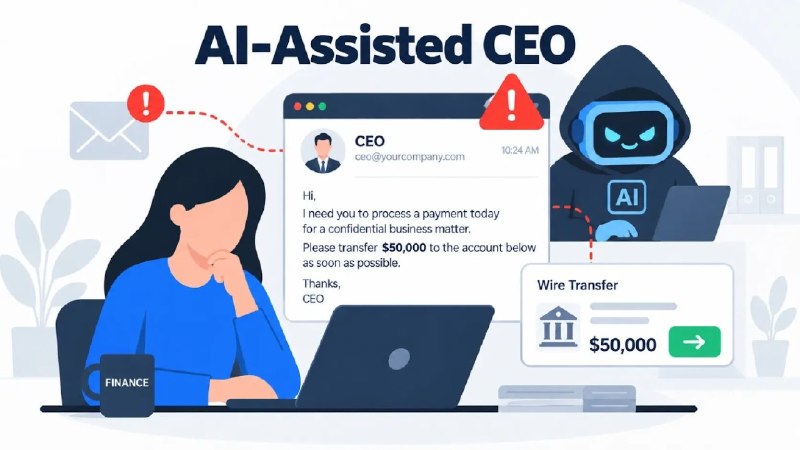
🔴 Hackers Use AI-Assisted CEO Emails to Trick Finance Teams Into Sending $50,000 Payments

Threat actors are using AI-assisted phishing templates, executive impersonation, fake ServiceNow invoices, and fabricated email threads to pressure finance teams into authorizing fraudulent ACH payments worth nearly $50,000.

Microsoft detected more than one million messages in the campaign, demonstrating how business email compromise (BEC) operations are becoming more polished, scalable, and difficult to spot.

The United States received 87.7% of the campaign volume, indicating a broad effort to target organizations with U.S.-based finance and accounts-payable operations.
Post #3124 149
🔴 New IoT Malware Uses Public Linux Exploits to Gain Root and Launch DDoS Attacks

A newly observed IoT malware family dubbed KATARU targets internet-exposed devices through Telnet credential brute-forcing, then attempts to gain root privileges with publicly available Linux kernel exploits before enrolling compromised systems in a DDoS botnet.

The sample combines familiar Mirai-style flooding functions with encrypted command-and-control, broad persistence logic, anti-analysis checks and decoy network activity designed to complicate incident response.

Following successful access, the operator used BusyBox commands to download and execute an ARM payload named vlxx.arm, with SHA-256 hash 13382c16e2401b07451577b46e634b8031ec254d98b876e59692b5fa22abc1d4.
Post #3123 139
District Scrambles to Restore Classes After Major IT Incident

Springfield Public Schools is preparing to bring students back after a cyber incident forced the district to close for the latter part of the week. But as classrooms prepare to reopen, educators say major questions about the incident remain unanswered.

🔗 Read More
Post #3122 132
🔴 Kiteworks Acquires Bonfy.AI to Fill the AI Gap in Data Governance

Kiteworks has announced the acquisition of AI data security company Bonfy.AI, a move aimed at extending real-time policy enforcement over sensitive data exchanged by both human users and AI agents.

Kiteworks delivers a content-sharing platform to safeguard sensitive data as it moves across enterprise networks, external organizations, and internal systems. It includes regulatory compliance, governance, and audit tracking.

Bonfy.ai is an AI‑native content‑security platform protecting sensitive data across human workflows and AI‑agent reasoning. It offers real‑time classification, contextual enforcement, and cross‑SaaS governance.
Post #3121 108
🔴 Okta Patches Auth0 and Access Gateway Vulnerabilities Let Attackers Enable XSS, Authentication Bypass and SQL Injection

Okta has released security updates for three high-severity vulnerabilities affecting the Auth0 AD/LDAP Connector and Okta Access Gateway.

These vulnerabilities could allow authenticated attackers to trigger stored cross-site scripting (XSS), bypass Protected Rule authorization controls, or execute unintended SQL commands against configured backend databases under specific deployment conditions.

All three vulnerabilities were disclosed on September 8, 2026. Organizations using the affected Auth0 connector or Okta Access Gateway should prioritize upgrading, especially if they use directory attributes, Protected Rules, or custom SQL-backed advanced datastores.
Post #3120 96
🔴 Critical GitLab Flaws Let Attackers Read Arbitrary Files, Steal Credentials and Execute Code

GitLab has issued an emergency security update to address two critical vulnerabilities that could lead to unauthenticated file disclosure and authenticated credential theft, as well as a high-severity flaw that may enable remote code execution.

The company released updated versions of GitLab Community Edition and Enterprise Edition, specifically versions 19.3.2, 19.2.6, and 19.1.8, on September 10, 2026.
Post #3119 108
🔴 GPT-6 Astra finished the game Portal in 24 hours, spending $571.33

The GPT-6 Astra artificial intelligence model, announced this week by OpenAI, has successfully completed the space puzzle game Portal without human intervention. According to VideoCardz, the experiment was conducted by user cozyblaze, who connected the model to the game and assigned it to complete puzzles in test chambers.

As is well known, Portal is based on spatial puzzles that require the player to understand the features of rooms, the layout of portals, and movement between different surfaces. The AI ​​agent received visual information from the game, using a set of connected tools to make decisions. The new setup also provided the player's coordinates. As cozyblaze reported, the system was updated before launch to use the new Astra context management system.
  • ❤ 1
Post #3118 105
Federal Privacy Oversight Shifts From Agency Guidance to Codified Health-Data Requirements

The Federal Trade Commission has withdrawn a controversial 2021 policy statement covering data breaches involving health apps and connected devices, saying the guidance has become unnecessary following a subsequent overhaul of the agency’s formal rules.

🔗 Read More
Post #3117 129
🔴 Microsoft fixes Teams, Outlook launch failures on ARM Windows PCs

Microsoft has fixed a bug that prevented Teams and Outlook from launching after installing updates released since the August 2026 Patch Tuesday.

The company confirmed last week that this known issue affects users who haven't installed Microsoft Store updates on ARM-based Windows devices (such as the Surface Pro 11 and Surface Laptop 7) running Windows 11 24H2 or later.

"After installing Windows security updates released on or after August 11, 2026, (KB5121003), Microsoft Teams and the new Outlook for Windows might fail to launch or might close unexpectedly on ARM-based devices, such as Surface Pro 11 and Surface Laptop 7," Microsoft explained in a Windows release health update.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →