TGViewer
PPHM HACKER NEWS PPHM HACKER NEWS @pphm_hackernews · 10.7K subscribers
Post #3181 108
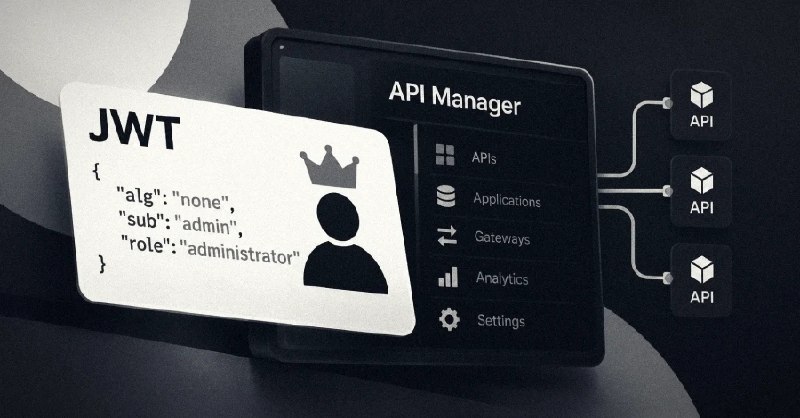
🔴 Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr.

The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and reporting the flaw.

"JWT authentication can be bypassed when a token is signed using an unsupported algorithm, allowing unauthorized access," according to an advisory released by WSO2 in May 2026. "Successful exploitation of the vulnerability may lead to unauthorized access, including potential compromise of administrative accounts and full account takeover."
More from @pphm_hackernews
  1. Oct 17, 2026🚨 Yemeni attack targets the Saudi capital, Riyadh. #Riyadh #SaudiArabia #Yemen #BreakingN…
  2. Oct 17, 2026Stealthy Intrusions Exploit Enterprise Access Weakness to Establish Persistent Control A s…
  3. Oct 17, 2026🚨 Direct strikes targeted Iranian opposition sites in Erbil. #Erbil #Iraq #Kurdistan #Bre…
  4. Oct 17, 2026Calif Achieves Persistent Root Access on Apple's Latest Smartphone Security research firm…
  5. Oct 17, 2026🚨 6,000 Egyptian soldiers have been deployed to support Saudi Arabia in the war against Y…
  6. Oct 17, 2026🚨 #BreakingNews‌ | Russia fired six ballistic missiles at the Zaporizhzhia plant in its f…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →