TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.32K
Photos
434
Videos
3
Links
575

Showing posts older than #435 · Back to latest

Older Posts 20 shown
Post #434 621
16B Credential Leak: The Largest Data Breach Ever? 😱

Over 16 billion credentials - usernames, passwords, and session tokens - have been exposed in a single aggregation of malware logs and past breaches, impacting accounts from Google, Facebook, Apple, GitHub, Telegram, and more.

Learn how this accidental mega-dump was uncovered, who’s behind it, and how to check if your data is at risk in the our new article.

👉 Read now: https://netlas.io/blog/16_billion_credential_breach/
  • ❤ 4
  • 👾 3
Post #431 576
CVE-2025-42963: Deserialization of Untrusted Data in SAP NetWeaver Application server for Java, 9.1 rating 🔥

A vulnerability in the LogViewer component allows an authenticated attacker to exploit unsafe Java object deserialization, which could lead to complete control over the system.

Search at Netlas.io:
👉 Link: https://nt.ls/0c6Ud
👉 Dork: http.headers.server:"NetWeaver"

Vendor's advisory: https://support.sap.com/en/my-support/knowledge-base/security-notes-news/july-2025.html
  • 👾 3
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #427
Netlas.io pinned «Dear Netlas Community Members, We are seeking passionate authors to contribute to our cybersecurity blog. If you’re interested in sharing your expertise and insights, we welcome you to join us 🤝 ✍️ What’s in it for you? • Competitive compensation in USDT…»
Post #426 702
Dear Netlas Community Members,
We are seeking passionate authors to contribute to our cybersecurity blog. If you’re interested in sharing your expertise and insights, we welcome you to join us 🤝

✍️ What’s in it for you?
• Competitive compensation in USDT — from $200 up to $1000 per article.
• A dedicated author profile to boost your visibility.
• Editorial support from our professional team.

👉 Ready to share your knowledge?
Fill out the form and join the Netlas author team today: https://netlas.io/promo/write_for_netlas/
netlas.io Join as an author - Netlas Write for the Netlas Blog: share your expertise in cybersecurity, internet research and OSINT with our audience, and learn how to apply as an author.
  • 🔥 7
Post #424 690
CVE-2025-6543, -5777: Vulnerabilities in NetScaler ADC/Gateway, 9.2 - 9.3 rating 🔥

Fresh vulnerabilities related to file manipulation outside the memory buffer. The first of them allows an attacker to perform DoS, the second - to obtain private data.

Search at Netlas.io:
👉 Link: https://nt.ls/XriYU
👉 Dork: http.title:"Netscaler Gateway" OR http.title:"Citrix Gateway" OR http.headers.x_powered_by:"Citrix ADC (formerly NetScaler)"

Vendor's advisory: https://support.citrix.com/support-home/kbsearch/article?articleNumber=CTX694788
  • 🔥 3
  • 👾 3
  • 👍 1
Post #422 1.2K
CVE-2025-4981: RCE in Mattermost, 9.9 rating 🔥

A recently patched vulnerability in some versions of Mattermost allowed attackers to write files to arbitrary locations on the host system, which could lead to remote code execution.

Search at Netlas.io:
👉 Link: https://nt.ls/zchKc
👉 Dork: http.meta:"mattermost"

Vendor's advisory: https://mattermost.com/security-updates/
  • 🔥 4
  • 👾 3
Post #421 689
AI‑Powered Attack Surface Mapping 🤖

Artificial intelligence is a topic that has not lost its popularity in recent years. Language models have proven themselves in many areas, including information security.

In our latest article, discover how to leverage AI for comprehensive attack surface discovery, plus get an unbiased comparison of leading models so you can pick the right one for your needs.

👉 Read now: https://netlas.io/blog/ai-driven_attack_surface_discovery/
netlas.io AI-Driven Attack Surface Discovery - Netlas Blog Can large language models assist in attack surface mapping? We put them to the test using the Netlas Discovery API in a hands-on classification experiment.
  • 🔥 5
  • 👍 2
  • 👾 1
Post #420 916
CVE-2025-4278, -5121, 2254 and other: Multiple vulnerabilities in GitLab, 3.7 - 8.7 rating❗️

In recent patch notes, GitLab reported ten vulnerabilities, including HTML injection, XSS, DoS, and more.

Search at Netlas.io:
👉 Link: https://nt.ls/dq6qU
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/06/11/patch-release-gitlab-18-0-2-released/#cve-2025-5121---missing-authorization-issue-impacts-gitlab-ultimate-ee
  • 👾 3
  • 🔥 2
Post #419 591
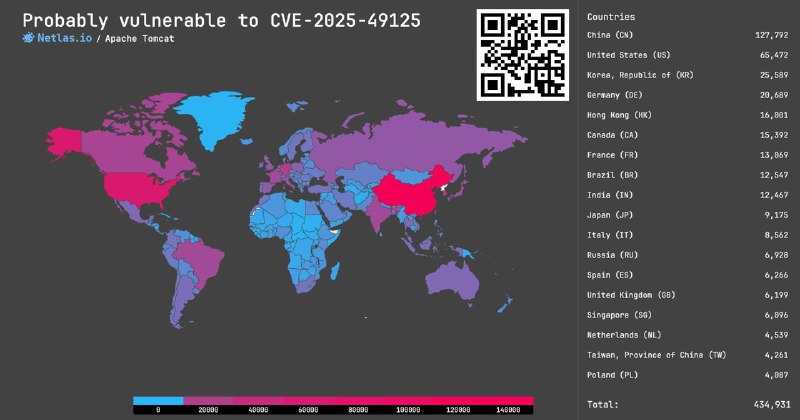
CVE-2025-48976, -48988, -49125: Multiple vulnerabilitites in Apache Tomcat, 7.5 rating❗️

Recent vulnerabilities in Apache Tomcat allow an attacker to perform DoS and gain access to resources through insecure path.

Search at Netlas.io:
👉 Link: https://nt.ls/oAb4X
👉 Dork: http.favicon.hash_sha256:64a3170a912786e9eece7e347b58f36471cb9d0bc790697b216c61050e6b1f08 OR http.headers.server:"Apache-Coyote"

Vendor's advisory: https://lists.apache.org/thread/m66cytbfrty9k7dc4cg6tl1czhsnbywk
  • 🔥 3
  • 👾 3
  • 👍 2
Post #418 712
CVE-2025-4798, -4799: Absolute Path Traversal in DownloadManager WordPress Plugin, 4.9 - 7.2 rating❗️

Vulnerabilities shared with us by the pen tester who found them. Allow attackers to manipulate files on the server, which can lead to RCE.

Search at Netlas.io:
👉 Link: https://nt.ls/DH8EA
👉 Dork: http.body:"plugins/wp-downloadmanager"

More information here: https://youtu.be/QTe3rf0-e7U?si=THZKoKeI1vN-arR7
  • 👾 5
  • 🔥 3
Post #416 669
CVE-2025-42989: Missing Authorization in SAP NetWeaver, 9.6 rating 🔥

One of the vulnerabilities disclosed in a recent patch allows an authenticated user to escalate their privileges, which could critically impact the integrity and availability of the system.

Search at Netlas.io:
👉 Link: https://nt.ls/lB0fI
👉 Dork: http.body:"This error page was generated by SAP Web Dispatcher!"

Vendor's advisory: https://support.sap.com/en/my-support/knowledge-base/security-notes-news/june-2025.html
  • 🔥 3
  • 👾 2
Post #415 621
CVE-2025-32756: Buffer Overflow in Fortinet products, 9.8 rating 🔥

Some Fortinet products, including FortiMail, FortiRecorder, and FortiVoice, are vulnerable to a buffer overflow that could allow a remote, unauthenticated attacker to execute arbitrary code or commands.
The vulnerability is not new, but a PoC was recently released!

Search at Netlas.io:
👉 Link: https://nt.ls/nmu5K
👉 Dork: certificate.subject.common_name:"FortiMail" OR certificate.subject.common_name:"FortiRecorder" OR certificate.subject.common_name:"FortiVoice"

Vendor's advisory: https://fortiguard.fortinet.com/psirt/FG-IR-25-254
  • 🔥 5
  • ☃ 2
  • 👾 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →