
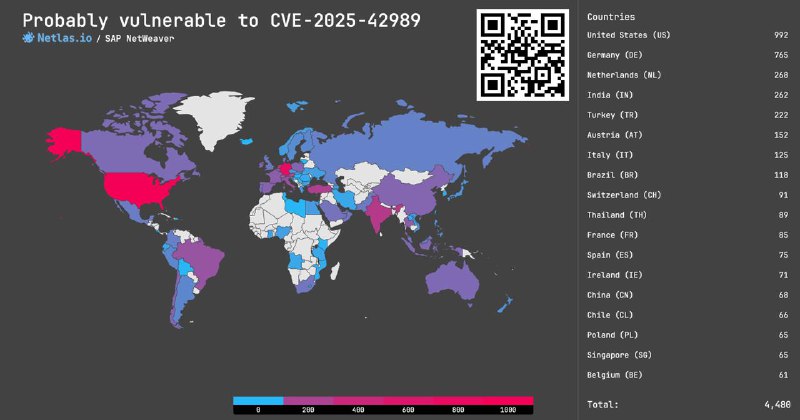
CVE-2025-42989: Missing Authorization in SAP NetWeaver, 9.6 rating 🔥
One of the vulnerabilities disclosed in a recent patch allows an authenticated user to escalate their privileges, which could critically impact the integrity and availability of the system.
Search at Netlas.io:
👉 Link: https://nt.ls/lB0fI
👉 Dork: http.body:"This error page was generated by SAP Web Dispatcher!"
Vendor's advisory: https://support.sap.com/en/my-support/knowledge-base/security-notes-news/june-2025.html
Post #416
669
- 🔥 3
- 👾 2