
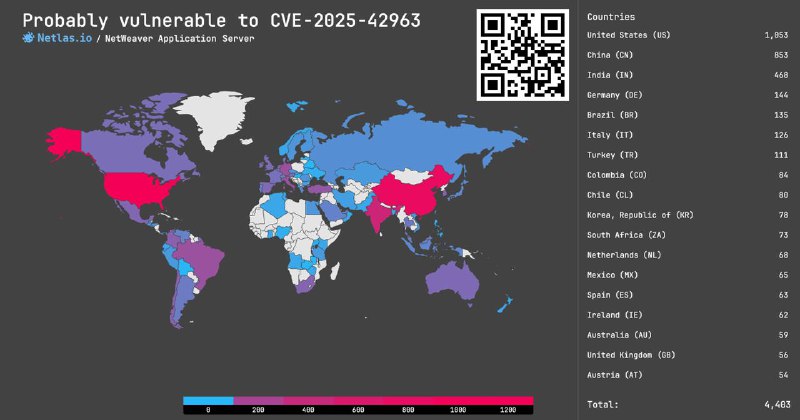
CVE-2025-42963: Deserialization of Untrusted Data in SAP NetWeaver Application server for Java, 9.1 rating 🔥
A vulnerability in the LogViewer component allows an authenticated attacker to exploit unsafe Java object deserialization, which could lead to complete control over the system.
Search at Netlas.io:
👉 Link: https://nt.ls/0c6Ud
👉 Dork: http.headers.server:"NetWeaver"
Vendor's advisory: https://support.sap.com/en/my-support/knowledge-base/security-notes-news/july-2025.html
Post #431
576
- 👾 3
- 👍 2
- ❤ 1
- 🔥 1