TGViewer
Channel Public Channel
Linux Kernel Security

Linux Kernel Security

@linkersec

Links related to Linux kernel security and exploitation | Chat @linkersec_chat | @xairy @a13xp0p0v | Mirrors on https://xairy.io/linkersec
Subscribers
4.72K
Photos
122
Videos
0
Links
355

Showing posts older than #274 · Back to latest

Older Posts 19 shown
Post #273 5.03K
SELinux bypasses

An amazing article by Klecko about different approaches to bypassing SELinux in Android kernel exploits.

The author lists multiple ways to disable SELinux via an arbitrary address read/write primitive and shows which of them are detected by the Samsung and Huawei hypervisors (spoiler: not all 😁).
  • 👍 7
Post #272 5.7K
Deep Dive into RCU Race Condition: Analysis of TCP-AO UAF (CVE-2024–27394)

V4bel published an analysis of a race condition vulnerability in the TCP-AO subsystem caused by incorrect usage of the kernel RCU mechanism.

The researcher managed to trigger it reliably using the ExpRace technique.
  • 👍 4
Post #269 8.95K
SLUB Internals for Exploit Developers

Slides and recording for a talk by Andrey Konovalov that covers the SLUB allocator internals and explains how common Slab shaping approaches work for exploiting Slab memory corruption bugs.
  • 🔥 36
  • 👍 2
Post #268 4.75K
GPUAF: Using a general GPU exploit tech to attack Pixel 8

A talk by Pan Zhenpeng and Jheng Bing Jhong about leveraging an integer overflow bug in the Mali GPU driver to gain use-after-free access to physical pages, fake GPU page tables, and escalate privileges on Pixel 8.
  • 🔥 10
  • 👍 2
Post #267 4.32K
CVE-2020-27786 (Race Condition + Use-After-Free)

An article by ii4gsp about exploiting a racy use-after-free in the MIDI subsystem.
  • 👍 10
  • 🔥 1
Post #266 4.13K
Ongoing slab hardening efforts

Recently, there have been multiple efforts to make the exploitation of slab memory corruptions harder.

1️⃣ RANDOM_KMALLOC_CACHES by Ruigi Gong; merged in v6.6; enabled in Ubuntu 24.04; LWN article

This feature creates 16 instances of each normal kmalloc cache and makes kmalloc randomly pick one of them based on the code location of the kmalloc call.

2️⃣ SLAB_BUCKETS by Kees Cook; merged in v6.11; LWN article

It allows putting specific dynamically-sized allocations into separate caches called buckets. This requires annotating allocation sites. This feature is intended to be used for user-controllable allocations. So far, only msg_msg and v/memdup_user allocations are annotated.

3️⃣ SLAB_PER_SITE by Kees Cook; under discussion; LWN article

This patchset creates a set of buckets for each kmalloc call site without manual annotations.

4️⃣ SLAB_VIRTUAL by Jann Horn and Matteo Rizzo; under discussion; documentation

It mitigates cross-cache attacks by making the slab allocator use a unique virtual memory address range for each cache for allocating slabs.
  • 👍 16
  • 🔥 1
  • 🎉 1
Post #265 3.95K
SSD Advisory — Linux kernel TAPRIO OOB

An article about exploiting an RCU-involved race condition in the TAPRIO network queuing discipline implementation. The exploit is by Kyle Zeng.
  • 👍 7
  • 🔥 2
Post #264 4.4K
CVE-2022-22265: Samsung NPU driver

An article by Javier P Rufo about exploiting a slab double-free in the Samsung's NPU driver via the Dirty Pagetable technique.
  • 🔥 14
Post #263 4.02K
PageJack: A Powerful Exploit Technique With Page-Level UAF

A talk, a summary article, and a related paper by Zhiyun Qian et al. about overwriting slab objects containing a struct page * field to achieve arbitrary read/write in physical memory.

The authors also shared a set of exploits that uses the described technique.
  • 🔥 16
  • 👍 2
Post #262 4.53K
Listen Up: Sonos Over-The-Air Remote Kernel Exploitation and Covert Wiretap

A talk and an article by Robert Herrera and Alex Plaskett about remotely exploiting a bug in the Wi-Fi driver of the Sonos One smart speaker.
  • 👍 11
Post #261 5.34K
A deep dive into CVE-2023-2163: How we found and fixed an eBPF Linux Kernel Vulnerability

An article by JJ and Meador Inge about exploiting a bug in the eBPF subsystem found with buzzer.
  • 🔥 14
  • 👍 3
Post #260 5.12K
SLUBStick: Arbitrary Memory Writes through Practical Software Cross-Cache Attacks within the Linux Kernel

A paper by Lukas Maar, Stefan Gast, et al. about exploiting slab memory corruptions via a cross-allocator slab-to-page attack targeting user page tables.

The paper covers:

— Using a timing side-channel to make sure that all objects in a slab are under the exploit's control to increase the success chance of executing a cross-cache or a cross-allocator attack;

— Converting limited slab memory corruptions to a stronger slab use-after-free write primitive;

— Using a single-shot slab use-after-free write to gain control over user page tables and thus obtain physical memory arbitrary read/write.
  • 🔥 25
Post #258 4.65K
So You Wanna Find Bugs In The Linux Kernel?

Slides of the talk presented by sam4k at TyphoonCon. The talk gives an overview of the Linux kernel vulnerability research area and suggests approaches and tools for finding bugs.
  • 🔥 10
  • 👍 5
Post #257 7.24K
Post #255 5.27K
Driving forward in Android drivers

An article by Seth Jenkins about exploiting a race condition in the MediaTek mtk_jpeg driver that leads to a variety of memory corruption side-effects.

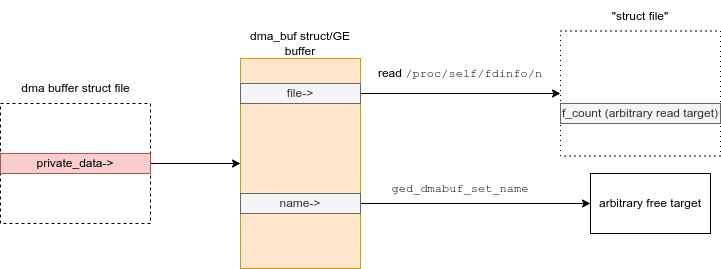
The described data-only exploit leverages the bug to get a use-after-free on a dmabuf file structure and then gets an arbitrary read/write primitive to disable SELinux and gain root on Asus ROG 6D.

In the exploit, Seth deliberately avoided using the cross-cache techniques, as these might soon get mitigated by SLAB_VIRTUAL.

The article also covers:

— Approaches to discovering device drivers accessible to unprivileged users on Android;
— Using the MediaTek GED (GPU Extension Device) driver to gain extremely powerful slab memory control primitives.
  • 👍 14
  • 👎 1
  • 🔥 1
Post #254 4.77K
Attacking Android Binder: Analysis and Exploitation of CVE-2023-20938

An article by Zi Fan Tan, Gulshan Singh, and Eugene Rodionov about exploiting a vulnerability in the Android Binder device driver that leads to a slab use-after-free.

Zi and Eugene also gave a talk (slides) about this work at OffensiveCon last month. There, they also shared the details about finding this vulnerability with a custom Linux Kernel Library–based fuzzer.
  • 🔥 13
  • 👎 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →