TGViewer
Channel Public Channel
Linux Kernel Security

Linux Kernel Security

@linkersec

Links related to Linux kernel security and exploitation | Chat @linkersec_chat | @xairy @a13xp0p0v | Mirrors on https://xairy.io/linkersec
Subscribers
4.71K
Photos
122
Videos
0
Links
355
Recent Posts 20 shown
Post #397 810
CROSS-X: Generalized and Stable Cross-Cache Attack on the Linux Kernel

Paper by Dong-ok Kim, Juhyun Song, et al. documenting the steps for executing cross-cache attacks for caches with min_partial >= cpu_partial_slabs.

The paper also describes a fuzzing-based approach of finding target slab objects useful for exploitation.
  • 🔥 13
  • 🤯 3
  • 👍 2
Post #396 1.75K
Testing race conditions with memory access tracing and stack-based delay injection

Article by Jann Horn about MAccConc — a KCOV-based tool for exploring possible kernel code interleavings of a multi-threaded program.
  • 🔥 4
  • 👏 3
  • 👍 2
Post #395 2.46K
SCTPhantom: An 18-Year-Old SCTP ASCONF Transport Use-After-Free

Article about exploiting CVE-2026-64564 in the implementation of the Stream Control Transmission Protocol (SCTP). Authors exploited a UAF in the kmalloc-1k cache to gain root and escape a container.
  • 🔥 10
  • 👏 1
Post #394 4.79K
Gone in 60 Frames – USB Video Exploitation

Article (and slides) by Alex Plaskett and Robert Herrera about fuzzing USB drivers with syzkaller and writing an exploit that gains code execution over USB on Ubuntu.
  • 🔥 15
  • 👍 2
Post #393 3.53K
IonStack part III: Rooting Android 17 with GhostLock

Article about adapting the exploit of CVE-2026-43499 (racy stack use-after-free in the futex implementation) to Android.

The researchers used KernelSnitch, ashmem fops overwriting, pipe_buffer corruption, and other tricks to perform LPE.
  • 🔥 17
Post #392 3.86K
I handed the epoll UAF to an agent

Article by Guy Beck about using Claude for porting an exploit for an eventpoll vulnerability to Android.
  • 🔥 9
  • 👍 4
  • 🤔 1
Post #391 3.44K
IonStack part II: GhostLock, a stack-UAF that has existed in ALL Linux distributions for 15 years

Article about exploiting a racy stack use-after-free in the futex implementation. The bug was used to pwn a kernelCTF instance.
  • 🔥 17
  • 👍 2
Post #390 2.95K
Unprivileged root via an out-of-bounds write in the FUSE readdir cache (CVE-2026-31694)

Article by Stan Shaw about exploiting a page OOB write bug in the FUSE subsystem by overwriting /etc/passwd in the page cache.
  • 🔥 6
  • 🤔 3
  • 👍 1
Post #389 3.01K
Januscape: Guest-to-Host Escape in KVM/x86

Hyunwoo Kim published an article about a use-after-free vulnerability in the shadow MMU emulation of KVM/x86 (CVE-2026-53359). Both Intel (VMX) and AMD (SVM) code is affected.

The article only covers achieving a kernel crash via this bug, but the vulnerability can also be exploited to escape the guest VM. The author used this bug to pwn a kvmCTF instance.
  • 🔥 14
  • 👍 6
Post #388 9.16K
ITScape: Guest-to-Host Escape in KVM/arm64

Article by Hyunwoo Kim about exploiting a race condition bug in the KVM driver on the arm64 architecture to escape the guest VM.
  • 🔥 18
  • 🤔 2
Post #387 4.88K
Bad Epoll: The bug missed by Mythos

Article by Jaeyoung Chung about exploiting CVE-2026-46242 — a race condition bug in the eventpoll subsystem. Jaeyoung exploited this bug to claim a kernelCTF entry, but the vulnerability also affects Android kernels.
  • 🔥 26
Post #386 3.6K
Unprivileged root via a use-after-free in DRM GEM change_handle (CVE-2026-46215)

Stan Shaw published an article about exploiting UAF in a DRM GEM ioctl. The researcher reallocated freed memory as a pipe_buffer array to set PIPE_BUF_FLAG_CAN_MERGE and perform the Dirty Pipe attack.
  • 🔥 10
  • 👍 1
Post #385 3.42K
Off By !: Exploiting a Use-after-Free in the Linux Kernel

Oliver Sieber published a write-up about CVE-2026-23111 in nftables, which they found in early 2025 and other researchers patched upstream in February 2026. The article describes exploiting this UAF on Debian and Ubuntu.
Exodus Intelligence Off By !: Exploiting a Use-after-Free in the Linux Kernel - Exodus Intelligence By Oliver Sieber Overview In this blog post, we discuss a use-after-free vulnerability that we found in the nftables subsystem of the Linux kernel in early 2025. This vulnerability was patched upstream on 5 February 2026 and assigned CVE-2026-23111. This…
  • 👍 6
  • 🔥 4
Post #384 3.29K
CIFSwitch: a non-universal Linux local root vulnerability

Asim Viladi Oglu Manizada posted an article about a nice logic bug in the interaction between the kernel CIFS subsystem and the userspace cifs-utils package.

An attacker can forge a "cifs.spnego" key in Linux keyring to make the kernel run a root userspace helper to escalate privileges of the attacker's process.
Hey, it's Asim CIFSwitch: a non-universal Linux local root vulnerability Harnessing LLMs into composing complex, multihop vulnerability chains to discover CVE-2026-46243
  • 🔥 9
  • 👍 1
  • 🤔 1
Post #383 3.69K
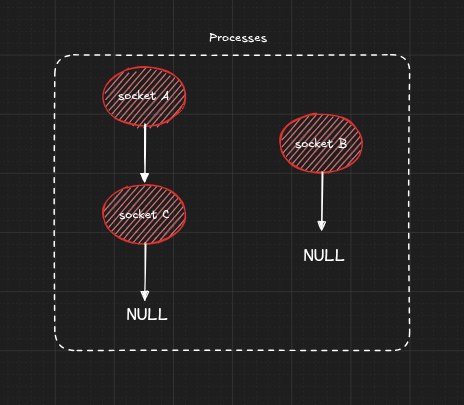
Unix GC Remastered

Article by Moe Acherir about the internals of the new Unix sockets garbage collector implementation and the analysis of CVE-2025-40214, which was used in a kernelCTF entry.
  • 👏 7
Post #381 4.47K
Logic bug in the Linux kernel's __ptrace_may_access() function (CVE-2026-46333)

Article about a logical bug in the ptrace implementation that allows getting access to file descriptors of other processes and thus escalating privileges in certain scenarios.
  • 🔥 15
  • 🤯 4
Post #380 3.66K
StepStone: LLM-Based GPU Kernel Driver Fuzzing via User-Space Libraries

Paper by Xiaochen Zou et. al about using LLMs for generating syzkaller descriptions for fuzzing GPU drivers via their userspace libraries APIs.
  • 🔥 13
Post #379 3.61K
Privilege Escalation via a Page Use-After-Free in Qualcomm's AI Accelerator Linux Kernel Driver

Article by Lukas Maar about exploiting a bug in the mmap handler of the QAIC driver that causes a page UAF.
  • 👍 7
  • 🔥 4
  • 🤯 1
Post #378 3.8K
Discovery & Validation in the Linux Kernel

Three-part article by Samuel Page about analyzing two vulnerabilities (in CAN sockets and FUSE) and attempting to use local LLMs to rediscover the bugs.
  • 🔥 9
Older posts →

About this channel

How can I read @linkersec without a Telegram account?
TGViewer shows the public web preview Telegram publishes for Linux Kernel Security: recent posts, photos, videos and the subscriber count, with no app, login or account.
How many subscribers does Linux Kernel Security have?
Linux Kernel Security (@linkersec) has 4.71K subscribers on Telegram, refreshed roughly every 30 minutes.
Does Linux Kernel Security know I viewed it here?
No. Public channel previews carry no viewer identity, and TGViewer has no accounts or tracking of what you look up.
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →