TGViewer
Channel Public Channel
Linux Kernel Security

Linux Kernel Security

@linkersec

Links related to Linux kernel security and exploitation | Chat @linkersec_chat | @xairy @a13xp0p0v | Mirrors on https://xairy.io/linkersec
Subscribers
4.72K
Photos
122
Videos
0
Links
355

Showing posts older than #254 · Back to latest

Older Posts 20 shown
Post #253 5.52K
A Bug Hunter's Reflections on Fuzzing

Alexander Popov (me) shared the video and slides of the HITBxPHDays talk, where he describes what is special in fuzzing for vulnerability discovery and how to adapt the syzkaller kernel fuzzer for security research.
YouTube A bug hunter's reflections on fuzzing Fuzzing is an incredibly effective and popular technique for testing software. But not all the bugs that it finds are interesting for bug hunters. Fuzzing for vulnerability discovery is special, and in this talk, Alexander will share his reflections on that…
  • 🔥 28
Post #251 5.35K
To Boldly Go Where No Fuzzer Has Gone Before: Finding Bugs in Linux' Wireless Stacks through VirtIO Devices

A paper by Sönke Huster et al. about externally fuzzing the Linux kernel's Wi-Fi and Bluetooth stacks.

The implemented VirtFuzz fuzzer injects Wi-Fi and Bluetooth frames into the kernel through QEMU via a custom VirtIO-based device. The fuzzer also collects coverage via KCOV-based annotations and exposes it to the host via QEMU's shared memory device to guide the fuzzing process.
  • 👍 11
  • 🔥 3
Post #250 4.49K
64 bytes and a ROP chain – A journey through nftables

A two-part article by Davide Ornaghi about finding, analyzing, and exploiting a stack buffer-overflow in the netfilter subsystem from the softirq context.

Davide also gave a talk (slides) about this work at HITB Amsterdam last year.
Betrusted 64 bytes and a ROP chain - A journey through nftables - Part 1 Dive into the process of vulnerability research in the Linux kernel: focus on CVE-2023-0179 and Local Privilege Escalation (LPE).
  • 🔥 8
Post #249 4.27K
Make your own backdoor: CFLAGS code injection, Makefile injection, pkg-config

Vegard Nossum posted a PoC backdoor for the Linux kernel that doesn't require changing the kernel source code or any release tarballs.
  • 👍 4
Post #248 5.61K
Your NVMe Had Been Syz’ed: Fuzzing NVMe-oF/TCP Driver for Linux with Syzkaller

An article by Alon Zahavi about externally fuzzing the NVMe-over-TCP packet parsing paths with syzkaller.

The article:

— Introduces syzkaller and syzlang;
— Shows added syzlang descriptions for NVMe-over-TCP fuzzing, including a new pseudo-syscall;
— Explains how remote KCOV was used to collect coverage from the NVMe packet parsing code executed in a background kernel thread;
— Lists found bugs.
Palo Alto Networks Idira | The Identity Security Platform Protect your organization with Idira®. Modernize identity governance, automate access reviews, and secure every identity across your hybrid cloud environment.
  • 👍 13
  • 🔥 2
Post #247 5.13K
Mind the Patch Gap: Exploiting an io_uring Vulnerability in Ubuntu

An article by Oriol Castejón about exploiting a logical bug in the io_uring subsystem that leads to freed pages being writable through a userspace mapping.

The proposed exploitation approach reclaims the freed pages with a slab filled with file structures for /etc/passwd and modifies them from userspace via the mapping to add a new /etc/passwd entry.

In addition, Yordan Stoychev published an exploit for this bug that uses a different technique.
Exodus Intelligence Mind the Patch Gap: Exploiting an io_uring Vulnerability in Ubuntu - Exodus Intelligence By Oriol Castejón Overview This post discusses a use-after-free vulnerability, CVE-2024-0582, in io_uring in the Linux kernel. Despite the vulnerability being patched in the stable kernel in December 2023, it wasn’t ported to Ubuntu kernels for over two months…
  • 👍 14
  • 🔥 2
Post #246 5.35K
Flipping Pages: An analysis of a new Linux vulnerability in nf_tables and hardened exploitation techniques

An incredibly detailed and well-presented article by notselwyn about exploiting a logical bug in the netfilter subsystem.

The shared exploit leverages the bug to get a page double-free primitive and then execute the Kernel Space Mirroring Attack (KSMA) via a novel Dirty Pagedirectory technique.

The amount of knowledge shared in the article is impossible to encompass in a brief summary, so go check it out yourself! 🔥
Pwning Tech Flipping Pages: An analysis of a new Linux vulnerability in nf_tables and hardened exploitation techniques A tale about exploiting KernelCTF Mitigation, Debian, and Ubuntu instances with a double-free in nf_tables in the Linux kernel, using novel techniques like Dirty Pagedirectory. All without even having to recompile the exploit for different kernel targets…
  • 🔥 14
  • 👍 9
  • 😱 1
Post #245 5.2K
Gaining kernel code execution on an MTE-enabled Pixel 8

An article by Man Yue Mo about exploiting a race condition in the JIT memory regions handling code in the Mali GPU driver.

The shared exploit disables SELinux and gains root privileges from the untrusted_app context on Pixel 8.

In the article, the author also pointed out that MTE (Memory Tagging Extension) does not prevent the exploitation of this bug, as invalid memory accesses happen through the GPU coprocessor.
  • 👍 11
Post #244 4.96K
Mali GPU Kernel LPE

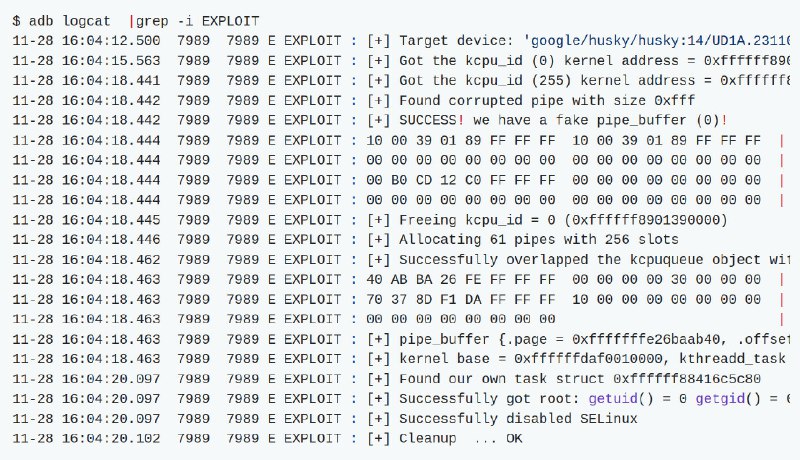
An article by simo about expoiting a kernel pointer leak and an out-of-bounds write bug in the Mali GPU driver.

The shared exploit leverages the pipe_buffer structure to gain arbitrary read/write to disable SELinux and gain root privileges on Pixel 7 and 8 Pro phones.

In the article, the researcher also pointed out the non-transparent and confusing handling of reported vulnerabilities by Google.
  • 🔥 7
  • 👍 4
Post #243 4.77K
SyzRetrospector: A Large-Scale Retrospective Study of Syzbot

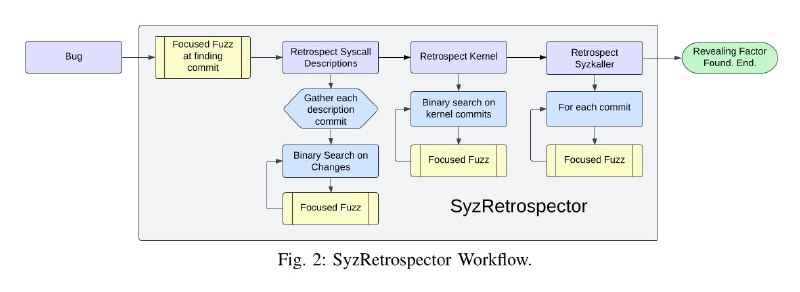
Joseph Bursey, Ardalan Amiri Sani, and Zhiyun Qian published an article analyzing how changes in the Linux kernel and syzkaller influence the ability of syzbot to find bugs.

In the paper, the researchers share the key results of their analysis and offer suggestions on how to improve the syzbot effectiveness.
  • 🔥 4
  • 🤔 2
  • 👍 1
Post #242 6.38K
Linux is a CNA

Greg Kroah-Hartman announced that the Linux kernel project has been accepted as a CVE Numbering Authority (CNA) for vulnerabilities found in Linux.

In his post, Greg referenced the patch documenting the process of CVE allocation and the mailing list where the announcement are published.
  • 🎉 13
  • 👍 5
  • 🤔 1
Post #241 5.87K
CodeQL query to find interesting objects for slab exploitation

A CodeQL script by Jordy Zomer for finding slab allocations of particular size or type.

Eduardo Vela also made a dynamic dashboard based on this script.
  • 👍 13
  • 🔥 3
  • 🤔 1
Post #240 5.51K
KernelGPT: Enhanced Kernel Fuzzing via Large Language Models

A paper by Chenyuan Yang et. al about using the GPT4 LLM neural network for automatically generating syzkaller descriptions.
  • 👍 17
Post #239 6.49K
Linux Kernel GSM Multiplexing Race Condition Local Privilege Escalation Vulnerability (CVE-2023-6546)

An article by Nassim Asrir about exploiting a race condition that leads to a kmalloc-1k use-after-free in the n_gsm TTY line discipline module.

In the exploit, the researcher overwrote the freed object, gained an arbitrary function call with a controlled argument primitive, and escalated privileges by spawning a userspace process via run_cmd.

The exploit bypasses KASLR by leaking the kernel address from world-readable /sys/kernel/notes. This is a separate vulnerability that still affects up-to-date kernels that enable CONFIG_XEN_PV.

To bypass SMAP, the author used a novel technique of filling the kernfs_pr_cont_buf global variable with controlled data from userspace. The data is supplied as the path to a cgroup filter created via iptables, whose use requires unprivileged user namespaces.

The repository with the exploit also contains a set of scripts for automatically extracting symbol offsets for Ubuntu, CentOS, and RHEL kernels.
GitHub GitHub - zerozenxlabs/ZDI-24-020 Contribute to zerozenxlabs/ZDI-24-020 development by creating an account on GitHub.
  • 👍 13
  • 👏 2
  • 🤔 1
Post #238 6.46K
Understanding Dirty Pagetable - m0leCon Finals 2023 CTF Writeup

ptr-yudai published a write-up about exploiting a slab use-after-free on the file structure provided in a CTF challenge.

The researcher used a cross-cache attack and the Dirty Pagetable technique to execute a shellcode in the kernel space, which allowed to gain root privileges and escape from nsjail.
  • 🔥 14
Post #237 6.14K
RetSpill: Igniting User-Controlled Data to Burn Away Linux Kernel Protections

A paper by Kyle Zeng et al. about techniques for saving controlled data on the kernel stack for exploiting control flow hijacking primitives.

The paper also gives an overview of the previously existing approaches for using controlled data with control flow hijacking primitives and the mitigations that affect them.

The authors also developed a semi-automated framework for turning control flow hijacking crashers into privilege escalation exploits based on their techniques.
  • 👏 8
  • 👍 3
  • 🤔 1
Post #236 5.53K
Ubuntu Shiftfs: Unbalanced Unlock Exploitation Attempt

Slides by Jean-Baptiste Cayrou about analyzing an inode locking issue in the shiftfs filesystem in Ubuntu.

The presenter focuses on how they turned the locking issue into a race condition, widened the race window, and caused a slab use-after-free. The researcher also outlines the further exploitation strategy for getting the root privileges.
  • 👍 6
  • 🔥 2
Post #235 4.89K
Conquering the memory through io_uring - Analysis of CVE-2023-2598

An article by Yordan Stoychev about exploiting a logical bug in the io_uring subsystem. The bug leads to the out-of-bounds read/write access to the physical memory.

In the shared exploit, the author leaked and corrupted a sock structure to bypass KASLR and spawn a root shell via call_usermodehelper.
a place of anatomical precision Conquering the memory through io_uring - Analysis of CVE-2023-2598 A logic bug in io_uring leading to Local Privilege Escalation
  • 👍 12
Post #234 4.56K
One shot, Triple kill: Pwning all three Google kernelCTF instances with a single 1-day Linux vulnerability

Slides by Dongok Kim, SeungHyun Lee, and Insu Yun about exploiting a slab use-after-free in the netfilter subsystem.

The researchers managed to exploit all instances of Google's kernelCTF with the same bug, including the instance with advanced custom mitigations.

This research is also available in text form.
Hacking Lab One shot, Triple kill: Pwning all three Google kernelCTF instances with a single 1-day Linux vulnerability | Hacking Lab Desktops, servers, cloud computing services, mobile devices, and IoT devices. Linux is the most popular open-source kernel and is used in various IT platforms. Because of the ubiquitous presence of Linux and the characteristic of the kernel which governs…
  • 🔥 17
  • 👍 1
Post #233 4.71K
Exploring Linux's New Random Kmalloc Caches

An article by sam4k about the new CONFIG_RANDOM_KMALLOC_CACHES mitigation.

The article gives an overview of the currently used slab exploitation techniques, provides a deep analysis of the CONFIG_RANDOM_KMALLOC_CACHES implementation, and reasons about how the new mitigation affects the existing techniques.
sam4k Exploring Linux's New Random Kmalloc Caches Let's explore the modern kernel heap exploitation meta and how the new RANDOM_KMALLOC_CACHES tries to address it.
  • 👍 9
  • 🔥 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →