TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1545 · Back to latest

Older Posts 18 shown
Post #1544 354
🤖 How to evaluate LLMs before production

Practical LLM evaluation lessons from GitHub secret scanning: define product goals and guardrails first, treat offline evaluation as repeatable integration testing, keep eval data close to production, audit labels, use error analysis, and apply LLM-as-judge for human review triage.

https://github.blog/ai-and-ml/llms/how-to-evaluate-llms-before-production

#AI
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1540 346
🔴 Staying Ahead of Adversarial AI Through Agentic Source Code Review

This blog describes the methodology that powers a Mandiant internal tool for point-in-time AI vulnerability discovery. It has discovered hundreds of vulnerabilities in customer codebases and resulted in dozens of vendor notifications with either assigned or pending CVE numbers.

https://cloud.google.com/blog/topics/threat-intelligence/staying-ahead-of-adversarial-ai-through-agentic-source-code-review

#gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1539 315
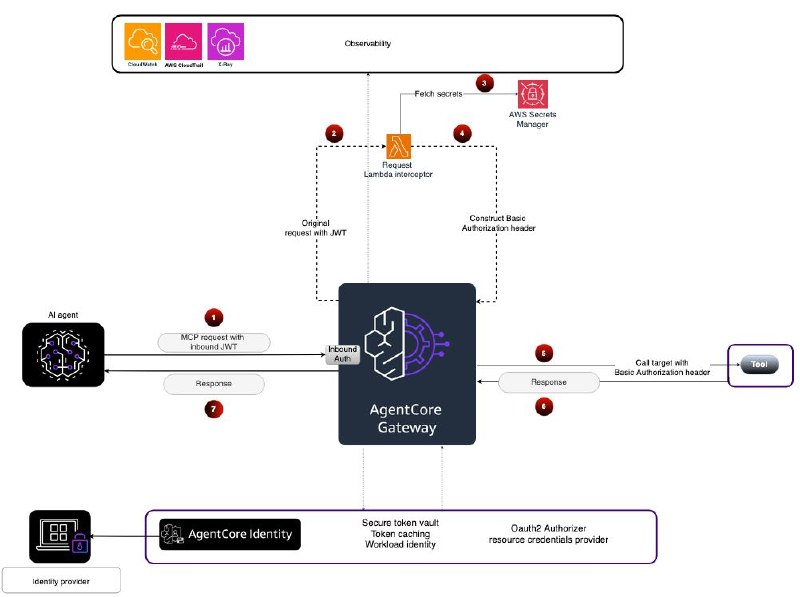
🔶 Implement custom authentication for tools integration using request Lambda interceptor in AgentCore Gateway

AgentCore Gateway supports OAuth 2.0, IAM, and API keys natively, but a request Lambda interceptor enables legacy Basic Auth integration. The interceptor validates the inbound JWT, retrieves system credentials from Secrets Manager, and constructs the Basic Auth header before forwarding to the downstream tool.

https://aws.amazon.com/ru/blogs/security/implement-custom-authentication-for-tools-integration-using-request-lambda-interceptor-in-agentcore-gateway

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1537 361
🤖 Putting models to the secure coding test: Plan vs default mode

Datadog tested Claude Sonnet 5, Composer 2.5, and GPT 5.5 in plan vs. default mode for secure code generation. No meaningful correlation between plan mode and improved security was found; explicit prompt-level security constraints had greater impact than mode selection.

https://securitylabs.datadoghq.com/articles/putting-models-to-the-secure-coding-test-plan-vs-default-mode

#AI
  • 👍 3
  • ❤ 1
  • 🔥 1
Post #1536 351
🔶 Threat hunt AI: How we built an AI security analyst on AWS for under $500/month

Grow Therapy built a Claude-powered threat hunting system on ECS Fargate and Lambda, querying Snowflake and Datadog logs across 15 sources. A five-phase AI pipeline (data gathering, baseline comparison, enrichment, confidence scoring, adversarial validation) reduces false positives. Total cost: under $500/month.

https://engineering.growtherapy.com/post/threat-hunt-ai-how-we-built-an-ai-security-analyst-on-aws-for-under-500-month

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1535 396
⚠️ Going depthfirst: Achieving GitLab RCE via Two Ruby Memory. Corruption Vulnerabilities

Researchers chained two memory-safety flaws in Oj, into remote code execution in a Puma worker. The path begins with an attacker-controlled Jupyter notebook and crosses GitLab, ipynbdiff, CRuby, and jemalloc before reaching function-pointer control.

https://depthfirst.com/research/going-depthfirst-achieving-gitlab-rce-via-two-ruby-memory-corruption-vulnerabilities

#RCE
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1534 355
🤖 Building an Advanced Agentic Harness

How to build a production-grade agentic harness using typed Pydantic tools, a DAG planner with parallel asyncio execution, tiered memory, Planner/Worker/Critic role separation, multi-dimensional budgeting with graceful degradation, and structured tracing for observability.

https://data4sci.com/blog/building-an-advanced-agentic-harness

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1532 351
🔶 How AWS IAM role manager rethinks the starting point for IAM roles

AWS IAM role manager automates IAM role creation within supported service consoles, eliminating manual role setup. Using managed role templates and a new AcquireRole API, it provisions and attaches least-privilege roles automatically. Roles remain fully customer-controlled and refinable via IAM Access Analyzer.

https://aws.amazon.com/ru/blogs/security/how-aws-iam-role-manager-rethinks-the-starting-point-for-iam-roles

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1531 306
🤖 Orchestrating AI Code Review at scale

Cloudflare built a CI-native AI code review system using OpenCode, orchestrating up to 7 specialised agents (security, performance, code quality, etc.) per merge request.

https://blog.cloudflare.com/ai-code-review

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1530 414
🔶 HIPAA Security Rule on AWS

AWS released a whitepaper guiding covered entities and business associates on implementing HIPAA Security Rule Technical Safeguards on AWS, covering access control, audit, MFA, encryption, and 2025 NPRM proposed changes, with shared responsibility mapping and ePHI architecture guidance.

https://aws.amazon.com/ru/blogs/security/hipaa-security-rule-on-aws-technical-safeguards-implementation-and-readiness-guidance

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1529 359
🔴 Cloud CISO Perspectives: Why AI Threat Defense is the new boardroom baseline

Google Cloud CISO Chris Betz argues that AI-native threat defense is now a board-level requirement. Boards should govern five areas: business enablement, remediation cycle speed, platform consolidation, contextual vulnerability prioritization, and AI safety policy to enable secure, AI-driven business agility.

https://cloud.google.com/blog/products/identity-security/cloud-ciso-perspectives-why-ai-threat-defense-is-the-new-boardroom-baseline

#gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1528 365
👩‍💻 CosmosEscape: Taking Over Every Azure Cosmos DB

Wiz Research found CosmosEscape, a critical vulnerability in Azure Cosmos DB's Gremlin API enabling sandbox escape via .NET reflection. Attackers could obtain a platform-wide Cosmos Master Key granting full read/write access to any customer database and enumeration of all accounts.

https://www.wiz.io/blog/cosmosescape-taking-over-every-database-in-azure-cosmos-db

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1526 367
🔶 Investigating Persistence Mechanisms in AWS

Rapid7 Labs details four AWS persistence techniques used by attackers: rogue IAM user creation, backdoored assume role policies granting external account access, malicious Lambda functions provisioning privileged users, and federated user sessions that survive key rotation. Includes LEQL detection queries and remediation steps.

https://www.rapid7.com/blog/post/dr-investigating-aws-persistence-mechanisms

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →