TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1524 · Back to latest

Older Posts 14 shown
Post #1523 370
🤖 A Security Analysis of Amazon S3 Vectors and Its Use in LLM Retrieval Pipelines

An analysis of the security model of Amazon S3 Vectors and of the considerations that arise when it is used as the retrieval layer for LLM applications: access control scope, input validation, metadata integrity, and audit coverage.

https://www.offensai.com/blog/amazon-s3-vectors-security-llm-rag-poisoning

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1521 364
🤖 Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident

A companion technical writeup to HunggingFace's incident disclosure from last week. This post walks through how the intrusion actually worked: the two initial-access vectors, how the agent pivoted and moved laterally, representative examples of the commands that were run and how they investigated with GLM 5.2.

https://huggingface.co/blog/agent-intrusion-technical-timeline

#AI
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1519 361
🤖 Least privilege for AI agents: Identity, access, and tool binding

AI agents acting as autonomous multi-system actors require dedicated managed identities, least-privilege task-scoped RBAC, explicit tool allowlists, JIT time-limited entitlements, downstream re-authorization per call, and end-to-end audit logs capturing identity, role, scope, and correlation IDs.

https://www.microsoft.com/en-us/security/blog/2026/07/16/least-privilege-for-ai-agents-identity-access-and-tool-binding

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1518 347
🤖 Inside the OpenClaw Ecosystem: What Happens When AI Agents Get Credentials to Everything

Permiso researchers deployed an AI agent (Rufio) into the OpenClaw ecosystem and found active malware campaigns in its unvetted skill marketplace (ClawHub), credential-harvesting skills with 377+ downloads, C2 infrastructure, and prompt injection attacks targeting agents holding plaintext credentials to email, Slack, and file systems.

https://permiso.io/blog/inside-the-openclaw-ecosystem-ai-agents-with-privileged-credentials

#AI
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1517 382
🤖 New Study Identifies 53 Slopsquatting Targets Across 5 Frontier LLMs

A study of ~200,000 LLM responses found 5 frontier models (Claude, GPT, Gemini, DeepSeek) hallucinate nonexistent package names at 4.62-6.10%, with 53 shared fictitious names on PyPI/npm still registrable and exploitable via slopsquatting attacks.

https://socket.dev/blog/slopsquatting-targets-across-frontier-llms

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1515 390
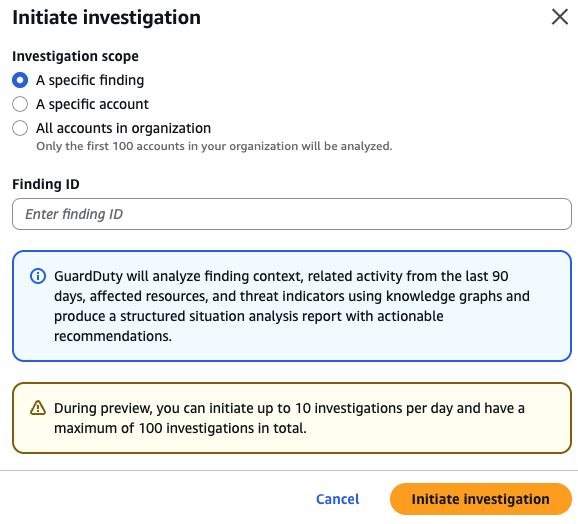
🔶 Introducing the Amazon GuardDuty investigation agent: on-demand AI-powered threat assessment

Amazon GuardDuty investigation agent (public preview) uses AI to auto-investigate GuardDuty security findings, reducing investigation time from hours to minutes. It returns risk levels, confidence scores, MITRE ATT&CK mappings, and remediation steps via console, CLI, API, or AWS MCP server.

https://aws.amazon.com/ru/blogs/security/introducing-the-amazon-guardduty-investigation-agent-on-demand-ai-powered-threat-assessment

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1511 352
🤖 Delegated authority, running locally: Give an agent on your machine an identity you can trust

A reference architecture for giving a locally-running AI agent a trustworthy, auditable identity, without long-lived credentials on disk, including a structural defense against prompt injection built into the protocol layer.

https://1password.com/blog/ai-agent-identity-delegated-local

#AI
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1510 365
🤖 CISO's guide to agentic AI

Anthropic's Deputy CISO shares a four-question framework for assessing agentic AI risk, and walks through controls that keep agent deployments bounded and auditable.

https://claude.com/blog/ciso-guide-to-agentic-ai

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1507 397
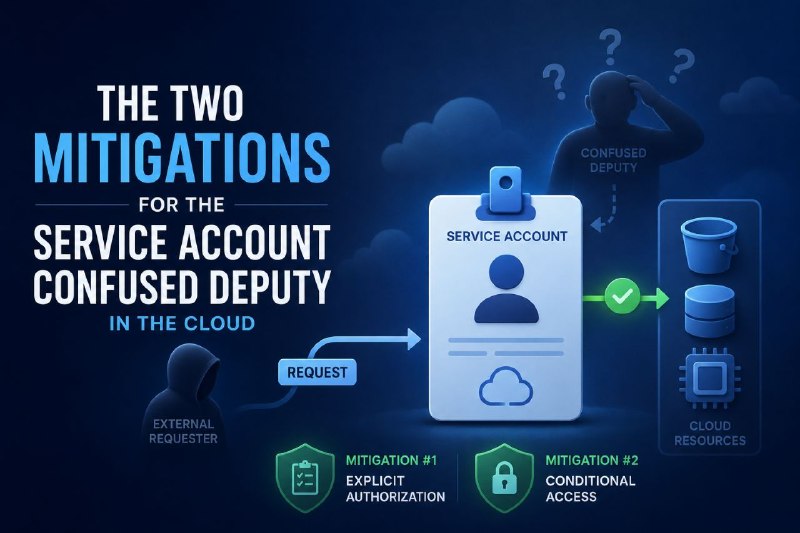
🔶🔷🔴 The Two Mitigations for the Service-Account Confused Deputy in the Cloud

Two mitigations exist for cloud service-account confused deputy attacks: for customer-managed identities, an attachment gate (GCP actAs, AWS iam:PassRole, Azure assign/action) controls bind-time authorization; for provider-managed identities, the CSP enforces internal checks, with AWS uniquely exposing this via Forward Access Sessions and condition keys.

https://kattraxler.cloud/the-two-mitigations-for-the-service-account-confused-deputy-in-the-cloud

#aws #azure #gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1505 366
🔶 Authenticate legitimate AI agent traffic with AWS WAF Bot Control

AWS WAF Bot Control now supports Web Bot Authentication (WBA), using ed25519 cryptographic signatures (RFC 9421) to verify AI agent identities. It introduces new WAF labels (verified, invalid, expired, unknown_bot) enabling granular allow/block rules, replacing unreliable IP-based bot filtering.

https://aws.amazon.com/ru/blogs/security/authenticate-legitimate-ai-agent-traffic-with-aws-waf-bot-control

#aws
  • ❤ 3
  • 👍 1
  • 🔥 1
Post #1501 328
👩‍💻 No single pane of glass: Anatomy of an Azure permission takeover

Sysdig TRT observed an attacker use one leaked service principal (with RoleManagement.ReadWrite.Directory) to self-grant Global Administrator, then elevateAccess to root RBAC Owner, harvest storage/Event Hub/Key Vault keys, and plant backdoors on 26 app registrations.

https://www.sysdig.com/blog/no-single-pane-of-glass-anatomy-of-an-azure-permission-takeover

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →