TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K
Recent Posts 15 shown
Post #1566 135
🤖 OpenAI's Defense Factory

OpenAI's Defense Factory is a continuous, agent-first vulnerability detection and remediation pipeline using Codex and specialized cyber models (Daybreak Blue/Red). It automates inventory, triage, dynamic validation, ownership assignment, and verified patching, achieving 0.81% false-positive rate and 0.53% fix rollback rate.

https://openai.com/ru-RU/the-defense-factory

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1564 174
🤖 Detecting and countering misuse of AI: September 2026

Anthropic's September 2026 threat report covers disrupted misuse of Claude (Dec 2025-Aug 2026) across seven harm areas: AI-augmented cyber ops by state and criminal actors, influence operations across six continents, surveillance platforms targeting dissidents, conventional weapons software development, dual-use biological research, fraud/scams, and illicit distillation by PRC AI labs including Alibaba, DeepSeek, Moonshot, and Zhipu.

https://www.anthropic.com/threat-intelligence-report-september-2026

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1563 241
🤖 ASCII smuggling crosses over from AI prompt injection to phishing evasion

Microsoft researchers discovered a high-volume phishing campaign that repurposed ASCII smuggling to split financial keywords like "funding" and evade email filters, generating over 2.3 million messages daily at its February 2026 peak.

https://www.microsoft.com/en-us/security/blog/2026/09/03/ascii-smuggling-crosses-over-from-ai-prompt-injection-to-phishing-evasion

#AI
  • ❤ 3
  • 🔥 1
  • 👏 1
Post #1558 236
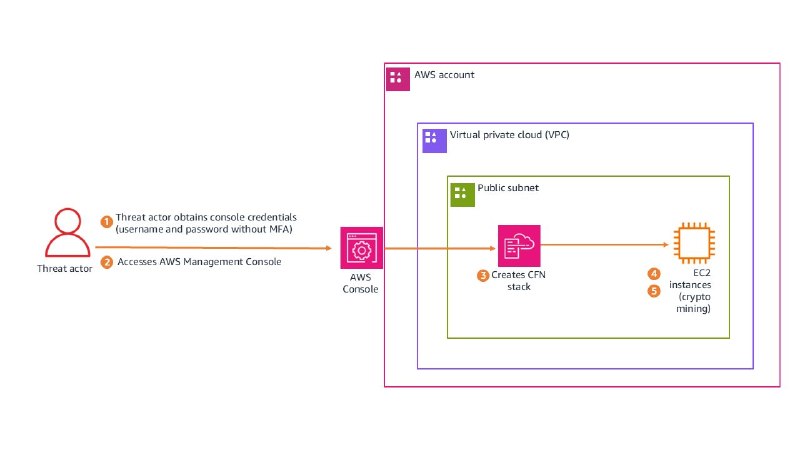
🔶 Incident response guide for AWS CloudTrail investigations

AWS's Security Incident Response Team (SIRT) walks through two real-world CloudTrail investigation scenarios, cross-account S3 data deletion with ransomware implications and cryptocurrency mining via stolen console credentials, teaching investigators how to read key log fields, recognize attacker patterns, and apply practical response checklists. You can also check out Part 2.


https://aws.amazon.com/ru/blogs/security/incident-response-guide-for-aws-cloudtrail-investigations-part-1

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1557 238
🔶 A scenario to evaluate your Agentic SOC

A downloadable multi-source log dataset built around a 7-phase GitHub Actions cache poisoning → Kubernetes → AWS attack chain, used to benchmark agentic SOC harnesses.

https://unsecure.sh/blog/agentic-soc-scenario/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1555 308
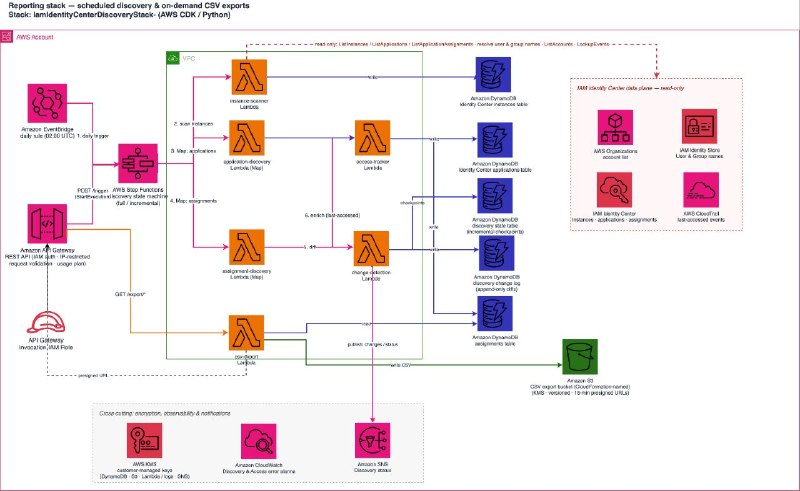
🔶 Automate IAM Identity Center governance with continuous discovery and reporting

A walkthrough deploying two AWS CDK stacks for IAM Identity Center governance: a reporting stack (EventBridge, Step Functions, Lambda, DynamoDB, API Gateway, S3) for automated daily discovery and CSV export, and a remediation stack for real-time event-driven enforcement and SNS notifications on non-compliant application assignments.

https://aws.amazon.com/ru/blogs/security/automate-iam-identity-center-governance-with-continuous-discovery-and-reporting

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1554 310
🔶 Extend your data perimeter to the AWS Management Console with Private Access

AWS Management Console Private Access is now GA, routing all console traffic (auth, static assets, service APIs) through AWS PrivateLink VPC endpoints with no internet path required. VPC endpoint policies and Sign-In RCPs enforce identity, resource, and network perimeter controls on interactive console sessions.

https://aws.amazon.com/ru/blogs/security/extend-your-data-perimeter-to-the-aws-management-console-with-private-access

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1553 282
🤖 Amazon Kiro: AI Is Breaking Vulnerability Disclosure Processes

A prompt injection flaw in Amazon Kiro IDE v0.7.45 allowing attacker-controlled repository content to exfiltrate sensitive data via the powersRecommendationUrl setting and Kiro Powers, exploitable in both trusted and untrusted workspaces.

https://mindgard.ai/blog/amazon-kiro-data-exfiltration

#AI
  • 🔥 3
  • ❤ 1
  • 👍 1
Post #1547 337
🔶 From clickops to governed IaC: CloudFormation drift detection in practice

A guide for migrating ClickOps-managed AWS infrastructure to governed CloudFormation IaC using IaC Generator for template generation, stack organization by lifecycle/ownership, and automated drift detection via EventBridge for continuous compliance monitoring.

https://aws.amazon.com/ru/blogs/devops/from-clickops-to-governed-iac-cloudformation-drift-detection-in-practice

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1545 289
🔶 Detecting multi-stage attacks on AWS: A guide to cross-service signal correlation

A guide to detecting multi-stage AWS attacks by correlating signals across CloudTrail, VPC Flow Logs, and Route 53 DNS logs. Covers four business-context-aware patterns: unexpected S3 access, abnormal role chains, KMS key misuse, and off-hours privileged changes, with CloudWatch Logs Insights queries and Lambda automation.

https://aws.amazon.com/ru/blogs/security/detecting-multi-stage-attacks-on-aws-a-guide-to-cross-service-signal-correlation

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Older posts →

About this channel

How can I read @cloud_sec without a Telegram account?
TGViewer shows the public web preview Telegram publishes for CloudSec Wine: recent posts, photos, videos and the subscriber count, with no app, login or account.
How many subscribers does CloudSec Wine have?
CloudSec Wine (@cloud_sec) has 2.27K subscribers on Telegram, refreshed roughly every 30 minutes.
Does CloudSec Wine know I viewed it here?
No. Public channel previews carry no viewer identity, and TGViewer has no accounts or tracking of what you look up.
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →