TGViewer
CloudSec Wine CloudSec Wine @cloud_sec · 2.27K subscribers
Post #1558 236
🔶 Incident response guide for AWS CloudTrail investigations

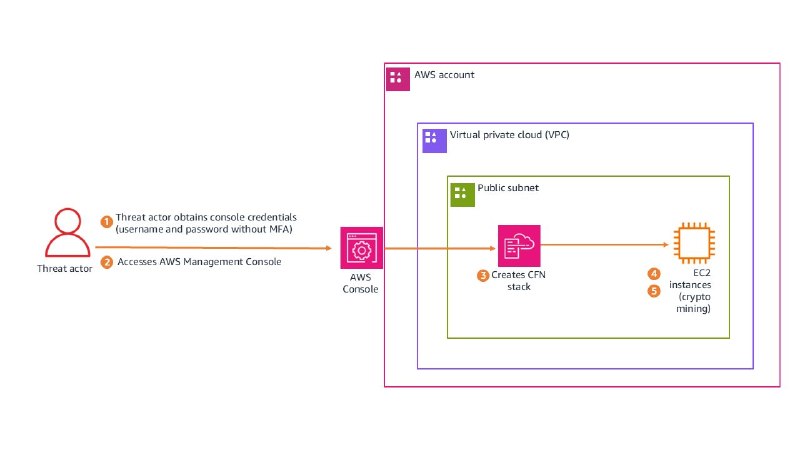
AWS's Security Incident Response Team (SIRT) walks through two real-world CloudTrail investigation scenarios, cross-account S3 data deletion with ransomware implications and cryptocurrency mining via stolen console credentials, teaching investigators how to read key log fields, recognize attacker patterns, and apply practical response checklists. You can also check out Part 2.


https://aws.amazon.com/ru/blogs/security/incident-response-guide-for-aws-cloudtrail-investigations-part-1

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
More from @cloud_sec
  1. Sep 22, 2026🤖 OpenAI's Defense Factory OpenAI's Defense Factory is a continuous, agent-first vulnerab…
  2. Sep 21, 2026🤖 Detecting and countering misuse of AI: September 2026 Anthropic's September 2026 threat…
  3. Sep 18, 2026🤖 ASCII smuggling crosses over from AI prompt injection to phishing evasion Microsoft res…
  4. Sep 17, 2026🤖 GTIG AI Threat Tracker: From Prompting to Autonomy This AI threat update provides GTIG'…
  5. Sep 16, 2026🔶 Agentic SOC alert triage: 60% to 92% AI accuracy Elastic's InfoSec team describes how e…
  6. Sep 14, 2026🔶 A scenario to evaluate your Agentic SOC A downloadable multi-source log dataset built a…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →