TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1480 · Back to latest

Older Posts 16 shown
Post #1478 474
🔶 Amazon S3 annotations: attach rich, queryable context directly to your object

Amazon S3 now lets you attach up to 1 GB of rich, mutable, and queryable context directly to your objects using annotations, purpose-built for AI agents and autonomous workflows that need to discover, understand, and act on data at scale without maintaining separate metadata systems.

https://aws.amazon.com/ru/blogs/aws/amazon-s3-annotations-attach-rich-queryable-context-directly-to-your-objects

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1477 402
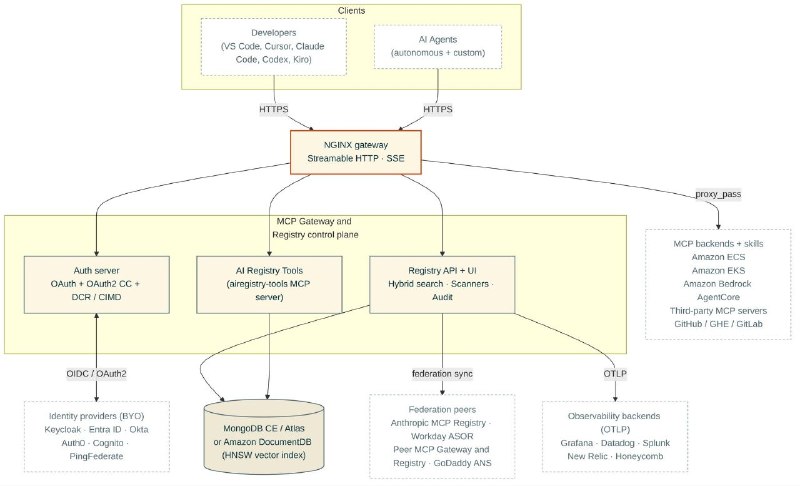
🔶 Governing AI Assets at Scale with MCP Gateway and Registry

Open source MCP Gateway and Registry (Apache 2.0) provides enterprise governance for AI assets (MCP servers, agents, skills) via centralized discovery, fine-grained RBAC, supply-chain security scanning, hybrid semantic/keyword search, OpenTelemetry observability, federation with external registries, and deployable on EKS/ECS/EC2.

https://aws.amazon.com/ru/blogs/opensource/governing-ai-assets-at-scale-with-mcp-gateway-and-registry

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1473 384
🤖 AI Agent Supply-Chain Malware in Instruction Files

Mitiga Labs scanned 50,000+ AI instruction files across 7,000+ repos, finding prompt-exfiltration malware, ANTHROPIC_BASE_URL MITM overrides, YOLO-mode permission bypasses, and 1,230+ hardcoded API keys. They released Skillgate, a free scanner, to detect these techniques.

https://www.mitiga.io/blog/malware-in-ai-instruction-files-skillgate

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1470 420
🤖 Entra Agent ID: The blueprint blast radius

Entra Agent ID is an extension of Entra's application model that provides identities for AI agents. Unlike applications, the agent identity model allows linking a single app registration (blueprint) to multiple identities and their associated privileges, increasing the potential blast radius of a compromised agent.

https://securitylabs.datadoghq.com/articles/agent-id-blueprint-blast-radius

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1468 456
🌩 Securing CI/CD in an agentic world: Claude Code Github action case

Microsoft Threat Intelligence identified a prompt injection pathway in Claude Code GitHub Action that allowed access to workflow secrets under specific conditions. This research examines the attack chain, responsible disclosure process, Anthropic's mitigation, and guidance for securing AI-powered CI/CD workflows.

https://www.microsoft.com/en-us/security/blog/2026/06/05/securing-ci-cd-in-agentic-world-claude-code-github-action-case

#ClaudeCode
  • 👍 3
  • ❤ 1
  • 🔥 1
Post #1467 398
🔶 Operationalizing AWS security: A maturity roadmap

A six-phase maturity roadmap for operationalizing AWS Security Hub and GuardDuty: assess current state, reduce alert noise via tuning, build tiered notification routing, implement automated remediation for high-confidence findings, establish recurring review cadences with metrics, then expand with Inspector, Macie, Security Lake, and preventive controls.

https://aws.amazon.com/ru/blogs/security/operationalizing-aws-security-a-maturity-roadmap

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1465 447
🔐 Identity and Access Management Whitepaper

CNCF TAG Security released an IAM whitepaper targeting architects and platform engineers, covering zero-trust vs. perimeter models, PEP/PDP-based authorization, SPIFFE workload identity, and authentication patterns for stateful and stateless cloud native workloads.

https://www.cncf.io/blog/2026/06/04/identity-and-access-management-whitepaper

#iam
  • ❤ 2
  • 👍 2
  • 🔥 1
Post #1464 574
🌩 Hidden Gaps in Claude Code Security Reviews

Claude Code's /security-review is vulnerable to model anchoring bias when run in the same session that wrote the code. A new diff-scoped plugin avoids this but misses cross-commit vulnerability chains where each individual change appears benign in isolation.

https://brainoverflow.blog/posts/claude-code-security-review-bias

#ClaudeCode
  • 👍 4
  • ❤ 1
  • 🔥 1
Post #1457 485
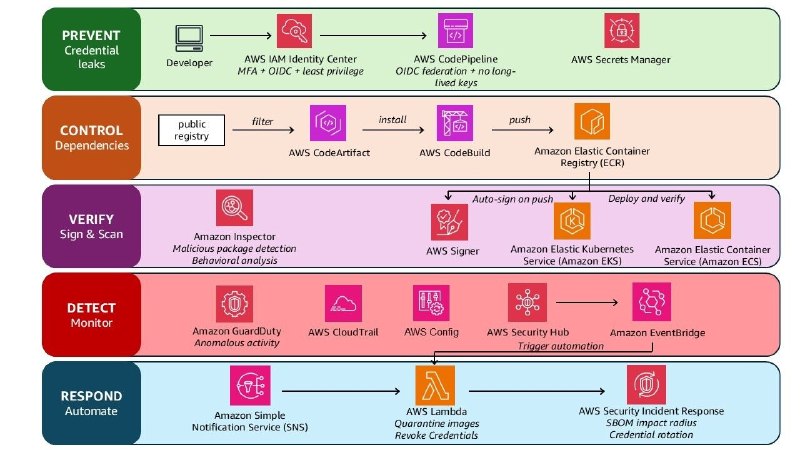
🔶 Well-architected best practices for software supply chain security

Aligned with the AWS Well-Architected Security Pillar, the article recommends defending against npm supply chain attacks (e.g., Shai-Hulud) by using temporary credentials, least-privilege IAM, artifact signing via AWS Signer, centralized dependency management with CodeArtifact, continuous scanning via Amazon Inspector, and CloudTrail-based monitoring.

https://aws.amazon.com/ru/blogs/security/well-architected-best-practices-for-software-supply-chain-security

#aws
  • 👍 3
  • ❤ 2
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →