TGViewer
CloudSec Wine CloudSec Wine @cloud_sec · 2.27K subscribers
Post #1457 485
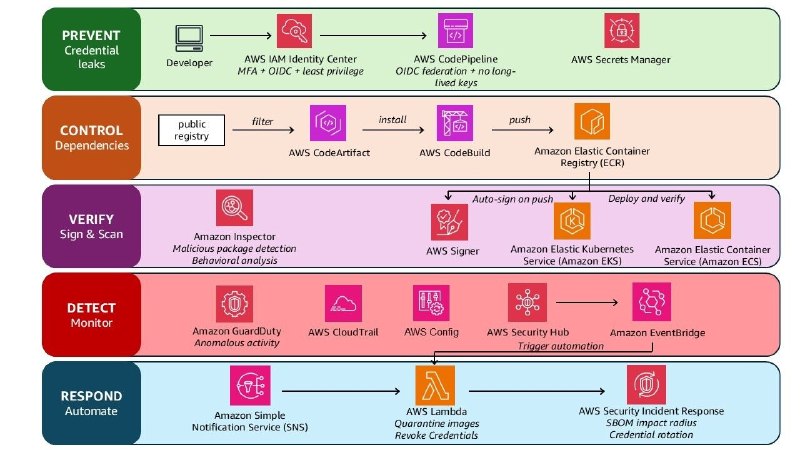
🔶 Well-architected best practices for software supply chain security

Aligned with the AWS Well-Architected Security Pillar, the article recommends defending against npm supply chain attacks (e.g., Shai-Hulud) by using temporary credentials, least-privilege IAM, artifact signing via AWS Signer, centralized dependency management with CodeArtifact, continuous scanning via Amazon Inspector, and CloudTrail-based monitoring.

https://aws.amazon.com/ru/blogs/security/well-architected-best-practices-for-software-supply-chain-security

#aws
  • 👍 3
  • ❤ 2
  • 🔥 1
More from @cloud_sec
  1. Sep 23, 2026🤖 Hacking AI customer service agents Techniques for attacking AI customer service agents:…
  2. Sep 22, 2026🤖 OpenAI's Defense Factory OpenAI's Defense Factory is a continuous, agent-first vulnerab…
  3. Sep 21, 2026🤖 Detecting and countering misuse of AI: September 2026 Anthropic's September 2026 threat…
  4. Sep 18, 2026🤖 ASCII smuggling crosses over from AI prompt injection to phishing evasion Microsoft res…
  5. Sep 17, 2026🤖 GTIG AI Threat Tracker: From Prompting to Autonomy This AI threat update provides GTIG'…
  6. Sep 16, 2026🔶 Agentic SOC alert triage: 60% to 92% AI accuracy Elastic's InfoSec team describes how e…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →