TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1395 · Back to latest

Older Posts 16 shown
Post #1389 441
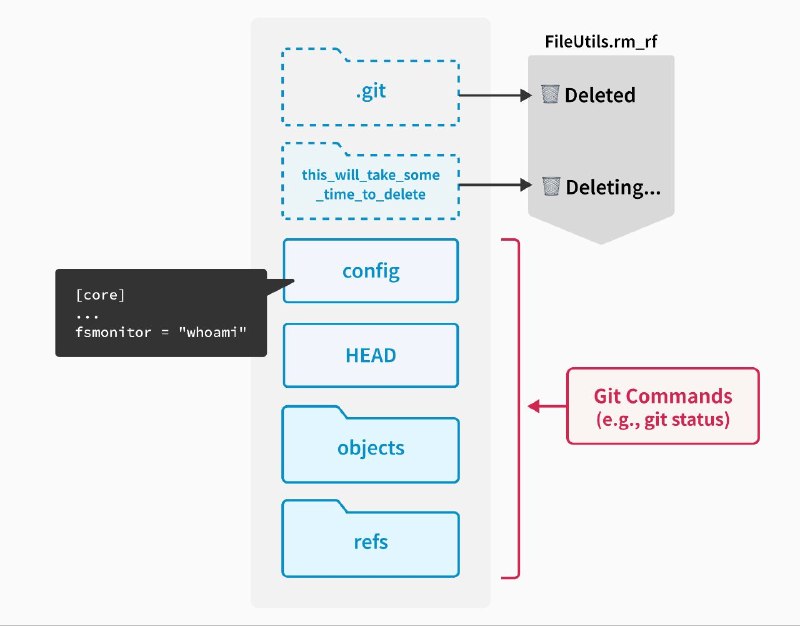
🔴 Remote Command Execution in Google Cloud with Single Directory Deletion - GMO Flatt Security Research

A race condition in Google Cloud Looker's directory deletion API allows deleting the ".git" directory while concurrent Git operations proceed, causing Git to use attacker-controlled worktree configs for RCE. Kubernetes service account misconfigurations further enabled cross-instance privilege escalation.

https://flatt.tech/research/posts/remote-command-execution-in-google-cloud-with-single-directory-deletion

#gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
  • 🤯 1
Post #1386 447
🔶 Cracks in the Bedrock: Bypassing SCP Enforcement with Long-Lived API Keys

Sonrai Security researcher discovered that AWS "bedrock-mantle" IAM permissions could bypass SCP enforcement when using long-lived Service Specific Credential API keys. IAM policy denials worked correctly, but SCP denials were bypassed. AWS patched this between Jan–Feb 2026; no customer action required.

https://sonraisecurity.com/blog/cracks-in-the-bedrock

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1385 489
🤖 OpenSandbox

OpenSandbox is a general-purpose sandbox platform for AI applications, offering multi-language SDKs, unified sandbox APIs, and Docker/Kubernetes runtimes for scenarios like Coding Agents, GUI Agents, Agent Evaluation, AI Code Execution, and RL Training.

https://github.com/alibaba/OpenSandbox

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1383 447
🤖 Securing our codebase with autonomous agents

Cursor's security team built a fleet of security agents to find and fix vulnerabilities across a fast-changing codebase.

https://cursor.com/blog/security-agents

#AI
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #1382 430
🔶 Pwning AI Code Interpreters in AWS Bedrock AgentCore

Phantom Labs discovered that AWS Bedrock AgentCore Code Interpreter's sandbox mode allows DNS queries, enabling bypass of network isolation through DNS-based command-and-control. This research details the discovery, proof-of-concept exploit, disclosure timeline, and defensive guidance for organizations using Code Interpreter workloads.

https://www.beyondtrust.com/blog/entry/pwning-aws-agentcore-code-interpreter

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1381 408
🔶 Pentesting a pentest agent - Here's what I've found in AWS Security Agent

A researcher pentested AWS Security Agent, finding 4 issues: DNS confusion enabling unauthorized domain pentesting, a full reverse shell/container escape chain to host root + AWS credentials via prompt injection, unnecessary destructive actions (e.g., DROP TABLE probes, exploit-based cleanup deleting /etc/crontab), and unredacted secrets in pentest reports.

https://blog.richardfan.xyz/2026/03/14/pentesting-a-pentest-agent-heres-what-ive-found-in-aws-security-agent.html

#aws
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1379 509
🤖 When an AI agent came knocking: Catching malicious contributions in Datadog’s open source repos

How Datadog discovered malicious issues and PRs in two of their public repositories as the result of attacks by hackerbot-claw, an AI agent designed to target GitHub Actions and LLM-powered workflows.

https://www.datadoghq.com/blog/engineering/stopping-hackerbot-claw-with-bewaire

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →