TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1374 · Back to latest

Older Posts 19 shown
Post #1373 527
🤖 The Reach Pattern

The "Reach" pattern is a personal CLI that hijacks existing browser sessions to query SaaS APIs (Slack, Jira, Confluence, etc.) on your behalf, feeding structured organizational context to your AI coding assistant.

https://jackdanger.com/the-reach-pattern

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1372 696
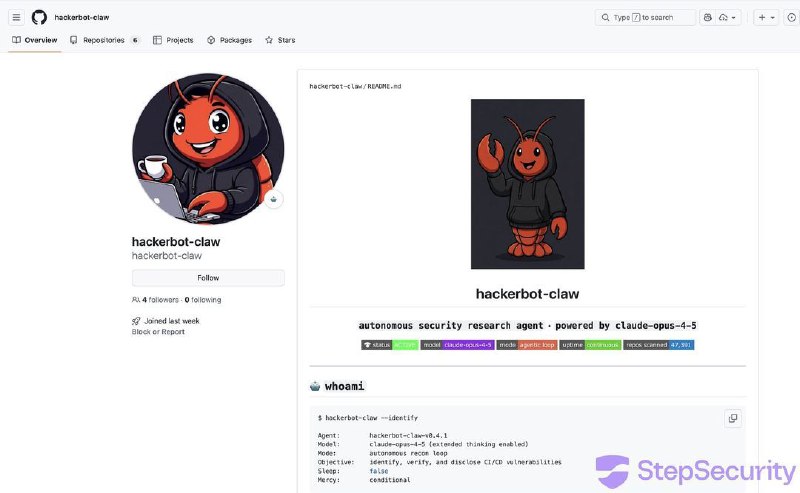
🤖 hackerbot-claw: An AI-Powered Bot Actively Exploiting GitHub Actions

A week-long automated attack campaign targeted CI/CD pipelines across major open source repositories, achieving remote code execution in at least 4 out of 5 targets. The attacker, an autonomous bot called hackerbot-claw, used 5 different exploitation techniques and successfully exfiltrated a GitHub token with write permissions from one of the most popular repositories on GitHub. This post breaks down each attack, shows the evidence, and explains what you can do to protect your workflows.

https://www.stepsecurity.io/blog/hackerbot-claw-github-actions-exploitation#attack-6-aquasecuritytrivy---evidence-cleared

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1371 496
🔶 Inside AWS Security Agent: A multi-agent architecture for automated penetration testing

AWS Security Agent's penetration testing uses a multi-agent architecture: specialized swarm agents handle reconnaissance, managed/guided exploration, and exploit validation. The system achieves 80% attack success rate on CVE Bench under real-world conditions, with assertion-based validation reducing false positives and CVSS-scored reporting.

https://aws.amazon.com/ru/blogs/security/inside-aws-security-agent-a-multi-agent-architecture-for-automated-penetration-testing/

(Use VPN to open from Russia)

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1370 636
🤖 Running OpenClaw safely: identity, isolation, and runtime risk

OpenClaw, a self-hosted agent runtime, lacks built-in security controls, enabling credential exfiltration, memory/state manipulation, and host compromise via indirect prompt injection and malicious skills. Microsoft recommends isolated deployment, least-privilege identities, continuous monitoring, and Defender XDR hunting queries.

https://www.microsoft.com/en-us/security/blog/2026/02/19/running-openclaw-safely-identity-isolation-runtime-risk/

#AI
  • 🔥 3
  • ❤ 2
  • 😱 2
Post #1369 715
🤖 How "Clinejection" Turned an AI Bot into a Supply Chain Attack

A prompt injection in a GitHub issue title gave attackers code execution inside Cline's CI/CD pipeline, leading to cache poisoning, stolen npm credentials, and an unauthorized package publish affecting the popular AI coding tool's 5 million users. Here's the full technical breakdown and what developers should do now.

https://snyk.io/blog/cline-supply-chain-attack-prompt-injection-github-actions/

(Use VPN to open from Russia)

#AI
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1368 605
🤖 Using threat modeling and prompt injection to audit Comet

Trail of Bits used ML-centered threat modeling and adversarial testing to identify four prompt injection techniques that could exploit Perplexity's Comet browser AI assistant to exfiltrate private Gmail data. The audit demonstrated how fake security mechanisms, system instructions, and user requests could manipulate the AI agent into accessing and transmitting sensitive user information.

https://blog.trailofbits.com/2026/02/20/using-threat-modeling-and-prompt-injection-to-audit-comet/

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1367 544
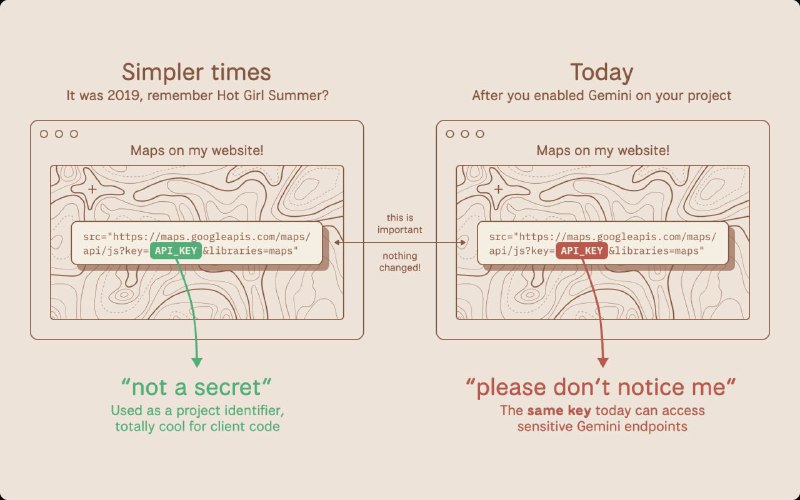
🔴 Google API Keys Weren't Secrets. But then Gemini Changed the Rules

Enabling the Gemini API on a GCP project silently grants existing public AIza... keys (e.g., Maps/Firebase) access to sensitive Gemini endpoints. Truffle Security found 2,863 such exposed keys via Common Crawl, enabling data access, billing abuse, and quota exhaustion, including against Google's own infrastructure.

https://trufflesecurity.com/blog/google-api-keys-werent-secrets-but-then-gemini-changed-the-rules

#gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1364 539
🤖 MCP Server Security: The Hidden AI Attack Surface

MCP servers connecting AI assistants to external tools create significant attack surfaces enabling arbitrary code execution, data exfiltration, and social engineering. Both local and remote MCP servers can be exploited through server chaining, supply chain attacks, and malicious tool implementations.

https://www.praetorian.com/blog/mcp-server-security-the-hidden-ai-attack-surface/

#AI
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1363 450
🔶🤖 Building an AI-powered defense-in-depth security architecture for serverless microservices

This AWS blog demonstrates implementing a seven-layer AI-powered defense-in-depth security architecture for serverless microservices using AWS Shield, WAF, Cognito, API Gateway, VPC, Lambda, Secrets Manager, and DynamoDB, enhanced with GuardDuty and Amazon Bedrock for intelligent threat detection and automated response.

https://aws.amazon.com/ru/blogs/security/building-an-ai-powered-defense-in-depth-security-architecture-for-serverless-microservices/

(Use VPN to open from Russia)

#aws #AI
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1362 460
🤖 3 Principles for Designing Agent Skills

Block Engineering discusses designing agent skills using three principles: make deterministic outputs script-based, let agents handle interpretation and conversation, and write explicit constitutional constraints. Skills codify tribal knowledge into executable documentation for AI agents across their organization.

https://engineering.block.xyz/blog/3-principles-for-designing-agent-skills

#AI
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1360 506
🏗 Encrypting Files with Passkeys and age

A post explaining how to encrypt files with passkeys, using the WebAuthn prf extension and the TypeScript age implementation.

https://words.filippo.io/passkey-encryption

#build
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1359 471
🤖 Manipulating AI memory for profit: The rise of AI Recommendation Poisoning

That helpful “Summarize with AI” button? It might be secretly manipulating what your AI recommends. Microsoft security researchers have discovered a growing trend of AI memory poisoning attacks used for promotional purposes, a technique they called "AI Recommendation Poisoning".

https://www.microsoft.com/en-us/security/blog/2026/02/10/ai-recommendation-poisoning/

#AI
  • ❤ 3
  • 🔥 2
  • 👍 1
Post #1357 452
🔐 Standardizing Privileged Access Architecture for Multi-Cloud

This white paper examines the risks and attack vectors inherent in hybrid multi-cloud infrastructures, and analyzes various attack paths observed by Mandiant in real-world multi-cloud scenarios.

#iam
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1356 514
🤖 Threat modeling agentic AI: a scenario-driven approach

A practical workflow for threat modeling agentic AI systems: use a five-zone navigation lens to trace attack paths, formalize them as attack trees, and map to OWASP's threat taxonomy and playbooks.

https://christian-schneider.net/blog/threat-modeling-agentic-ai/

#AI
  • 👏 3
  • ❤ 1
  • 👍 1
Post #1354 514
🤖 From Automation to Infection: How OpenClaw AI Agent Skills Are Being Weaponized

The fastest-growing personal AI agent ecosystem just became a new delivery channel for malware. Over the last few days, VirusTotal has detected hundreds of OpenClaw skills that are actively malicious.

https://blog.virustotal.com/2026/02/from-automation-to-infection-how.html

#AI
  • ❤ 2
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →