TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1354 · Back to latest

Older Posts 19 shown
Post #1353 429
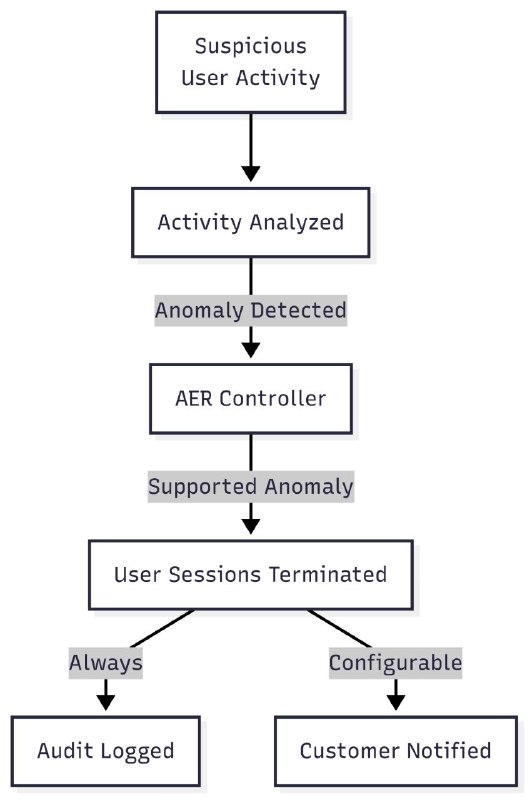
👀 Building Slack’s Anomaly Event Response

This article introduces Slack's Anomaly Event Response (AER), an automated security system that detects suspicious activities and terminates user sessions in real-time, reducing detection-to-response gaps from hours to minutes.

https://slack.engineering/building-slacks-anomaly-event-response/

#monitor
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1348 453
🤖 AI-Assisted Development at Block

Block's AI engineering approach includes: 95% of engineers using AI assistants, providing freedom to explore multiple tools, launching an AI Champions program focused on repo readiness and context engineering, implementing automated PRs, and planning team-based workshops for multi-agent workflows.

https://engineering.block.xyz/blog/ai-assisted-development-at-block

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1347 432
⚙️ Stealing Salesforce OAuth Tokens using the WAF

This post details a method for stealing Salesforce OAuth tokens by exploiting an XSS vulnerability and leveraging the Cloudflare Web Application Firewall (WAF).

https://castilho.sh/salesforce-oauth-ato

#saas
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #1346 437
⚙ We should all be using dependency cooldowns

Dependency cooldowns delay automatic dependency updates, providing a free and effective mitigation against most open source supply chain attacks. Tools like Dependabot and Renovate support configurable cooldown periods before adopting new dependency versions.

https://blog.yossarian.net/2025/11/21/We-should-all-be-using-dependency-cooldowns

(Use VPN to open from Russia)

#cicd
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1344 439
⚙️ Kubernetes Remote Code Execution Via Nodes/Proxy GET Permission

An authorization bypass in Kubernetes RBAC allows for nodes/proxy GET permissions to execute commands in any Pod in the cluster.

https://grahamhelton.com/blog/nodes-proxy-rce

(Use VPN to open from Russia)

#kubernetes
  • 🔥 3
  • ❤ 1
  • 👍 1
Post #1342 567
👩‍💻 A new era of agents, a new era of posture

Microsoft Defender introduces AI Security Posture Management for multi-cloud environments, providing visibility and contextual risk assessment across AI agent architectures. It identifies agents connected to sensitive data, susceptible to indirect prompt injection attacks, and operating as coordinators, while offering attack path analysis and actionable hardening recommendations.

https://www.microsoft.com/en-us/security/blog/2026/01/21/new-era-of-agents-new-era-of-posture/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1341 439
👩‍💻 Linking Privileged Accounts to Identities in Microsoft Defender: Benefits & Use Cases

Microsoft Defender for Identity now allows linking multiple accounts to a single identity, by correlating accounts from different identity providers or linking distinct user accounts, crucial for incident response and remediation.

https://www.cloud-architekt.net/linking-privileged-accounts-in-defender/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1340 446
🔶 CodeBreach: Infiltrating the AWS Console Supply Chain and Hijacking AWS GitHub Repositories via CodeBuild

Wiz Research discovered a critical supply chain vulnerability that abused a CodeBuild misconfiguration to take over key AWS GitHub repositories, including the JavaScript SDK powering the AWS Console.

https://www.wiz.io/blog/wiz-research-codebreach-vulnerability-aws-codebuild

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1338 483
⚙ Kubernetes v1.35: Restricting executables invoked by kubeconfigs via exec plugin allowList added to kuberc

Kubernetes v1.35 introduces beta support for restricting credential plugin executables via kuberc configuration. Users can set "credentialPluginPolicy" to AllowAll, DenyAll, or Allowlist, with an optional "credentialPluginAllowlist" to specify permitted binaries, enhancing security against supply-chain attacks.

https://kubernetes.io/blog/2026/01/09/kubernetes-v1-35-kuberc-credential-plugin-allowlist/

#kubernetes
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1337 493
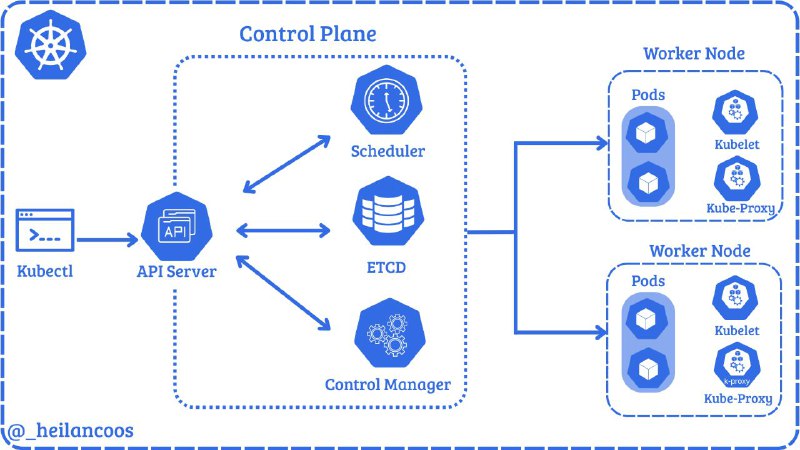
⚙ A Brief Deep-Dive into Attacking and Defending Kubernetes

This article covers Kubernetes attack and defense techniques. Explores Kubernetes components (API Server, ETCD, kubelet), attack vectors including unauthenticated API access, RBAC misconfigurations, ServiceAccount token abuse, malicious admission controllers, CoreDNS poisoning, writable volume mounts, ETCD compromise, and certificate authority exploitation.

https://heilancoos.github.io/research/2025/12/16/kubernetes.html

#kubernetes
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1336 461
🔶 Unauthenticated Cluster Takeover in AWS ROSA

A critical vulnerability in AWS ROSA Classic allowed unauthenticated attackers to discover clusters via Certificate Transparency logs, extract cluster UUIDs and owner emails from unauthenticated endpoints, initiate unauthorized cluster transfers, and escalate to AWS account access through ROSA's IAM roles.

https://blog.ryanjarv.sh/2026/01/05/unauth-aws-rosa-cluster-takeover.html

(Use VPN to open from Russia)

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →