TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1313 · Back to latest

Older Posts 20 shown
Post #1312 390
🔶 Introducing AWS Lambda Managed Instances: Serverless simplicity with EC2 flexibility

Run Lambda functions on EC2 compute while maintaining serverless simplicity—enabling access to specialized hardware and cost optimizations through EC2 pricing models, with AWS handling all infrastructure management.

https://aws.amazon.com/ru/blogs/aws/introducing-aws-lambda-managed-instances-serverless-simplicity-with-ec2-flexibility/

(Use VPN to open from Russia)

#aws
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1310 353
👩‍💻 Backdooring Managed Identities via Azure API Management

Azure API Management exposes managed identity certificates with private keys in plaintext through an undocumented configuration API used by self-hosted gateways. Attackers with gateway keys can extract these certificates for persistent backdoor access.

https://dazesecurity.io/blog/apimMIVuln

(Use VPN to open from Russia)

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1309 472
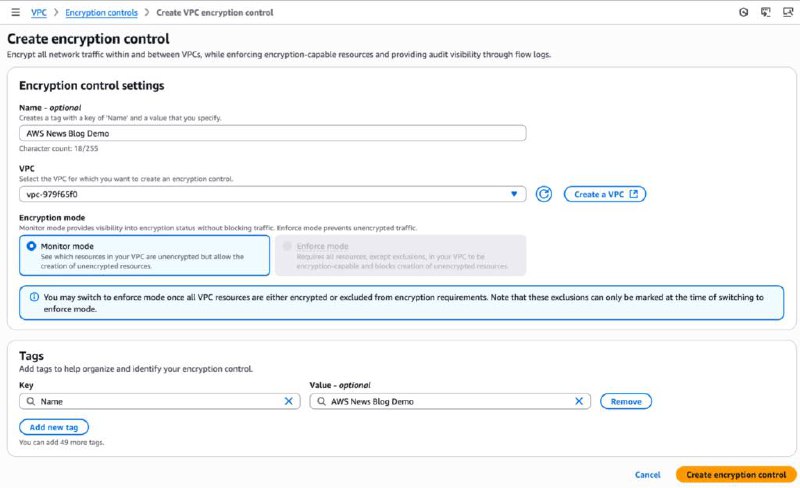
🔶 Introducing VPC encryption controls: Enforce encryption in transit within and across VPCs in a Region

AWS announces VPC encryption controls, a new capability that helps organizations audit and enforce encryption in transit for all traffic within and across VPCs in a Region, simplifying compliance with regulatory frameworks like HIPAA, PCI DSS, and FedRAMP through automated monitoring and enforcement modes.

https://aws.amazon.com/ru/blogs/aws/introducing-vpc-encryption-controls-enforce-encryption-in-transit-within-and-across-vpcs-in-a-region/

(Use VPN to open from Russia)

#aws
  • ❤ 2
  • 👍 2
  • 🔥 1
Post #1305 399
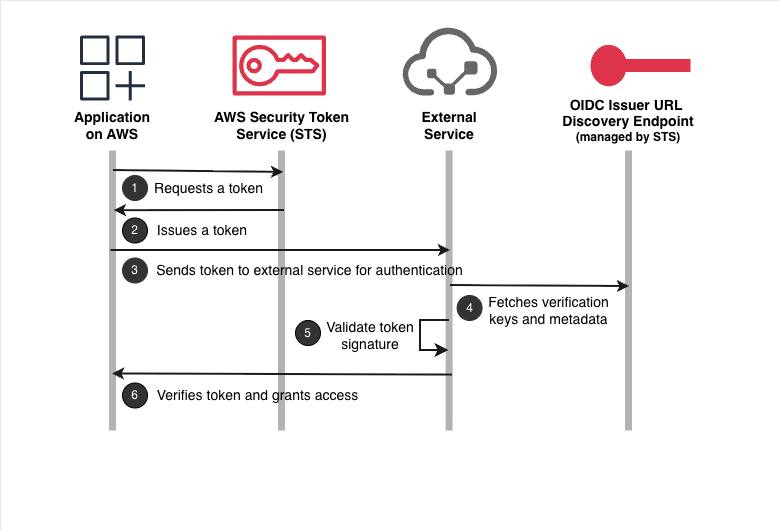
🔶 Simplify access to external services using AWS IAM Outbound Identity Federation

AWS IAM now enables outbound identity federation, allowing developers to securely authenticate AWS workloads with external services using short-lived JSON Web Tokens instead of storing long-term credentials like API keys and passwords.

https://aws.amazon.com/ru/blogs/aws/simplify-access-to-external-services-using-aws-iam-outbound-identity-federation/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1304 404
🔴 Introducing the Emerging Threats Center in Google Security Operations

Google introduces the Emerging Threats Center in Google Security Operations, powered by Gemini AI. It automates detection engineering by ingesting threat intelligence, generating synthetic events, testing coverage, and creating detection rules to help security teams rapidly assess exposure and defensive posture against emerging threats.

https://cloud.google.com/blog/products/identity-security/introducing-the-emerging-threats-center-in-google-security-operations/

#gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1303 351
👩‍💻 Terraform Stacks: A Deep-Dive for Azure Practitioners in Europe

This article explores Terraform Stacks for Azure on HCP Terraform EU. It covers designing stacks with components and deployments, building modules, configuring authentication via OIDC, passing data between stacks, and operational tasks like provisioning and managing stacks at scale.

https://mattias.engineer/blog/2025/terraform-stacks-deep-dive-azure/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1302 365
👩‍💻 Managing Privileged Roles in Microsoft Entra ID

A three-tier model for classifying privileged Microsoft Entra ID roles: Tier 0 (core tenant administration/security), Tier 1 (major service component administration), and Tier 2 (limited-scope/read-only). Each tier has defined security controls, addressing inconsistencies in Microsoft's privileged role documentation.

https://trustedsec.com/blog/managing-privileged-roles-in-microsoft-entra-id-a-pragmatic-approach

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1301 360
🔶 Weaponizing the AWS CLI for Persistence

This article demonstrates weaponizing AWS CLI aliases for stealthy persistence. A one-liner dynamically toggles alias activation to execute malicious payloads while preserving original command functionality, evading detection. The technique exfiltrates credentials post-execution and persists across sessions, useful for red team operations.

https://slayer0x.github.io/awscli/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1300 414
🔴 Private AI Compute: our next step in building private and helpful AI

Google introduces Private AI Compute, a cloud AI processing platform combining Gemini models with on-device-level privacy protections. It uses hardware-secured enclaves, remote attestation, and encryption to ensure personal data remains inaccessible to anyone, including Google, while enabling faster, more capable AI experiences.

https://blog.google/technology/ai/google-private-ai-compute/

#gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1298 384
🔴 Hacking Gemini: A Multi-Layered Approach

The article describes exploiting multi-layered architecture discrepancies in Gemini to bypass Markdown sanitization. The researcher achieved image injection through linkification quirks and context bridges (Gemini-to-Colab), enabling workspace data exfiltration via indirect prompt injection despite existing protections.

https://buganizer.cc/hacking-gemini-a-multi-layered-approach-md

(Use VPN to open from Russia)

#gcp
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #1296 390
🔴 Public Report: Google Private AI Compute Review

NCC Group conducted a 100 person-day security review of Google's Private AI Compute system across two phases, evaluating architecture, cryptography, attestation, IP-blinding relay, T-Log system, and frontend components to ensure cloud-based AI processing maintains local-only privacy guarantees.

https://www.nccgroup.com/research-blog/public-report-google-private-ai-compute-review/

#gcp
  • 👍 2
  • 🔥 2
  • ❤ 1
Post #1295 421
🔶 Introducing AWS Capabilities by Region for easier Regional planning and faster global deployment

AWS Capabilities by Region is a new planning tool that provides detailed visibility into AWS services, features, APIs, and CloudFormation resources across different AWS Regions, helping customers make informed decisions for global deployments and prevent costly rework through side-by-side regional comparisons and forward-looking roadmap information.

https://aws.amazon.com/ru/blogs/aws/introducing-aws-capabilities-by-region-for-easier-regional-planning-and-faster-global-deployments/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 🔥 1
  • 👏 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →