TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1293 · Back to latest

Older Posts 19 shown
Post #1292 407
🔴 How Google Does It: Threat modeling, from basics to AI

Google's threat modeling process follows four key questions: identifying scope, enumerating potential threats using STRIDE methodology and threat libraries, operationalizing mitigations through defensive controls and offensive red team activities, and continuously updating models through review processes and AI-powered automation with Gemini.

https://cloud.google.com/transform/how-google-does-it-threat-modeling-from-basics-to-ai/

#gcp
  • ❤ 3
  • 👍 2
  • 🔥 1
Post #1285 360
🔶 Advancing Our Chef Infrastructure: Safety Without Disruption

Slack's engineering team has enhanced its Chef infrastructure to improve deployment safety and reliability without causing disruption to service owners. Instead of a complex migration to Chef Policyfiles, they focused on practical improvements to their existing EC2 and Chef frameworks.

https://slack.engineering/advancing-our-chef-infrastructure-safety-without-disruption/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1284 374
🔶 Using AWS Secrets Manager Agent with Amazon EKS

AWS Secrets Manager Agent for Amazon EKS provides a language-agnostic HTTP interface that runs locally within containers. It improves application availability by fetching secrets from local cache instead of direct API calls, and implements post-quantum cryptography protection via ML-KEM key exchange.

https://aws.amazon.com/ru/blogs/security/using-aws-secrets-manager-agent-with-amazon-eks/

(Use VPN to open from Russia)

#aws
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1282 372
👩‍💻 Inside the attack chain: Threat activity targeting Azure Blob Storage

Blog outlining some of the unique threats associated with the data storage layer, including relevant stages of the attack chain for Blob Storage to connect these risks to actionable Azure Security controls and applicable security recommendations.

https://www.microsoft.com/en-us/security/blog/2025/10/20/inside-the-attack-chain-threat-activity-targeting-azure-blob-storage/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1281 356
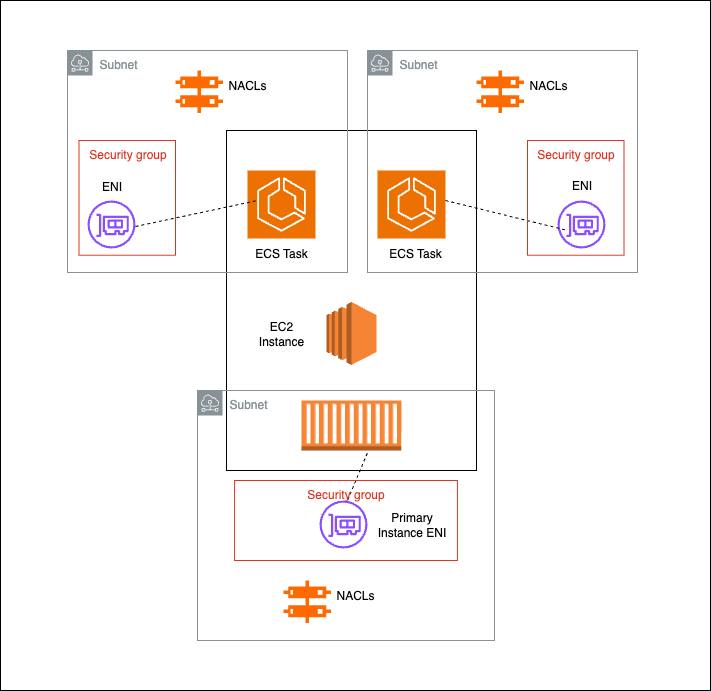
🔶 ECS on EC2: Covering Gaps in IMDS Hardening

The article discusses securing ECS on EC2 by blocking IMDS access. IMDSv2 with hop limit 1 only blocks access in bridge mode but not in awsvpc or host modes. Different networking modes require specific configurations to protect against privilege escalation attacks like ECScape.

https://www.latacora.com/blog/2025/10/02/ecs-on-ec2-covering-gaps-in-imds-hardening/

(Use VPN to open from Russia)

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1276 399
🔶 Introducing Amazon EBS Volume Clones: Create instant copies of your EBS volumes

AWS launched Amazon EBS Volume Clones, a new capability that allows users to create instant point-in-time copies of EBS volumes within the same Availability Zone with a single API call, eliminating the previous multi-step process of taking snapshots and creating volumes from them.

https://aws.amazon.com/ru/blogs/aws/introducing-amazon-ebs-volume-clones-create-instant-copies-of-your-ebs-volumes/

#aws
  • ❤ 3
  • 👍 2
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →