TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1272 · Back to latest

Older Posts 20 shown
Post #1262 428
🔶 How to accelerate security finding reviews using automated business context validation in AWS Security Hub

A structured workflow where security teams define acceptable compensating controls, developers implement them, and an automated system validates their effectiveness.

https://aws.amazon.com/ru/blogs/security/how-to-accelerate-security-finding-reviews-using-automated-business-context-validation-in-aws-security-hub/

(Use VPN to open from Russia)

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1260 388
🔶 IMDS Abused: Hunting Rare Behaviors to Uncover Exploits

This post is about how Wiz used a data-driven methodology to uncover and stop anomalous IMDS usage, and how that approach led them to discover a zero-day vulnerability being exploited in the wild in a popular web service.

https://www.wiz.io/blog/imds-anomaly-hunting-zero-day

#aws
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #1258 403
🔶 Adding Determinism and Safety to Uber IAM Policy Changes

Uber's production environment relies on a complex network of microservices and assets governed by IAM policies. Managing these policies effectively without disrupting production is challenging, as highlighted by an incident where an accidental IAM policy change caused Uber Eats outages. To address this, Uber introduced a Policy Simulator tool that allows policy authors to preview the impact of proposed changes in real time.

https://www.uber.com/en-GB/blog/adding-determinism-and-safety-to-uber-iam-policy-changes/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1256 449
🔶 Multi-Region keys: A new approach to key replication in AWS Payment Cryptography

The new Multi-Region key replication feature in Payment Cryptography enhances automatic key replication capabilities, providing improved resilience and simplified management for global payment applications.

https://aws.amazon.com/ru/blogs/security/multi-region-keys-a-new-approach-to-key-replication-in-aws-payment-cryptography/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1255 412
🔶🔷🔴 Comparing CSP-Managed Machine Identities

This paper compares the threat models of machine identities managed by the CloudService Providers (CSP-managed) across the three major cloud service providers, with a focus on the risks associated with impersonation and usage.

https://cdn.prod.website-files.com/64e50cbe2b6f932c04238c14/68c18f3c1a686fcdf26e81ac_V_WP_Comparing-CSP-Managed-Machine-Identities_090925_FNL%20(1).pdf

#aws #azure #gcp
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1254 385
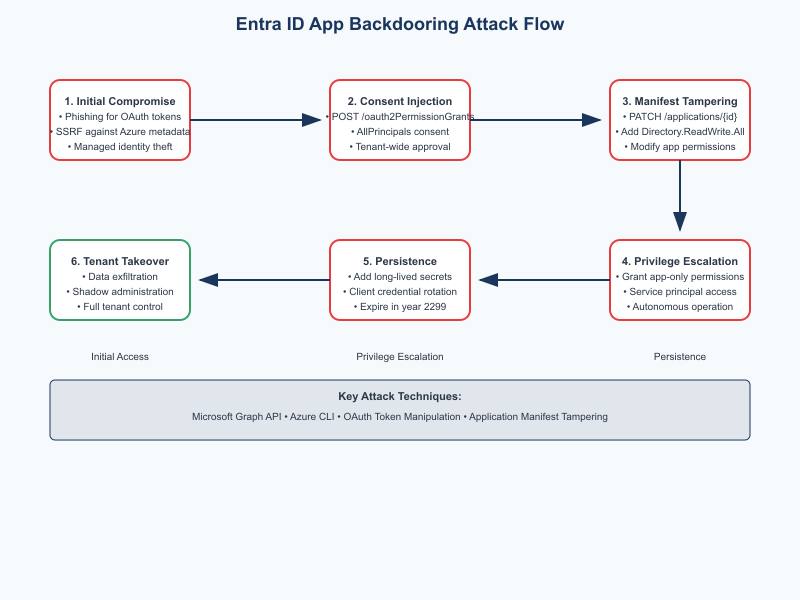
👩‍💻 Illicit Consent-Granting & App Backdooring – Obtaining persistence in Entra

This article details how attackers exploit Entra ID through OAuth consent injection and app backdooring, covering attack flows, MITRE ATT&CK mappings, detection strategies, and prevention methods for securing consent flows.

https://www.slashid.dev/blog/entra-app-backdooring/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1253 391
👩‍💻 One Token to rule them all - obtaining Global Admin in every Entra ID tenant via Actor tokens

This article details a critical vulnerability discovered in Entra ID that allowed full tenant compromise through undocumented Actor tokens and a flaw in Azure AD Graph API's tenant validation. Microsoft patched it under CVE-2025-55241.

https://dirkjanm.io/obtaining-global-admin-in-every-entra-id-tenant-with-actor-tokens/

#azure
  • 👍 2
  • ❤ 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →