TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1252 · Back to latest

Older Posts 20 shown
Post #1251 432
🔶 Overview of security services available in AWS Dedicated Local Zones

Dedicated Local Zones provide a robust solution for running regulated workloads for all industries, to meet strict data residency and digital sovereignty, integrating services like AWS Nitro System, AWS KMS External Key Store, ACM, AWS Shield, Amazon GuardDuty, Amazon Inspector, and AWS CloudTrail.

https://aws.amazon.com/ru/blogs/security/overview-of-security-services-available-in-aws-dedicated-local-zones/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1249 392
👩‍💻 Copilot Broke Your Audit Log, but Microsoft Won’t Tell You

This article reveals a vulnerability in Microsoft 365 Copilot where users could access files without generating audit log entries by simply asking Copilot to omit file links. Microsoft fixed but chose not to disclose this issue.

https://pistachioapp.com/blog/copilot-broke-your-audit-log

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1244 435
👩‍💻 Cloud forensics: Why enabling Microsoft Azure Storage Account logs matters

Although often overlooked, Azure Storage logs can provide invaluable insights for digital forensics, helping investigators reconstruct attacker activity, trace data access patterns, and detect anomalies.

https://techcommunity.microsoft.com/blog/microsoftsecurityexperts/cloud-forensics-why-enabling-microsoft-azure-storage-account-logs-matters/4445723

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1242 406
👩‍💻 Illicit Consent-Granting & App Backdooring – Obtaining persistence in Entra

This article details how attackers exploit Entra ID through OAuth consent injection and app backdooring, covering attack flows, MITRE ATT&CK mappings, detection strategies, and prevention methods for maintaining persistence in Azure environments.

https://www.slashid.com/blog/entra-app-backdooring/

#azure
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1241 393
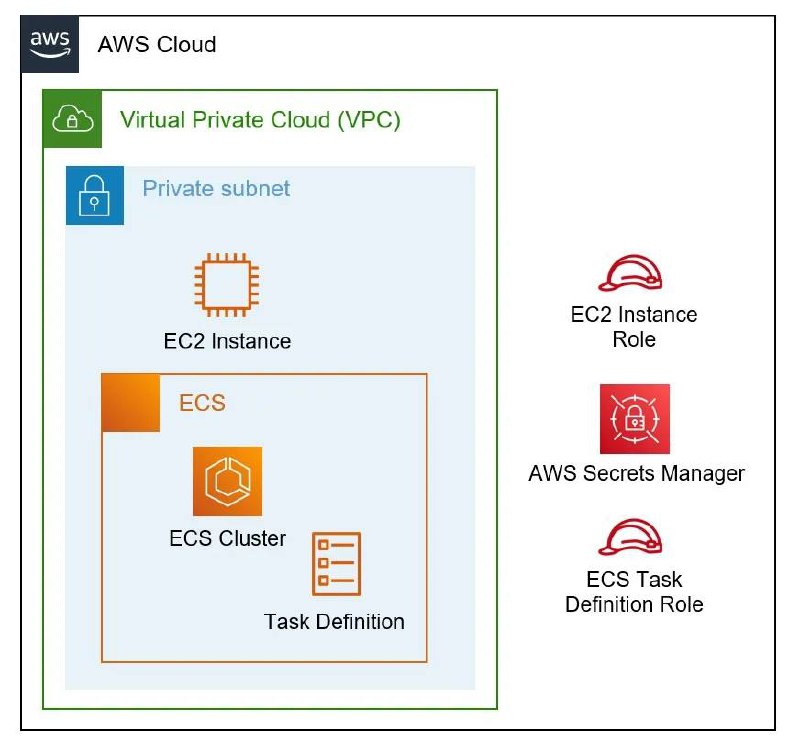
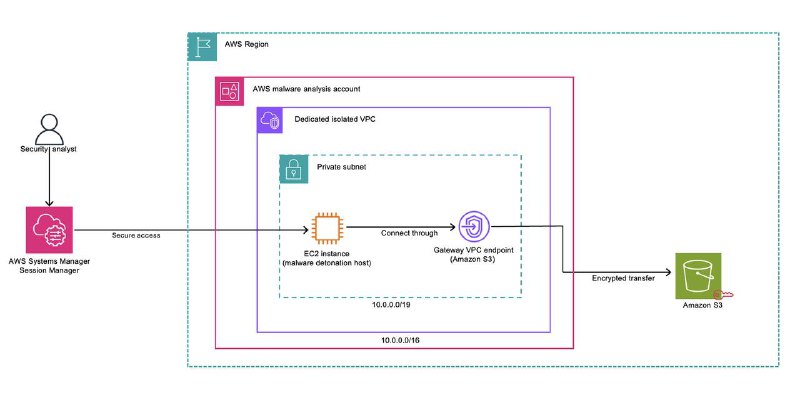
🔶 Sandboxed to Compromised: Credential Exfiltration Paths in AWS Code Interpreters

The article discusses security vulnerabilities in AWS Code Interpreters, particularly focusing on sandboxed environments, and demonstrates that even sandboxed interpreters can access certain AWS services like S3, and their role credentials can be extracted through the Metadata Service.

https://sonraisecurity.com/blog/sandboxed-to-compromised-new-research-exposes-credential-exfiltration-paths-in-aws-code-interpreters/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1240 489
🔶 Simplify multi-tenant encryption with a cost-conscious AWS KMS key strategy

An efficient approach to managing encryption keys in a multi-tenant SaaS environment through centralization, addressing challenges like key proliferation, rising costs, and operational complexity across multiple AWS accounts and services.

https://aws.amazon.com/ru/blogs/architecture/simplify-multi-tenant-encryption-with-a-cost-conscious-aws-kms-key-strategy/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1239 432
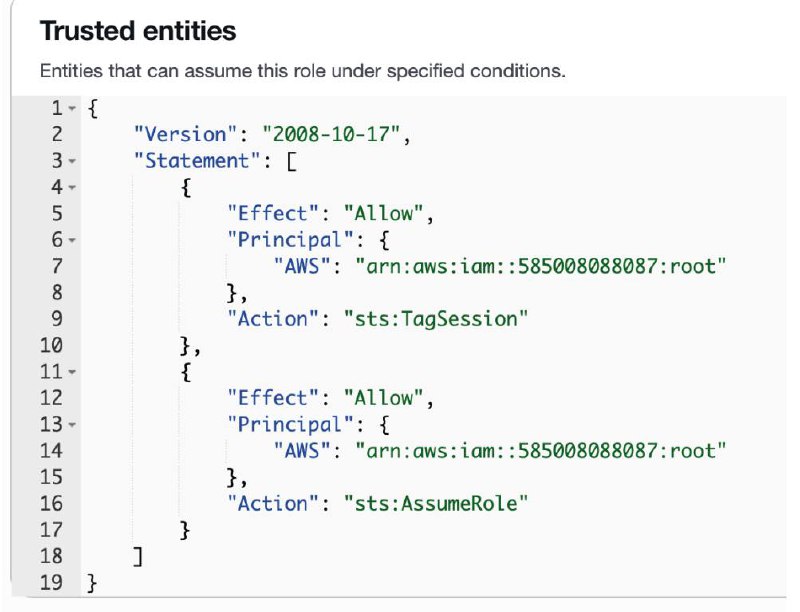
🔶 AWS CDK and SaaS Provider Takeover

This article details a vulnerability where SaaS providers using AWS CDK bootstrap roles could have their accounts taken over through their own platform due to permissive IAM role trust policies lacking external ID protections.

https://blog.ryanjarv.sh/2025/07/21/saas-provider-takeover.html

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1238 422
🔶 A new type of long-lived key on AWS: Bedrock API keys

AWS has introduced a new type of long-lived key called Bedrock API keys, which are used for authenticating applications. These keys are created through the IAM API and can have an expiration time set, but there's no way to enforce this via IAM policy conditions.

https://www.wiz.io/blog/a-new-type-of-long-lived-key-on-aws-bedrock-api-keys

(Use VPN to open from Russia)

#aws
  • ❤ 2
  • 👍 1
  • 🔥 1
Post #1237 434
🔶 AWS CDK and SaaS Provider Takeover

This article details a vulnerability where SaaS providers using AWS CDK bootstrap roles could have their accounts taken over through their own platform due to permissive IAM role trust policies lacking external ID protections.

https://blog.ryanjarv.sh/2025/07/21/saas-provider-takeover.html

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1232 409
🔶 Using AWS Certificate Manager as a covert exfiltration mechanism

This article demonstrates how AWS Certificate Manager can be exploited as a data exfiltration mechanism by storing arbitrary data in X.509 certificates' nsComments extension, allowing up to 2MB per certificate.

https://me.costaskou.com/articles/acmfs/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →