TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.7K
Photos
565
Videos
28
Links
909

Showing posts older than #974 · Back to latest

Older Posts 20 shown
Post #973 2.86K

Forwarded from Кирилл Николаев

  • 👍 5
  • ❤ 2
  • 🔥 2
Post #972 3.28K

Forwarded from Миша

Kerberos UCS.pptx6.5 MB
Всем привет! Сегодня в УрФУ выступил с докладом на тему Kerberos, разобрали некоторые базовые атаки, принцип работы и основные, самые популярные механизмы, которые встречаются при каждом внутреннем пентесте. В докладе старался не погружаться в уж очень страшные дебри, а рассказать все более-менее простым понятным человеческим языком.


Видео:
https://vk.com/video-210214143_456239047

Презентацию прикрепил во вложениях :)

P.S. Само собой, будет продолжение :)
  • 👍 8
  • 🔥 6
  • ❤ 1
Post #969 3.61K

Forwarded from Ralf Hacker Channel (Ralf Hacker)

Если кто-то не совсем разобрался с техникой DLL Hijacking, или может совсем не в курсе, что это такое, советую данный материал. Очень хорошая работа!

https://elliotonsecurity.com/perfect-dll-hijacking/

So today, we're doing 100% original research reverse engineering the Windows library loader to not just cleanly workaround Loader Lock but, in the end, disable it outright. Plus, coming up with some stable mitigation & detection mechanisms defenders can use to help guard against DLL hijacking.

#maldev #redteam
Elliot on Security Elliot on Security - Perfect DLL Hijacking Disengaging Loader Lock to do anything directly from DLLMain...
  • 🔥 11
Post #968 4.27K

Forwarded from SecuriXy.kz

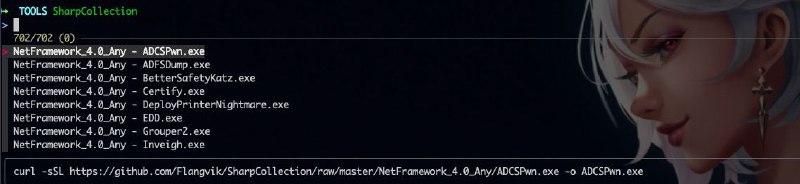
Для автоматизации загрузки скомпиленных бинарей, к примеру из репозитория #SharpCollection можете добавить альяс в свой .zshrc и использовать его подручно. Удобно, быстро и хорошо...

SharpCollection() {curl -sSL 'https://api.github.com/repos/Flangvik/SharpCollection/git/trees/master?recursive=1' | jq -r '.tree[] | select(.path | endswith(".exe")) | .path | split("/") | "\(.[0]) - \(.[1])"' | fzf -m --reverse --height=50% --preview-window=down:5% -d" - " --preview 'echo "curl -sSL https://github.com/Flangvik/SharpCollection/raw/master/"{1}"/"{2}" -o "{2}""' | awk -F' - ' '{print $1,$2}' | while read -r arch filename; do echo; wget https://github.com/Flangvik/SharpCollection/raw/master/$arch/$filename -O $filename; done}

Спасибо Паше за подсказку
  • 🔥 8
  • 👍 2
  • ❤‍🔥 1
  • ❤ 1
Post #967 6.37K
⚡PsMapExec

A PowerShell tool that takes strong inspiration from CrackMapExec.

🚀 Supported Methods

— PsExec
— RDP
— SMB Signing
— WinRM
— WMI

🔗 More Detailed
🔗 Github Repository

#ad #windows #powershell #cme
  • 🔥 18
  • 👍 4
  • ❤ 2
Post #966 24.4K
🔐 Crack.sh is dead, Long Live Shuck.sh

Recently, many of you might've noticed that Crack.sh is currently unavailable. While it's been an invaluable tool in our arsenal, the landscape is ever-changing, and we need to pivot. Meet Shuck.sh, an emerging service that offers similar capabilities, leveraging the extensive Have I Been Pwned (HIBP) database.

🚀 Key Features:

— Shuck It: Instantly shuck NetNTLMv1, PPTP VPN, and WPA-Enterprise MSCHAPv2 challenges against HIBP's NT-hash database.
— Tech Insight: Efficient binary search for DES-keys collisions from a subset of the HIBP database.
— Fast & Free: Got around 100 NetNTLMv1 challenges? Extract their corresponding NT-Hashes in roughly 10 seconds.

One significant advantage of Shuck.sh over other tools is its ability to be deployed locally. For those concerned about security and privacy, you can set up Shuck.sh on your own environment using its script from the GitHub repository.

🔗 Shuck.sh
🔗 GitHub Repository
🔗 Pwned Passwords Version 8 (Torrent)

#ntlmv1 #des #mschapv2 #bruteforce
  • 🔥 6
  • 👍 4
Post #964 4.38K
🍀 MSIFortune - Local Privilege Escalation with MSI Installers

MSI installers are still pretty alive today. It is a lesser known feature, that a low privileged user can start the repair function of an installation which will run with SYSTEM privileges. What could go wrong? Quite a lot!

The repair function often triggers CustomActions, which can lead to several potential issues:

— Visible conhost.exe via a cmd.exe or other console binaries
— Visible PowerShell
— Directly actions from the installer with SYSTEM privileges
— Executing binaries from user writable paths
— DLL sideloading / search path abusing
— Missing PowerShell parameters, mostly -NoProfile
— Execution of other tools in an unsafe manner

🌐 Details:
https://badoption.eu/blog/2023/10/03/MSIFortune.html

#windows #msi #lpe
  • 🔥 9
  • ❤ 1
  • 👍 1
Post #963 3.44K
Post #962 3.37K

Forwarded from 1N73LL1G3NC3

NetExec

This tool is based on CrackMapExec and was originally created by bytebleeder and maintained by mpgn over the years, shout out to them! With the retirement of mpgn, we decided to maintain the tool NetExec, formerly known as CrackMapExec, as a completely free open source tool.

Today will be our first release of NetExec version 1.0.0

NetExec wiki
  • 👍 8
  • 🔥 4
Post #961 20.7K
🔒 Protected Users and xfreerdp

By default xfreerdp does not support Kerberos authentication. As such you'll have to recompile it specifying the WITH_GSSAPI option. Also you'll need the libkrb5-dev package to handle TGT/ST requests :)

#ad #kerberos #xfreerdp #redteam
  • 🔥 6
Post #960 4.31K
➡️ Local Admin to Domain Admin

Ask a TGS on behalf of another user without password.

Scenario: you are Local Administrator and there is a logged User you want to Impersonate!

🌐 Source:
https://github.com/foxlox/GIUDA

#ad #kerberos #tgs #perl
  • 👍 7
Post #955 4.79K
😈 POSTDump

This is the C# / .NET implementation of the ReactOS minidump function (like nanodump), thus avoiding call to the Windows API MiniDumpWriteDump function.

🚀 Key Features:

— Usage of indirect syscall along with halo's gate technic to retrieve syscalls IDs
— No memory Allocation/Protection call is performed for indirect syscall, instead, free RWX codecave found in the current process are used
— ETW patching
— No call to MiniDumpWriteDump

🌐 Source:
https://github.com/YOLOP0wn/POSTDump

#windows #lsass #dump #syscall #reactos
  • 🔥 7
  • 👍 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →