Если кто-то не совсем разобрался с техникой DLL Hijacking, или может совсем не в курсе, что это такое, советую данный материал. Очень хорошая работа!
https://elliotonsecurity.com/perfect-dll-hijacking/
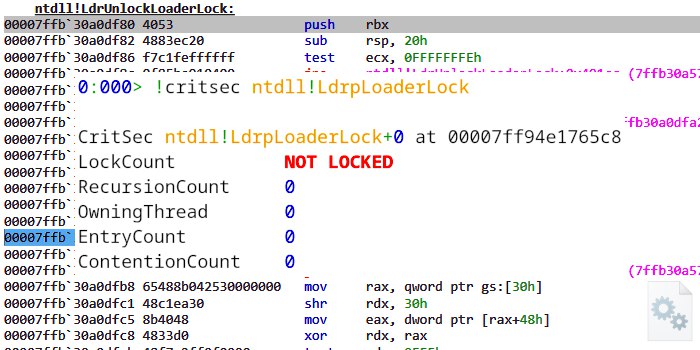
So today, we're doing 100% original research reverse engineering the Windows library loader to not just cleanly workaround Loader Lock but, in the end, disable it outright. Plus, coming up with some stable mitigation & detection mechanisms defenders can use to help guard against DLL hijacking.
#maldev #redteam
Post #969
3.61K