Some useful stuff
So called discussion group: https://t.me/zzzstuffchat
Post #214
240
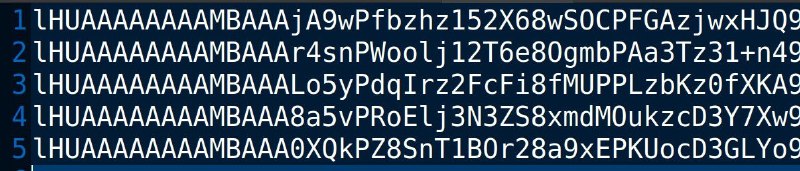
Disclaimer: It's not meant for extracting keybox as of now. If you still dump secure region you might get the leaf certificates in plain text as mentioned in the screenshot but you won't get the EC private key in plain text. Try injecting a custom SVC into the functions that handle heavy math. You'll see some complex multiplication and addition continuously. If your device is older enough your TEE binary will have (armv7 and armv8) mixed codes and TAs loaded from vendor partition are also armv7. So patch accordingly. I can't say anything beyond this. Use it at your own risk.
https://github.com/antagonizzzt/thalaivan
For those curious people. Here's the updated tool. You can start experimenting with this. Open the rmx2156 board file and include file to begin with. I've commented out how things work. I'm releasing this now. Becuz I won't be available for some days.
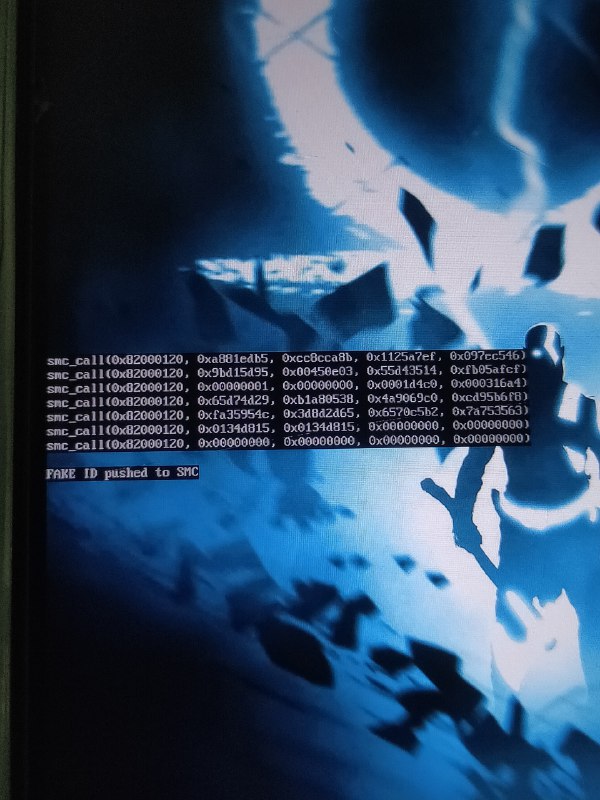
Also note that, ATF doesn't have a storage driver. So you have to rely on kaeru. Implement this into kaeru. Just call dump_call_smc(). A keypress or a custom fastboot command will do the job.
That's all for now
GitHub GitHub - antagonizzzt/thalaivan: A MediaTek ATF/TEE payload injector enabling arbitrary code execution at EL3 on vulnerable devices. A MediaTek ATF/TEE payload injector enabling arbitrary code execution at EL3 on vulnerable devices. - antagonizzzt/thalaivan https://github.com/antagonizzzt/thalaivan
For those curious people. Here's the updated tool. You can start experimenting with this. Open the rmx2156 board file and include file to begin with. I've commented out how things work. I'm releasing this now. Becuz I won't be available for some days.
Also note that, ATF doesn't have a storage driver. So you have to rely on kaeru. Implement this into kaeru. Just call dump_call_smc(). A keypress or a custom fastboot command will do the job.
That's all for now
- 🔥 3