


SQL injections in REST APIs and CMS cores, unverified digital signatures handing over full account takeovers, and
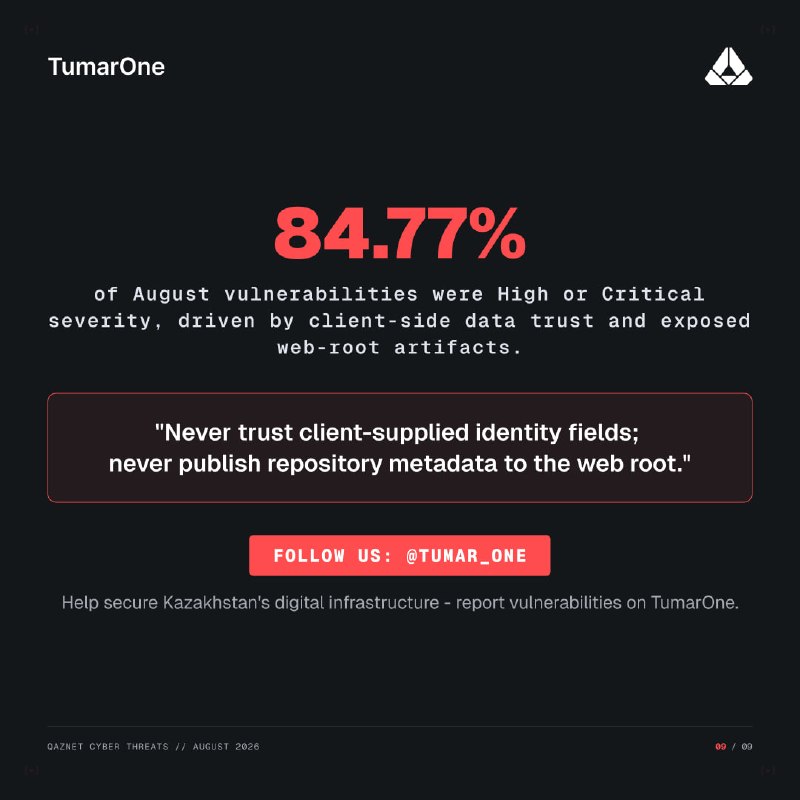
.git repositories left wide open in web roots. Nearly 85% of critical findings this month boiled down to two simple mistakes: trusting client-supplied input and leaving exposed metadata in the web root.Full breakdown - in the cards above. 👆
Stay ahead with tumar.one 😃