
The vulnerabilities in June and July weren't clever...
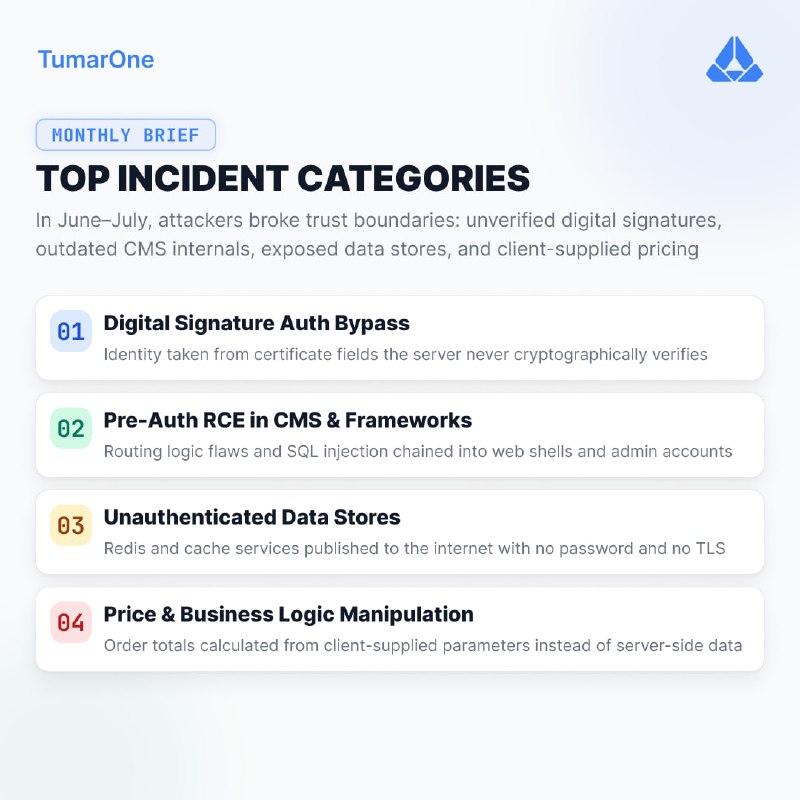
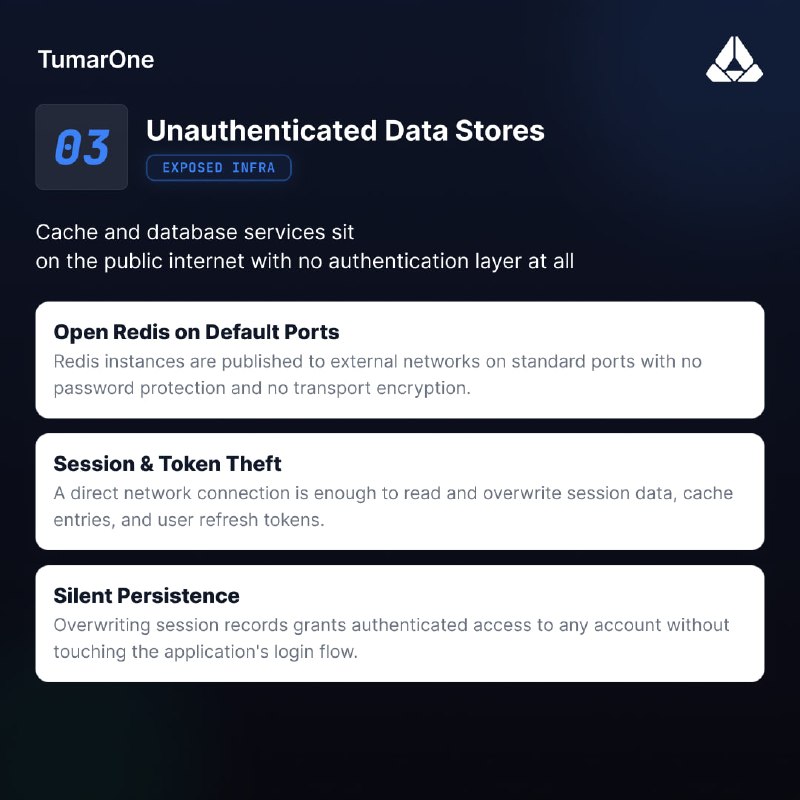
Because they didn't need to be. Unverified signatures, client-supplied prices, open Redis instances, outdated CMS handing out root shells. 89% of critical findings this cycle came from systems that simply trusted the wrong input.
This digest covers June and July combined. Full breakdown - categories, hunter checklist, developer checklist - in the cards above. 👆
Stay tuned tumar.one 😃
Post #78
257





- ❤ 5
- 👏 2
- 🙊 1