TGViewer
TumarOne platform (official channel) TumarOne platform (official channel) @tumar_one · 266 subscribers
Post #46 675
One day, vibe coders will learn not to push .env files. Until then - we'll keep the stats coming.

Over the past month, we analyzed a large number of reports from the Kazakhstan internet segment and spotted some clear trends we'll now be sharing regularly. And, oh boy, the majority of critical issues come not from sophisticated cyberattacks, but from basic negligence during development and server configuration.

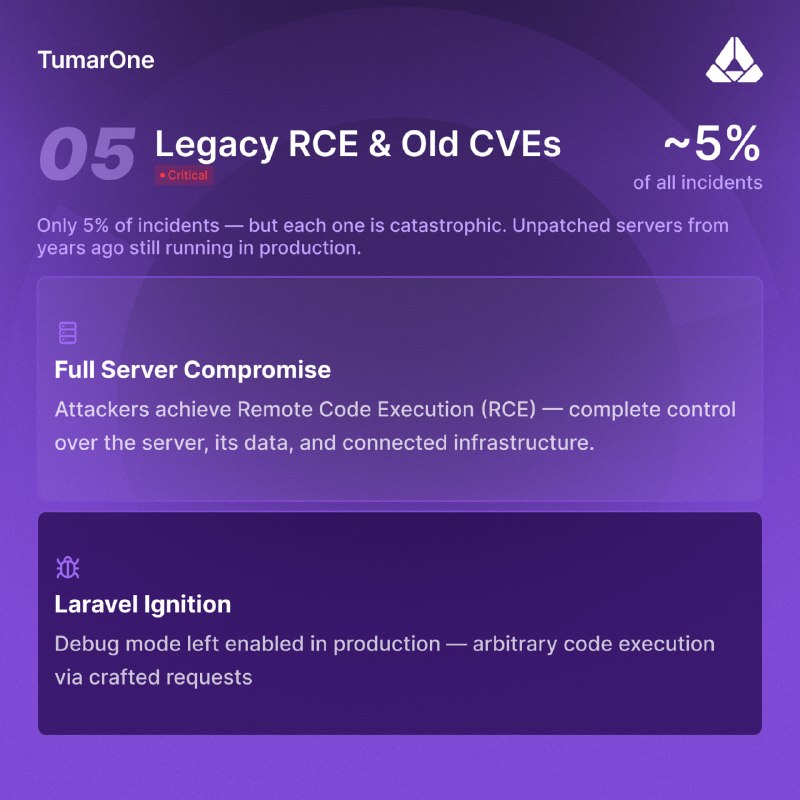
The full breakdown — top vulnerability categories, examples, and a developer checklist — is in the cards above. 👆

Remember, cyber hygiene is not a one-time campaign, but a continuous process.
Stay safe and stay tuned with tumar.one.
  • ❤‍🔥 5
  • 👍 4
  • 🎉 2
  • 🔥 1
  • 👏 1
More from @tumar_one
  1. Sep 11, 2026Limited time only! 🔥 Kcell Doubles Bug Bounty Rewards for Critical Vulnerabilities: Up to…
  2. Sep 9, 2026📋 New on Tumar.One: Report Limits We are rolling out report submission limits across the…
  3. Sep 8, 2026Hey researcher 👋 We'd like to invite you to KazHackStan - the biggest hacker conference i…
  4. Sep 7, 2026KazHackStan 2026 Executive Sponsor - Tumar.One 🔥 Tumar.One - Орталық Азиядағы 4 000-нан а…
  5. Aug 13, 2026The vulnerabilities in June and July weren't clever... Because they didn't need to be. Unv…
  6. Jul 21, 2026Important Rules Update We have updated the Tumar.One platform rules - and there are quite…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →