ThreatStrix pinned «🚀 نسخه جدید Dumplyzer (v0.1.1) منتشر شد. 🎯 در این نسخه: - بهبود Domain IOC Detection با استفاده از Public Suffix List و در نظر گرفتن Context - امکان انتخاب YARA Rules بهصورت Rule تکی، Category یا Custom Rules - اضافه شدن CSV Export در بخش Reports و IOCs…»
Channel Public Channel
 TH
- Subscribers
- 3.22K
- Photos
- 7
- Videos
- 1
- Links
- 30
Recent Posts 17 shown
Post #356
4.45K
🚀 نسخه جدید Dumplyzer (v0.1.1) منتشر شد.
🎯 در این نسخه:
- بهبود Domain IOC Detection با استفاده از Public Suffix List و در نظر گرفتن Context
- امکان انتخاب YARA Rules بهصورت Rule تکی، Category یا Custom Rules
- اضافه شدن CSV Export در بخش Reports و IOCs
- اضافه شدن Incremental Loading
- نمایش PID در بخش Jobs هنگام Process Deep Dive
- بهبود نمایش Processهای Deep Dive شده
- بهبود محاسبه Job Progress
- افزایش تعداد YARA Rulesها به 56 مورد
- رفع مشکل اضافه کردن Custom YARA Rules
- رفع مشکلات Export در بخش IOCs
- بهبود فرایند Upgrade / Uninstall و رفع مشکلات Installer
📦 فایل Installer ویندوزی رو میتونید از Repository زیر دانلود کنید و یا در صورت نیاز، پروژه رو از سورس Build کنید.
🔗 GitHub:
https://github.com/EmadAbedini/Dumplyzer
- ❤ 31
- 💯 2
- 🤩 1
- 😍 1
- 🫡 1
Post #355
2.58K
🚀 Dumplyzer v0.1.1 is now available!
🎯 What’s new in this release:
- Improved Domain IOC Detection using the Public Suffix List and contextual analysis
- YARA Rule selection by individual rule, category, or custom rules
- Added CSV export for Reports and IOCs
- Added Incremental Loading
- PID display in Jobs during Process Deep Dive
- Improved visualization of Deep Dive processes
- Improved Job Progress calculation
- Increased the number of built-in YARA rules to 56
- Fixed issues with adding Custom YARA Rules
- Fixed IOC export issues
- Improved Upgrade / Uninstall workflows and fixed Installer issues
📦 The Windows installer is available from the repository below. You can also build Dumplyzer from source if needed.
🔗 GitHub:
https://github.com/EmadAbedini/Dumplyzer
- ❤ 5
- 😍 2
- 🔥 1
- 👌 1
Post #348
2.42K


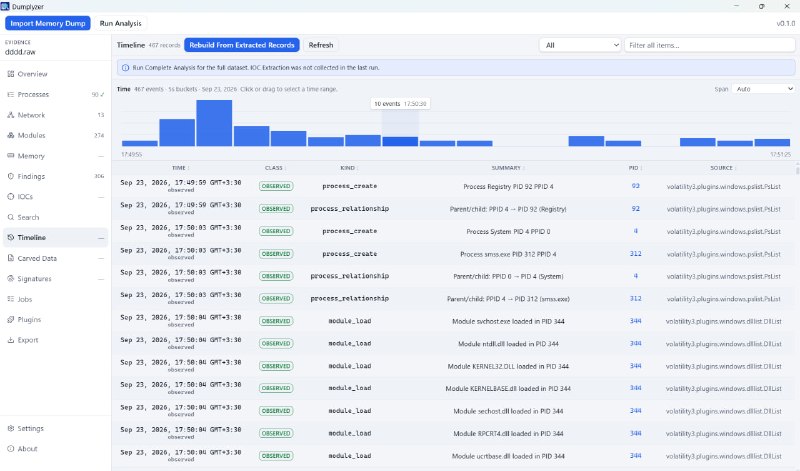

Dumplyzer v0.1.0
- ❤ 38
- 🤯 12
- 👍 1
- 🙏 1
- 👌 1
Post #347
7.05K
🧠 ابزار Dumplyzer | پلتفرم تحلیل Memory Dump
با Dumplyzer بدون درگیر شدن با ابزارهای مختلف، میتونید خیلی راحت و سریع فایلهای Memory Dump رو به صورت GUI تحلیل کنید.
🎯 بخشی از قابلیتها:
- استخراج دیتای Processها، Command Line، Module/DLL، Handle و Process Tree
- بررسی جزئیات یک Process بر اساس PID، شامل Parent/Child، Module، Network، Handle و Memory Region
- استخراج IOC شامل IP، Domain، URL، Mutex، Registry، Path و Hash
- استخراج و بررسی Network Connectionها و Network Artifactها
- امکان بازسازی PCAP
- ایجاد Timeline از Artifactهای استخراج شده و فیلتر بر اساس بازه زمانی
- امکان Index گذاری و جستوجوی سریع در Artifactهای استخراجی
- امکان بازسازی فایلهای PE
- سه حالت تحلیل Quick Triage، Complete Analysis و Custom
- امکان YARA Scan، به همراه امکان اضافه کردن Ruleهای سفارشی
- بررسی Capability فایلهای PE بازسازی شده
- استخراج Artifactهای قابل Carving شامل Email، Phone، MAC Address، HTTP Log، AES Key و موارد مشابه
- شناسایی و Deobfuscation خودکار Stringها
- اجرای Pluginهای Volatility به شکل بسیار ساده
- امکان Correlation بین Artifactها
- ایجاد گزارش در فرمتهای HTML، JSON و Excel
- کاملا Offline و Local
📦 فایل Installer ویندوزی رو میتونید از Repository زیر دانلود کنید یا در صورت نیاز، پروژه رو از سورس Build کنید.
🔗 GitHub:
https://github.com/EmadAbedini/Dumplyzer
اگه در زمینه DFIR، Threat Hunting، Malware Analysis و در کل Memory Forensics کار میکنید، این ابزار میتونه فرایند تحلیل Memory Dump رو تا حد زیادی سریعتر و سادهتر کنه.
امیدوارم مفید باشه ❤️
- 🔥 33
- ❤ 11
- 👍 3
- 🙏 1
- 😍 1
Post #346
2.17K
🧠 Dumplyzer | Memory Dump Analysis Platform
With Dumplyzer, you can analyze Memory Dump files quickly and easily through a GUI, without having to work with multiple separate tools.
🎯 Some of its key features include:
- Extract Process data, Command Lines, Modules/DLLs, Handles, and Process Trees
- Investigate detailed Process information by PID, including Parent/Child processes, Modules, Network connections, Handles, and Memory Regions
- Extract IOCs including IPs, Domains, URLs, Mutexes, Registry Keys, Paths, and Hashes
- Extract and investigate Network Connections and Network Artifacts
- Reconstruct PCAP files
- Create Timelines from extracted Artifacts and filter them by time range
- Index and quickly search through extracted Artifacts
- Reconstruct PE files
- Three analysis modes: Quick Triage, Complete Analysis, and Custom
- YARA scanning with support for custom Rules
- Analyze the capabilities of reconstructed PE files
- Carve Artifacts including Emails, Phone Numbers, MAC Addresses, HTTP Logs, AES Keys, and similar data
- Automatically identify and deobfuscate Strings
- Run Volatility Plugins with a simple and intuitive interface
- Correlate extracted Artifacts
- Generate reports in HTML, JSON, and Excel formats
- Fully Offline and Local
📦 The Windows Installer is available through the repository below, and you can also build the project from source if needed.
🔗 GitHub:
https://github.com/EmadAbedini/Dumplyzer
If you work in DFIR, Threat Hunting, Malware Analysis, or Memory Forensics, Dumplyzer can help make the Memory Dump analysis process significantly faster and easier.
Hope you find it useful ❤️
- ❤ 6
- 😱 3
- 😍 2
- 👍 1
Post #344
1.25K
ESXi_VMFS_Wiper.yar958 B
سلام و درود 🙋♂️
چند وقت پیش سر یک Incident، روی ESXi با Malwareی مواجه شدیم که:
1- کل VMهای Running رو Kill میکرد.
2- دیتا استورها رو بررسی میکرد تا یه دید کلی از VMها و Dataشون پیدا کنه.
3- از دیتای مرحله قبل استفاده میکرد و به صورت Random بین VMها، هر بار بخشی از Dataشون رو با 0x00 جایگزین (Overwrite) میکرد و این فرایند تا تکمیل Wipe ادامه داشت.
4- در نهایت Host رو Reboot میکرد. (با هدف از بین بردن Data موجود در Memory)
⚠️ از اونجایی که همین Wiper، در چند سازمان مختلف دیگه هم دیده شده، پیشنهاد میکنم همین الان ESXiتون رو با این Rule اسکن کنید.
▪️ اگه امکان اجرای YARA Engine روی خود ESXi براتون زمانبره، میتونید همین Rule رو به صورت یک اسکریپت Pythonی آماده و اجرا کنید. (معمولا ESXi بهصورت پیشفرض Python رو نصب داره)
▪️ اگه نگران Impact روی VMهای Running هستین، مسیر /vmfs/volumes/ رو اسکن نکنید.
چند وقت پیش سر یک Incident، روی ESXi با Malwareی مواجه شدیم که:
1- کل VMهای Running رو Kill میکرد.
2- دیتا استورها رو بررسی میکرد تا یه دید کلی از VMها و Dataشون پیدا کنه.
3- از دیتای مرحله قبل استفاده میکرد و به صورت Random بین VMها، هر بار بخشی از Dataشون رو با 0x00 جایگزین (Overwrite) میکرد و این فرایند تا تکمیل Wipe ادامه داشت.
4- در نهایت Host رو Reboot میکرد. (با هدف از بین بردن Data موجود در Memory)
چرا Random؟
که حتی اگه Processش در طول فرایند Wipe شناسایی و Kill شد، برگردوندن VMها حداقل با روشهای عادی امکانپذیر نباشه و بنابراین بیشترین حجم تخریب ممکن ایجاد بشه.
⚠️ از اونجایی که همین Wiper، در چند سازمان مختلف دیگه هم دیده شده، پیشنهاد میکنم همین الان ESXiتون رو با این Rule اسکن کنید.
▪️ اگه امکان اجرای YARA Engine روی خود ESXi براتون زمانبره، میتونید همین Rule رو به صورت یک اسکریپت Pythonی آماده و اجرا کنید. (معمولا ESXi بهصورت پیشفرض Python رو نصب داره)
▪️ اگه نگران Impact روی VMهای Running هستین، مسیر /vmfs/volumes/ رو اسکن نکنید.
- ❤ 23
- 👍 3
- 👏 3
- 🫡 1
Post #342
2.76K
Forwarded from رادیو زیرو پاد
قسمت دوازدهم زیرو تاک | رادیو زیرو پادHossein Naeiji | @RadioZeroPd - @TryHackBox⭕️ قسمت دوازدهم رادیو زیرو تاک
📌 موضوع جلسه :
آشنایی با DFIR
🎙 مهمان برنامه : مهندس عماد عابدینی
منتظر جلسه بعدی باشید.
🎤 راهبر گفتگوی امنیتی : حسین نائیجی
🆔 @RadioZeroPod
🆔 @TryHackBox
🆔 @TryHackBoxOfficial
🆔 @AiTHB
📌 موضوع جلسه :
آشنایی با DFIR
🎙 مهمان برنامه : مهندس عماد عابدینی
منتظر جلسه بعدی باشید.
🎤 راهبر گفتگوی امنیتی : حسین نائیجی
🆔 @RadioZeroPod
🆔 @TryHackBox
🆔 @TryHackBoxOfficial
🆔 @AiTHB
- 🔥 16
- ❤ 3
- 🤩 1
- 👌 1
- 😍 1
Post #340
3.46K
Forwarded from رادیو زیرو پاد

📌 برگزاری جلسه ویس چت :
با درود خدمت دوستان و همراهان عزیز،
در راستای ارتقای سطح دانش فنی و آشنایی بیشتر با مباحث امنیت سایبری، قصد داریم جلسهای تخصصی و آموزشی در خصوص زمینه DFIR به صورت ویس چت برگزار کنیم.
🎙 مهمان ویژه:
👤 مهندس : عماد عابدینی
📅 زمان برگزاری: دوشنبه 1405/05/26
📍 پلتفرم: ویس چت تلگرام
🕗 ساعت : 20:00
🔖 لینک جلسه :
⁉️ موضوعات ما :
◾️بخش اول: آشنایی با DFIR
🔔 نکته مهم:
جهت شرکت به موقع جلسه، حتماً کانال تلگرام را چک کنید تا از این جلسه جا نمونید .
➖➖➖➖➖➖➖➖➖➖➖➖➖➖
🆔 @RadioZeroPod
🆔 @TryHackBox
- ❤ 11
- 🎉 4
- 💯 4
- 😍 2
- 🔥 1
Post #338
4.09K

💎 چرا نباید به نتیجه Sandbox اعتماد کنیم؟
اگه سازمان شما از Sandbox استفاده میکنه و روی نتایج تحلیلش حساب باز میکنین، این پست رو بهتون پیشنهاد میکنم.
توی این پست ویرگول میخوایم ببینیم چرا حتی گرونترین و پیشرفتهترین Sandboxها هم وقتی یک فایل رو Clean اعلام میکنن، نمیتونیم این نتیجه رو قطعی در نظر بگیریم.
بررسی میکنیم Malwareها چطور میتونن با تشخیص محیط تحلیل، رفتار اصلی خودشون رو مخفی کنن.
📌 روشهای رایج Sandbox Detection و Evasion رو بررسی میکنیم و میریم سراغ مواردی مثل:
ـ Hypervisor/VM Detection
ـ Monitoring Tools و Human Interaction
ـ Network Environment
ـ Analysis Tools Detection
ـ CPU Instructions و Virtualization Artifacts
ـ روشهای نزدیک کردن Sandbox به محیط واقعی سازمان
🎯 در نهایت هم درباره مدل Risk-Based Scoring و ترکیب نتایج چند لایه تحلیل برای تصمیمگیری درباره فایلها صحبت میکنیم.
🔗 ویرگول:
https://vrgl.ir/kTVUx
امیدوارم مفید باشه ❤️
- ❤ 10
- 💯 6
- 🤩 4
- 🎉 2
- 👌 1
Post #337
3.31K
💎 Why You Shouldn’t Trust Sandbox Results?
If your organization uses a Sandbox and relies on its analysis results, I recommend checking out this post.
In this Medium post, we’ll look at why even the most expensive and advanced Sandboxes can’t be considered a definitive source of truth when they classify a file as Clean.
We’ll also look at how Malware can detect an analysis environment and hide its actual behavior.
📌 We’ll cover common Sandbox Detection and Evasion techniques, including:
- Hypervisor/VM Detection
- Monitoring Tools and Human Interaction
- Network Environment
- Analysis Tools Detection
- CPU Instructions and Virtualization Artifacts
- Techniques for making a Sandbox more similar to an organization’s real environment
🎯 Finally, we’ll discuss Risk-Based Scoring and how combining results from multiple analysis layers can help with file-related decision-making.
🔗 Medium:
https://emad-abedini.medium.com/why-you-shouldnt-trust-sandbox-results-d1b8159da26d?sharedUserId=emad-abedini
I hope you find it useful ❤️
- 💯 10
- ❤ 5
- 🤩 2
- 👍 1
- 🎉 1
Post #335
8.74K
Docker_From_Fundamentals_to_Production_Security.pdf2.6 MB
- 👏 7
- 👍 4
- 🤩 4
- ❤ 3
- 👌 1
Post #334
3.95K
- 👍 10
- 👏 4
- 😍 3
- 🙏 1
- 👌 1
Post #331
8.92K
📘 کتاب Docker: From Fundamentals to Production Security
این کتاب در 109 صفحه، مهمترین مفاهیم و نکاتی رو که برای استفاده اصولی از Docker نیاز هست رو پوشش میده.
از معماری و نحوه ارتباط بین اجزا گرفته تا Security و نکاتی که در محیط Production واقعا به کار میان.
این کتاب، جمعبندی من از چندین منبع، یک دوره آموزشی و مستندات رسمی Docker هست؛ با این هدف که مطالب رو به زبان سادهتر، خلاصهتر و کاربردیتر کنار هم بیارم.
قطعا این کتاب جایگزین مستندات رسمی یا منابع تخصصی نیست، اما میتونه نقطه شروع یا مرجع مناسبی برای یادگیری و مرور Docker باشه.
امیدوارم مفید باشه ❤️
- 👍 7
- ❤ 5
- 👏 4
- 🎉 4
Post #330
2.68K
📘 Docker: From Fundamentals to Production Security
This book covers the most important Docker concepts and topics required for using Docker properly, in 109 pages.
From architecture and how different components interact with each other to security and the key points that are actually needed in Production environments.
This book is a summary of my learnings from multiple resources, a training course, and the official Docker documentation. My goal was to bring these topics together in a simpler, more concise, and practical way.
This book is not intended to replace the official documentation or specialized resources, but it can be a good starting point or a useful reference for learning and reviewing Docker.
I hope it will be useful ❤️
- 👍 7
ThreatStrix pinned «🎥 روش تحلیل بدافزارهای Obfuscate شدهی Golang در فرایند تحلیل بدافزارها، نمونههایی که با Go (Golang) نوشته میشن معمولا نسبت به زبانهایی مثل C تحلیل پیچیدهتری دارن، بهخصوص زمانی که بدافزار Obfuscate هم شده باشه. در این ویدیو، روش تحلیل این دسته از بدافزارها…»
Post #328
11.4K

- ❤ 26
- 👏 2
- 🔥 1
About this channel
- How can I read @threatstrix without a Telegram account?
- TGViewer shows the public web preview Telegram publishes for ThreatStrix: recent posts, photos, videos and the subscriber count, with no app, login or account.
- How many subscribers does ThreatStrix have?
- ThreatStrix (@threatstrix) has 3.22K subscribers on Telegram, refreshed roughly every 30 minutes.
- Does ThreatStrix know I viewed it here?
- No. Public channel previews carry no viewer identity, and TGViewer has no accounts or tracking of what you look up.