
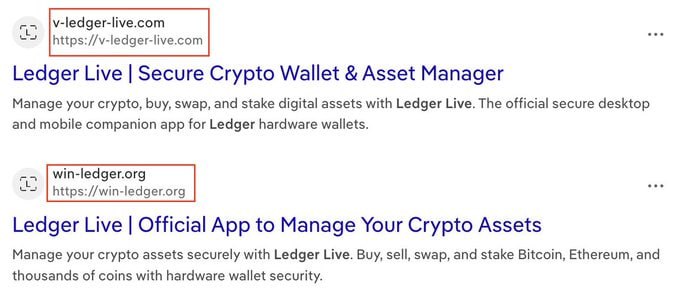
A single threat actor has reportedly stolen more than $2M in cryptocurrency through fake Ledger Live websites promoted through Google ads.
Victims were redirected to fraudulent Ledger clones and prompted to enter their 24-word recovery phrases.
One reported theft involved a Ledger user who entered their seed phrase while attempting to move their funds, resulting in the wallet being drained.
One identified threat-actor wallet reportedly consolidated around $1.9M in ETH:
0x380Fd431Cb9564A392Cf2405e02cd2a3737eab8aLedger warns that users should never enter their recovery phrase anywhere online.
❄️ @Release 💬 @Conversate
🦎 LizardSwap.com — Your #1 Crypto Exchange for NO KYC & No Frozen Funds