TGViewer
Channel Public Channel
PPHM HACKER NEWS

PPHM HACKER NEWS

@pphm_hackernews

PPHM Hacker News is a reliable news outlet that brings you the latest and most credential cyber news.

Contact us:
@pphmhackernews1

Website:
https://pphmnews.com/
Subscribers
10.7K
Photos
3.4K
Videos
9
Links
1.5K

Showing posts older than #3337 · Back to latest

Older Posts 18 shown
Post #3336 366
🔴 Storm-3168, Linked to JADEPUFFER, Abused Stolen Azure Identities

Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys.

Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same actor as Storm-3168, and its new report shows how fast this crew moves once it holds valid cloud credentials.
Post #3335 406
🔴 FBI agents’ blood tests and doctors’ notes surface after breach

It has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.

As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
Post #3334 177
🔴 Nvidia Unveils AI Agent Safety Platform With Hardware-Based Watchdog

Nvidia on Monday announced the Open Agent Safety Platform, which combines open source software and a reference system design to keep AI agents within set boundaries from testing through deployment.

The platform has two main parts. One of them is OpenShell, an open source runtime that sandboxes agents and enforces policy on what they do. The second is Sentry, a watchdog that runs separately on Nvidia’s BlueField-4 data processing units (DPUs).

Nvidia introduced OpenShell in March. The runtime, now at version 0.1.0, is broadly available. It supports agents such as Codex, Claude Code, Pi and Hermes.
Post #3333 144
🔴 JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources

The threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals.

Microsoft, which is tracking the activity under the name Storm-3168, has called it an evolution of the threat actor's tradecraft. The attack took place in early June 2026 over a period of about 18 hours.
Post #3332 151
🔴 New Mexico Jury Finds Facebook Liable for Deceiving Users About Privacy Protections

A New Mexico jury on Friday found Facebook liable for deceiving users about privacy protections on the platform in the latest legal setback against the social media giant that has already cost it billions of dollars.

The jury found over 43 million violations of state consumer protection law and it is now up to the judge to determine how much the company would pay, with attorneys representing the state asking for the maximum $5,000 penalty per violation.

“The verdict marks a significant victory for New Mexico consumers and holds one of the world’s largest technology companies accountable for its conduct,” the New Mexico Department of Justice said in a statement.
Post #3331 152
🔴 Google Warns of ShinyHunters’ Fresh Oracle PeopleSoft Campaign

Mandiant and Google Threat Intelligence Group (GTIG) over the weekend warned that the notorious extortion group ShinyHunters has launched a fresh mass-exploitation campaign targeting Oracle PeopleSoft customers.

An integrated enterprise resource planning (ERP) software suite, PeopleSoft is used across numerous large enterprises for the management of core business functions, including finance, HR, payroll, and supply chain.

Google’s warning comes four months after the hacking group was seen exploiting a zero-day vulnerability in PeopleSoft, tracked as CVE-2026-35273, to gain remote code execution without authentication.
Post #3330 138
🔴 The Arizona court system reports a cyber attack and a data breach of residents

The court IT teams identified the attack and managed to halt part of it, but the attackers had already copied personal information from the systems and notices were sent to some residents whose data was exposed/stolen.

Among the people who received the alert are residents with protective orders, and the concern is that their addresses or location information will be exposed.
Post #3329 175
🔴 Roundcube SQL injection CVE-2026-48842 is now being exploited in the wild

A Roundcube Webmail vulnerability, tracked as CVE-2026-48842 (CVSS score of 8.1) and patched four months ago, is now being exploited in the wild. The Canadian Centre for Cyber Security added the warning to its advisory on September 21, citing open-source reporting and urging administrators to apply the available updates.

The vulnerability CVE-2026-48842 affects Roundcube 1.6.x versions before 1.6.16 and 1.7.x versions before 1.7.1, but there’s an important detail: the vulnerable code sits in the virtuser_query plugin.
Post #3328 627
🔴 Canonical accelerates kernel updates: biweekly cycle arrives

The flood of discovered vulnerabilities has become so intense that Canonical's previous Ubuntu kernel update schedule is no longer adequate.

The company is migrating its stable kernels to a new SRU system: instead of a regular four-week update cycle and a separate two-week security cycle, a single two-week process will be maintained.
Post #3325 567
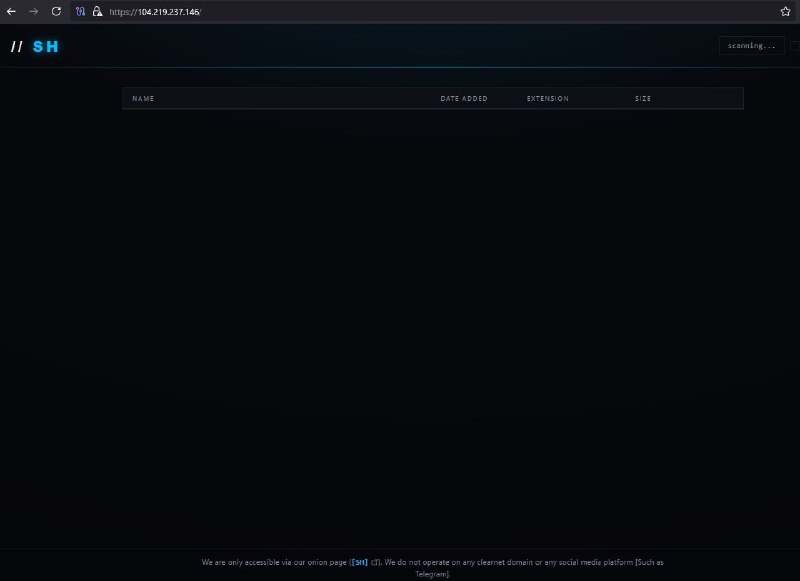
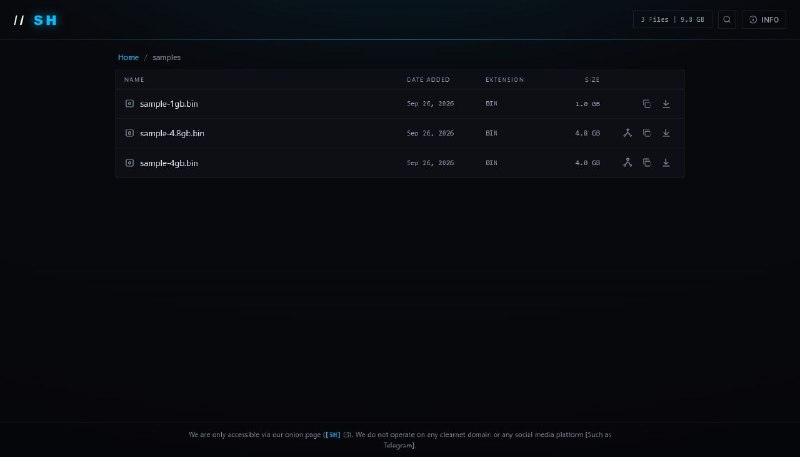
🚨 ShinyHunters:

104[.]219[.]237[.]146
ASN: 27176 🇺🇸
Org: DataWagon LLC

104[.]219[.]238[.]66
ASN: 27176 🇺🇸
Org: DataWagon LLC
  • ❤ 2
Post #3324 242
🚨 The occupation forces storming the Umm Al-Sharayet neighborhood in the city of Al-Bireh, and raiding a house‌‌
  • 🔥 1
Post #3323 225
🔴 Your Mac can become a microphone thanks to an AI agent

The Mac voice assistant can function as an external microphone and remote control. A zero-day bug has been discovered in the Muse AI agent that allows a standard local process to intercept user dictation and use the access already granted to the agent.

The issue was discovered by macOS security specialist Patrick Wardle. The vulnerability affects Meta's Muse client for macOS. The application works with files, browsers, messages, calendars, and other computer resources, while the agent itself can perform actions in the user's name. It's precisely this broad set of permissions that turns a relatively simple local error into a serious problem for AI agents.
Post #3322 223
Kosovo Operator Admits Role in Underground Identity-Theft Economy

A Kosovar national has pleaded guilty in the United States to operating Rydox, an illicit online marketplace that spent nearly a decade supplying cybercriminals with stolen identities, compromised credentials and tools used to conduct fraud.

🔗 Read More
  • ❤ 1
Post #3321 287
🔴 OpenAI attacks again! The U.S. Department of Commerce and other government websites have been hacked

The situation is really getting out of hand! If before, it was criminal "human" hackers who made headlines with major cyberattacks, now it's completely out-of-control AI agents that are making headlines.

The most disturbing point is that a private company finds itself having to publicly justify why its uncontrolled agents targeted another organization. And it wouldn't be an isolated incident: after the United States, similar incidents have also been reported in Australia.
Post #3320 250
Twenty-Year Archive Maps the Criminal Economy Behind Modern Extortion

A database containing the early history of Russian-language cybercrime forum Exploit.in is providing a rare view into how today's ransomware economy evolved from underground communities operating more than two decades ago.

🔗 Read More
  • ❤ 1
Post #3319 283
Federal Probe Exposes Alleged Foreign Control Behind Sensitive U.S. Software Supplier

U.S. authorities have arrested two executives connected to digital forensics provider Oxygen Forensics, alleging that the company concealed Russian ownership and Russia-based software development while securing contracts with sensitive American government agencies.

🔗 Read More
  • 👏 1
Post #3318 236
🔴 Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack

Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat intelligence about an imminent cyber attack.

"Kiteworks received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kiteworks systems," said Frank Balonis, Chief Information Security Officer (CISO) at Kiteworks.

"Out of an abundance of caution, we notified customers directly and recommended a precautionary shutdown window while we continue to work through the matter with federal intelligence authorities."
Post #3317 259
🔴 Pentesting with AI, but without the cloud: the model that stays in the company arrives

AI-based pentesting no longer requires sending source code to an external cloud service. Belgian company Aikido has introduced Altar, an open-source vulnerability testing model that can run on a corporate infrastructure. Altar is designed for Aikido Machine, where AI agents test applications without transferring sensitive data to an external provider.

Altar is based on Z.AI's GLM-5.3, a large mixture-of-experts architecture model. In this scheme, each request is processed by only a subset of specialized computation blocks, even though the entire set must be maintained. Aikido reduced the number of these blocks from 256 to 168 in each corresponding layer, while maintaining routing that activates eight blocks for each token.
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →