TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.31K
Photos
431
Videos
3
Links
572

Showing posts older than #618 · Back to latest

Older Posts 20 shown
Post #617 521
CVE-2026-19490: Authentication bypass in Citrix NetScaler ADC and NetScaler Gateway, 9.3 rating ‍🔥

A recently disclosed authentication bypass vulnerability affects customer-managed NetScaler ADC and NetScaler Gateway. The appliance must be configured as a Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or an AAA virtual server.

Search at Netlas.io:
👉 Link: https://nt.ls/Ebg2V
👉 Dork (NetScaler ADC): http.headers.set_cookie:"citrix_ns_id" OR http.headers.set_cookie:"ns_af" OR http.headers.set_cookie:"NSC_" OR http.headers.set_cookie:"NSC_ESNS"
👉 Dork (NetScaler Gateway): http.title:"citrix gateway" OR http.headers.set_cookie:"pwcount" OR http.favicon.hash_sha256:7b2fe2b7235b6645998edcae988ce1edaac40764c202abc3a4766db1b8ae6360 OR http.favicon.hash_sha256:3e8f8b98d8fe34a5e627c3033f0940777144effe4b5f588c67bfc6ba3bf106fa

Vendor's advisory:
https://support.citrix.com/support-home/kbsearch/article?articleNumber=CTX696939
  • 🔥 4
  • ❤ 3
Post #616 542
CVE-2026-73570: Unauthenticated RCE in Zimbra, 8.9 rating ‍🔥

A Zimbra vulnerability disclosed last week is now being actively exploited in the wild. It allows an unauthenticated attacker to execute arbitrary OS commands as the Zimbra user via specially crafted requests. Successful exploitation requires the optional zimbra-snmp package and enabled SNMP notifications.

Search at Netlas.io:
👉 Link: https://nt.ls/RfXS9
👉 Dork: tag.name:"zimbra"

Vendor's advisory:
https://wiki.zimbra.com/wiki/Zimbra_Security_Advisories
  • ❤ 3
  • 🔥 3
Post #614 463
CVE-2026-71479: Integer overflow in New API, 9.1 rating ‍🔥

A recently disclosed integer overflow vulnerability in New API allows low-privileged accounts with a positive balance or an active subscription to credit themselves an arbitrarily large amount. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/XoA0U
👉 Dork: http.favicon.hash_sha256:32132a307cad98d7f93b0384de87411f087bb34c148c932dcd5eea92101cbec3 OR http.unknown_headers.key:"x_new_api_version" OR http.title:"New API"

Vendor's advisory:
https://github.com/QuantumNous/new-api/security/advisories/GHSA-8r8v-xf7q-rcpr
  • ❤ 2
  • 🔥 2
Post #613 561
CVE-2026-65640: Authenticated RCE in WordPress, 8.8 rating ‍🔥

A recently disclosed vulnerability in WordPress allows an attacker with an Author-level privileges to upload malicious Postscript files, which could lead to RCE. This issue affects sites that use Imagick and Ghostscript.

Search at Netlas.io:
👉 Link: https://nt.ls/LrDYt
👉 Dork: tag.name:"wordpress"

Vendor's advisory:
https://github.com/WordPress/wordpress-develop/security/advisories/GHSA-8vr3-7mxf-gx8w
  • ❤ 1
  • 🔥 1
Post #611 522
CVE-2026-44901 and other: Critical bugs in Wazuh Manager, up to 9.1 rating ‍🔥

Recently disclosed vulnerabilities in Wazuh Manager allow an attacker to execute arbitrary code, read and write arbitrary files. PoCs exist for all of them!

Search at Netlas.io:
👉 Link: https://nt.ls/COx2Y
👉 Dork: certificate.issuer_dn:"Wazuh" OR http.headers.server:"Wazuh" OR raw.banner:"Unable to add agent"

Vendor's advisory:
https://github.com/wazuh/wazuh/security/advisories/GHSA-8c6v-7g3w-prrq
  • ❤ 2
  • 👍 2
  • 🔥 2
Post #610 487
CVE-2026-44945: A privilege escalation vulnerability in Rancher, 9.1 rating ‍🔥

An authenticated Rancher low-privileged user can gain full administrative access to the Rancher control plane and transitively to all downstream clusters it manages.

Search at Netlas.io:
👉 Link: https://nt.ls/FGN75
👉 Dork: http.favicon.hash_sha256:2d7adbc74e7c8941927d04e702acbff577d219fef8617c8c3014d34ae395525b OR http.body:"<title>Rancher</title>" OR http.unknown_headers.key:"x_api_cattle_auth"

Vendor's advisory:
https://github.com/rancher/rancher/security/advisories/GHSA-v584-7w32-jwpq
  • 🔥 4
  • ❤ 3
Post #609 513
0-day SQL Injection in Metabase, no CVE assigned yet, 10.0 rating ‍🔥🔥🔥

Recently disclosed vulnerability in Metabase allows an unauthenticated remote attacker to inject arbitrary SQL into the Metabase application database, which can give them administrator access to the instance. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/q4U1I
👉 Dork: http.favicon.hash_sha256:61c0353e2bde23f74f7febc277df979fbc1017186de060fd9bd8d07b65bcac13 OR http.headers.set_cookie:"metabase.DEVICE" OR http.title:"Metabase"

Vendor's advisory:
https://github.com/metabase/metabase/security/advisories/GHSA-vwf4-m7j8-wcjf
  • 🔥 4
  • ❤ 2
  • 👍 2
Post #607 519
🤖 Desktop AI Supercomputers and Automated Cyberattacks

AI supercomputers now fit on a desk. Combine them with uncensored open models and autonomous agents, and cyberattacks become cheaper, faster, and far easier to scale.

✔ Why local AI changes the economics of offensive operations
✔ How model guardrails can be removed or bypassed
✔ How agents automate reconnaissance, exploitation, and retries
✔ Why defenders must prepare for same-day, machine-speed attacks

⏱ 12 min read

👉 https://netlas.io/blog/desktop_ai_supercomputers_and_automated_attacks/
netlas.io Desktop AI Supercomputers and Automated Cyberattacks - Netlas Blog How local AI hardware, uncensored open models, and agent frameworks are lowering the cost and accelerating the scale of automated cyberattacks.
  • ❤ 5
  • 🔥 5
Post #606 506
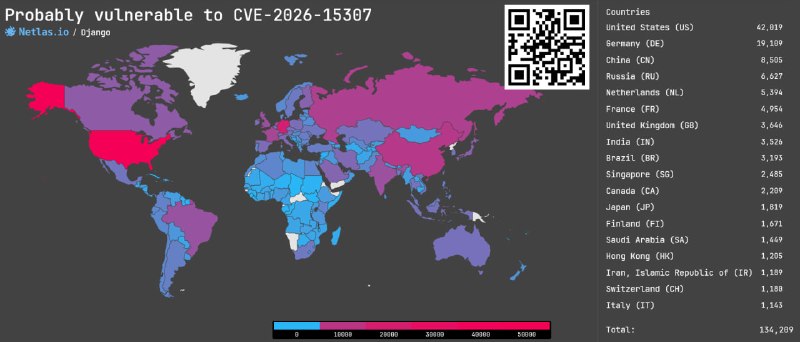
CVE-2026-15307: Server-side file-write and request forgery via spatial lookups in Django, 8.8 rating ‍🔥

Recently disclosed Django vulnerability allows an attacker to write a file to disk (in some cases enabling remote code execution) or issue a network request as the Django process user. This flaw is reachable by staff users with view permissions on any registered model containing a spatial field.

Search at Netlas.io:
👉 Link: https://nt.ls/xa9dB
👉 Dork: tag.name:"django"

Vendor's advisory:
https://www.djangoproject.com/weblog/2026/aug/04/security-releases/
  • ❤ 2
  • 🔥 1
Post #605 567
CVE-2026-16347: Possible brute-force attack in Mikrotik RouterOS, 8.8 rating ‍🔥

MikroTik RouterOS contains a weakness in its API authentication handling that allows attackers to brute-force logins for unauthorized system access.

Search at Netlas.io:
👉 Link: https://nt.ls/mMq91
👉 Dork: http.favicon.hash_sha256:6e08f1f90e778da22f07537040dfcdab9c29ac443d8386ba5be71fcbc418ff47 OR http.title:"RouterOS" OR http.body:"img src=\"mikrotik_logo.svg"

Read more:
https://www.cisa.gov/news-events/ics-advisories/icsa-26-209-05
  • 🔥 4
  • ❤ 1
Post #603 605
Command injection in Mittel MiCollab, no CVE assigned yet, 9.8 rating ‍🔥

A command injection vulnerability has been discovered in the AWV component of Mitel MiCollab. A successful exploit of this vulnerability could allow an attacker to execute arbitrary commands and potentially gain control of the system.

Search at Netlas.io:
👉 Link: https://nt.ls/t8Tk9
👉 Dork: tag.name:"micollab"

Vendor's advisory:
https://www.mitel.com/support/security-advisories/mitel-product-security-advisory-misa-2026-0006
  • ❤ 3
  • 🔥 3
  • 🕊 2
Post #602 595
CVE-2026-16812: OS Command injection in VeloCloud Orchestrator, 10.0 rating ‍🔥

A new vulnerability in Arista VeloCloud Orchestrator (VCO) allows an unauthenticated remote attacker run OS commands on the VCO host. A compromise can also expose managed devices. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/PkM4n
👉 Dork: http.body:"single-spa-application:@velocloud/vco-header" OR http.body:"vco/branding.css" OR http.body:"vco/favicon"

Vendor's advisory:
https://www.arista.com/en/support/advisories-notices/security-advisory/24364-security-advisory-0144
  • ❤ 4
  • 🔥 4
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →