TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.31K
Photos
431
Videos
3
Links
572

Showing posts older than #598 · Back to latest

Older Posts 20 shown
Post #596 615
CVE-2026-15409 & CVE-2026-15410: Two exploited in the wild vulnerabilities in SonicWall SMA1000, up to 10.0 rating 🔥

Recently disclosed vulnerabilities in SonicWall SMA1000 allow an unauthenticated attacker to open a websocket-based tunnel to arbitrary localhost-only services and subsequently execute arbitrary operating system commands as root.
These flaws are being actively exploited in the wild! PoC exists!

Search at Netlas.io:
👉 Link: https://nt.ls/I9q7F
👉 Dork: http.favicon.hash_sha256:6bb6f64adaa6a7ed4da10a2fe4edf4cb4d9914aa742c7ad607ca4ca678dcd3f1 OR certificate.subject_dn:"HTTPS Management Certificate for SonicWALL (self-signed)"

Vendor's advisory:
https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0008
  • 🔥 6
  • ❤ 4
  • 👍 3
Post #595 575
CVE-2026-56164 and other: EoP and another exploitable vulnerabilities in Microsoft SharePoint Server, 5.3 rating 🔥

A new Elevation of Privilege vulnerability in Microsoft SharePoint Server has been added to the CISA KEV, along with two previously disclosed vulnerabilities (CVE-2026-45659 & CVE-2026-32201). Attackers can chain them to gain access to SharePoint Server instances, steal IIS machine keys, and deploy malware.
🔥 All three are being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/oGZ1j
👉 Dork: tag.name:"microsoft_sharepoint"

Vendor's advisory:
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-56164
  • 🔥 5
  • 👾 4
  • ❤ 3
Post #594 587
CVE-2026-44747: Memory corruption in SAP NetWeaver AS ABAP, 9.9 rating 🔥

New vulnerability in SAP NetWeaver AS ABAP allows an authenticated attacker to abuse logical errors in memory management. This could lead to unauthorized data access, data modification, or system downtime.

Search at Netlas.io:
👉 Link: https://nt.ls/4m05i
👉 Dork: http.headers.server:"NetWeaver Application Server / ABAP"

Vendor's advisory:
https://support.sap.com/en/my-support/knowledge-base/security-notes-news/july-2026.html
  • ❤ 4
  • 🔥 4
  • 👾 4
Post #593 573
CVE-2026-57807 & CVE-2026-12761: Two vulnerable WordPress plugins by miniOrange, 9.8 rating both 🔥

There are two authentication bypass vulnerabilities disclosed in miniOrange plugins: OAuth Single Sign On - SSO & Social Login and Register (Discord, Google, Twitter, LinkedIn). These flaws might allow a malicious actor to gain admin access to the website.

Search at Netlas.io:
👉 Link: https://nt.ls/M4c8B
👉 Dork: http.body:"plugins/miniorange-oauth-oidc-single-sign-on" OR http.body:"miniorange-login-openid"

Read more:
https://patchstack.com/database/wordpress/plugin/miniorange-oauth-oidc-single-sign-on/vulnerability/wordpress-oauth-single-sign-on-sso-oauth-client-plugin-38-5-8-broken-authentication-vulnerability?_s_id=cve
https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/miniorange-login-openid/miniorange-social-login-and-register-discord-google-twitter-linkedin-770-unauthenticated-authentication-bypass-to-administrator-account-takeover-via-profile-completion-otp-flow
  • 🔥 4
  • ❤ 3
Post #592 586
Apache Kafka OAUTHBEARER authentication bypass, no CVE assigned yet, 8.1 rating 🔥

The vulnerability is a missing 'exp' enforcement in the SASL/OAUTHBEARER unauthenticated token acceptance path on the broker side. An attacker holding any historical Kafka session JWT can replay it indefinitely after the JWT's own 'exp' has passed.

Search at Netlas.io:
👉 Link: https://nt.ls/TQzt7
👉 Dork: http.title:"kafka" OR http.title:"Apache Kafka" OR http.body:"kafka" OR http.body:"Apache Kafka"

Read more:
https://seclists.org/oss-sec/2026/q3/18
  • 🔥 4
  • ❤ 3
  • 👾 3
Post #591 621
CVE-2026-56843: Cleartext FTP Password Exposure in Plesk's XML API, 9.9 rating 🔥

Exposure of cleartext FTP credentials is possible in Plesk's XML API, which may allow a low-privileged attacker to upload malicious files and execute arbitrary code remotely (RCE) as another tenant's system user.

Search at Netlas.io:
👉 Link: https://nt.ls/MZtlo
👉 Dork: tag.name:"plesk"

Vendor's advisory:
https://support.plesk.com/hc/en-us/articles/41178305151255-Vulnerability-in-Plesk-XML-API-Cleartext-FTP-Password-Exposure
  • ❤ 3
  • 🔥 3
Post #589 687
CVE-2026-57517: Blind SQL Injection in Control Web Panel, 9.8 rating 🔥

SQL Injection flow in Control Web Panel allows remote code execution. PoC is now available!

Search at Netlas.io:
👉 Link: https://nt.ls/biQe7
👉 Dork: http.title:"CWP ADMIN" OR http.favicon.hash_sha256:69cd33a03067a7a00b6a743e52b357cd46ffdfeb1d72beaf44f2ffd9abfc153a OR http.headers.server:cwpsrv

Read more:
https://karmainsecurity.com/KIS-2026-12
  • 🔥 5
  • ❤ 3
  • 👍 2
  • 👾 1
Post #588 596
🚧 Planned Maintenance

Netlas will be unavailable for up to an hour today, starting at 11:30 UTC.

We have to reboot the whole system after maintenance. Thank you for your understanding and patience. We are sorry for any inconvenience this may cause.
  • 🕊 5
  • ❤ 1
Post #587 636
CVE-2026-48276 and other: A lot of vulnerabilities in Adobe ColdFusion, 6 of them are 10.0 rating 😱

The last Adobe security bulletin disclosed 6 RCE vulnerabilities in Adobe ColdFusion with highest severity and other critical issues such as arbitrary file read and privilege escalation.

Search at Netlas.io:
👉 Link: https://nt.ls/GxXdK
👉 Dork: tag.name:"adobe_coldfusion"

Vendor's advisory:
https://helpx.adobe.com/security/products/coldfusion/apsb26-68.html
  • ❤ 5
  • 👍 1
Post #586 1.03K
CVE-2026-49869 & CVE-2026-53576: Two RCE vulnerabilities in kestra, 10.0 rating 😱

Recently disclosed vulnerabilities in Kestra allow an unauthenticated remote attacker to execute arbitrary code as root.

Search at Netlas.io:
👉 Link: https://nt.ls/58ToN
👉 Dork: http.title:kestra OR http.favicon.hash_sha256:26119c9b0a6c4e82ae8c2d367e4a7cb56a30c4da664b7185d14f6fbdf50f8ec8

Read more:
https://github.com/kestra-io/kestra/security
  • 🔥 4
  • ❤ 2
Post #584 789
CVE-2026-12046: RCE vulnerability in pgAdmin 4, 9.5 rating 🔥

Two SQL Editor endpoints were missing the login-required decorator and were reachable without authentication in server mode. This exposes an unauthenticated remote code execution path in the pgAdmin process.

Search at Netlas.io:
👉 Link: https://nt.ls/jbYEF
👉 Dork: http.title:"pgAdmin" OR http.headers.set_cookie:"pga4_session=" OR http.favicon.hash_sha256:c3251099ffc5ed057dcbb624adbe79fa5794a0c64684442c1eaf1abc3edf7bde OR http.favicon.hash_sha256:6afa287fc6721817d9931bd8d7a796646ea535596f8bb038ff048666e19cfd17

Read more:
https://github.com/pgadmin-org/pgadmin4/issues/10072
  • ❤ 3
  • 🔥 3
  • 👍 2
  • 👾 2
Post #583 627
CVE-2026-8713: Arbitrary file deletion in Avada Builder WordPress plugin, 9.1 rating 🔥

New vulnerability in Avada Builder WordPress plugin (formerly Fusion Builder) allows an unauthenticated attacker to delete any file on the server. It can easily lead to remote code execution when the right file is deleted.

Search at Netlas.io:
👉 Link: https://nt.ls/ohFG5
👉 Dork: http.body:"wp-content/plugins/fusion-builder"

Read more:
https://www.wordfence.com/blog/2026/06/critical-unauthenticated-arbitrary-file-deletion-vulnerability-patched-in-avada-builder-wordpress-plugin/
  • ❤ 5
  • 🔥 4
  • 👾 2
Post #582 719
CVE-2026-10829: Remote code execution in Moxa NPort, 8.6 rating 🔥

A stack-based buffer overflow in Moxa NPort allows an attacker to corrupt memory by sending crafted input. It could achieve remote code execution with root privileges.

Search at Netlas.io:
👉 Link: https://nt.ls/12mUL
👉 Dork: http.title:"NPort Web Console" OR http.headers.server:"MoxaHttp" OR http.body:"NPort Web Console" OR http.body:"<TITLE>OnCell" OR http.body:"<TITLE>Moxa OnCell"

Vendor's advisory:
https://www.moxa.com/en/support/product-support/security-advisory/mpsa-261910-cve-2026-10828,-cve-2026-10829-use-of-externally-controlled-format-string-and-stack-based-buffer-overflow-v
  • 🔥 7
  • ❤ 2
  • 👾 2
  • 👍 1
Post #580 753
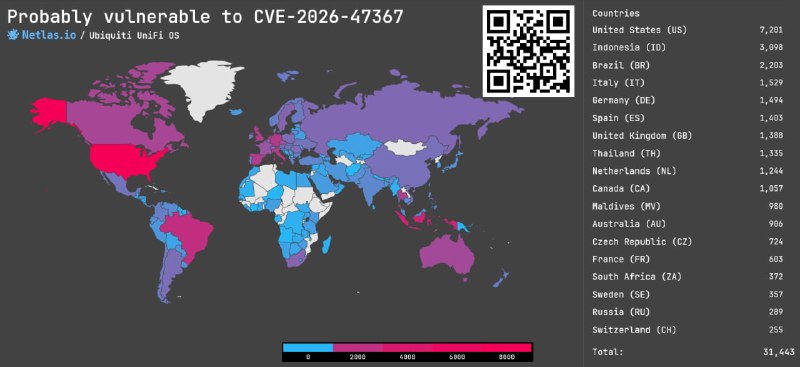
CVE-2026-47367 and other: Improper Input Validation vulnerabilities in Ubiquiti UniFi OS, 9.9 rating 🔥

Several improper input validation and other weaknesses allow low-privileged attacker to execute command injection and possible to compromise network.

Search at Netlas.io:
👉 Link: https://nt.ls/TczjZ
👉 Dork: tag.name:"ubiquiti_unifi"

Vendor's advisory:
https://community.ui.com/releases/Security-Advisory-Bulletin-065-065/aa46a22b-fc43-4eae-9382-6fc8feda967a
  • 👍 4
  • 🔥 4
  • ❤ 3
  • 👾 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →