TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.31K
Photos
432
Videos
3
Links
573

Showing posts older than #578 · Back to latest

Older Posts 20 shown
Post #577 715
📘 Attackers no longer need custom malware

Legitimate Remote Monitoring & Management (RMM) tools like AnyDesk, ScreenConnect, TeamViewer, Atera, and others are increasingly being weaponized for initial access, persistence, and ransomware operations.

Our latest research breaks down how threat actors abuse RMM platforms, common attack chains, detection opportunities, and defensive measures.

👉 Read the blog: https://netlas.io/blog/weaponized_rmm/
netlas.io Weaponized RMM: Hunting the Adversary Abuse of Remote Monitoring Tools - Netlas Blog Analysis of adversary abuse of RMM tools, phishing-to-RMM delivery, Netlas hunt pivots, IOCs, and defensive detection strategies.
  • 🔥 5
  • 👾 3
  • 👍 2
Post #576 808
CVE-2026-47783 & CVE-2026-47784: Two SASL vulnerabilities in Memcached, 8.1 rating 🔥

Two new vulnerabilities Memcached allow an attacker to enumerate valid usernames on the system and guess their passwords because password and username data for SASL password database authentication has a timing side channel.

Search at Netlas.io:
👉 Link: https://nt.ls/zZBd0
👉 Dork: memcached.version:<1.6.42

Read more:
https://github.com/memcached/memcached/wiki/ReleaseNotes1642
  • 🔥 3
  • ❤ 2
  • 👾 2
Post #575 836
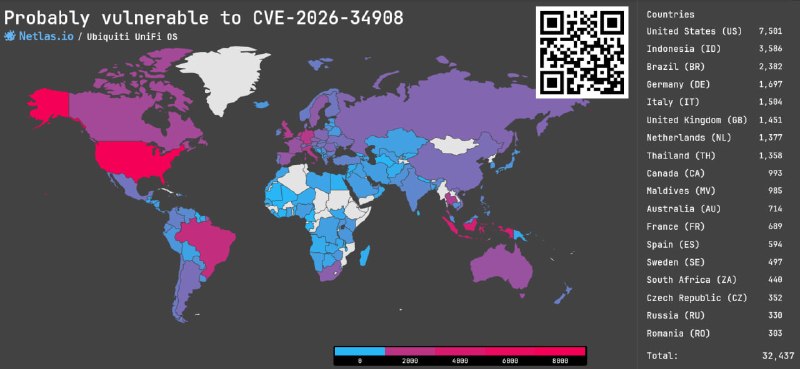
CVE-2026-34908, CVE-2026-34909 & CVE-2026-34910: Vulnerabilities in Ubiquiti UniFi OS, 10.0 rating 🔥🔥🔥

Three new vulnerabilities in Ubiquiti UniFi OS allow an network attacker to make unauthorized changes, access files and execute arbitrary command. It may cause to full device compromise.

Search at Netlas.io:
👉 Link: https://nt.ls/oMQHo
👉 Dork: tag.name:"ubiquiti_unifi"

Vendor's advisory:
https://community.ui.com/releases/Security-Advisory-Bulletin-064-064/84811c09-4cf4-42ab-bd61-cc994445963b
  • 🔥 3
  • ❤ 2
Post #574 729
CVE-2026-46354: Token theft in Coder, 9.1 rating 🔥

New vulnerability in Coder allows an attacker on any Azure VM to steal an agent session token, and with the stolen token get access to Git SSH private key, OAuth access tokens or workspace secrets.

Search at Netlas.io:
👉 Link: https://nt.ls/JwI80
👉 Dork: http.favicon.hash_sha256:05d85ef30160f0c790ba0acf9470dae35a85a90a2b79387fe4b6994852c1dbf4 OR http.meta:"https://coder.com/docs" OR http.unknon_headers.key:"x_coder_request_id" OR http.unknown_headers.key:"x_coder_build_version"

Vendor's advisory:
https://github.com/advisories/GHSA-6x44-w3xg-hqqf
  • 🔥 3
  • ❤ 2
Post #572 575
📓 Discovering Data Exposure with Netlas

A practical walkthrough of how security researchers can use Netlas to identify exposed / leaked sensitive data across internet-facing systems.

✔ Methods for finding leaked data
✔ Common exposure patterns
✔ Real-world search techniques

👉 Read the article: https://netlas.io/blog/discovering_data_exposure_with_netlas/
netlas.io Discovering Data Exposure with Netlas - Netlas Blog How to discover exposed configuration files, API keys, database credentials, bearer tokens, and debug outputs using Netlas response data.
  • 👍 5
  • 👏 3
Post #571 528
🌍 Netlas v1.8 is live

Private Scanner now supports Scanner Locations!

Run scans from different countries to see infrastructure from multiple geographic perspectives.

New in this release:
✓ Distributed Scanner Locations
✓ Location details in reports & API
✓ UI polish and ASD bug fixes.

👉 Details: https://docs.netlas.io/changelog/
  • 🔥 6
  • 👾 2
Post #570 551
CVE-2026-44789, CVE-2026-44790 & CVE-2026-44791: 3 new vulnerabilities in n8n, 9.4 rating 🔥

Recently disclosed vulnerabilities in n8n allow an attacker to read arbitrary files from the server, achieve global prototype pollution and bypass the patch for previous vulnerability (CVE-2026-42232).

Search at Netlas.io:
👉 Link: https://nt.ls/dRB5p
👉 Dork: http.title:"n8n.io - Workflow Automation"

Read more:
https://github.com/n8n-io/n8n/security
  • 🔥 4
  • ❤ 3
Post #569 604
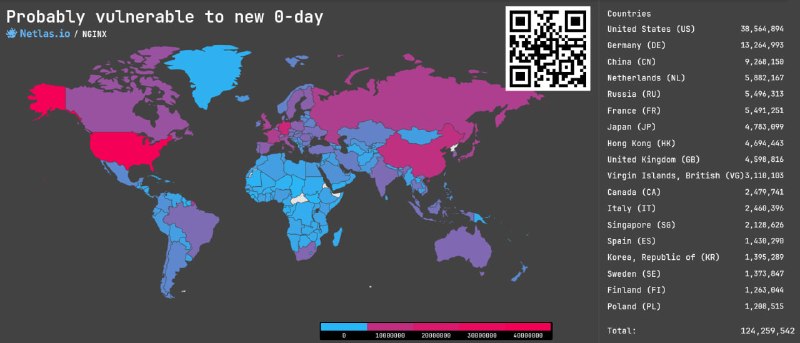
CVE-2026-42945: 18-Year-Old vulnerability in NGINX, 9.2 rating 🔥

Heap buffer overflow vulnerability in NGINX Plus and NGINX Open Source allows an unauthenticated attacker to lead NGINX worker process to restart by sending crafted HTTP requests. Additionally, in some cases code execution is possible. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/9xSvG
👉 Dork: tag.name:nginx

Vendor's advisory:
https://my.f5.com/manage/s/article/K000161019
  • 🔥 5
  • 👾 3
  • ❤ 2
Post #568 672
CVE-2026-42897: Microsoft Exchange Server spoofing vulnerability, 8.1 rating 🔥

New spoofing vulnerability in on-premise Microsoft Exchange Server hits OWA and allows an unauthorized attacker to execute malicious code by sending a specially crafted email to a user. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/64QAo
👉 Dork: tag.name:"microsoft_exchange"

Vendor's advisory:
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-42897
  • 🔥 4
  • 👍 3
  • 👾 2
Post #567 648
CVE-2026-44194 & CVE-2026-45158: Two RCE vulnerabilities in OPNsense, 9.1 rating 🔥

Two vulnerabilities in OPNsense allows an authenticated attacker to execute arbitrary code as root on the firewall host via User management system (CVE-2026-44194) and DHCP Config (CVE-2026-45158). PoC already available!

Search at Netlas.io:
👉 Link: https://nt.ls/S0qIg
👉 Dork: tag.name:opnsense

Vendor's advisory:
https://github.com/opnsense/core/security
  • 🔥 5
  • 👾 5
  • 👍 4
Post #565 618
CVE-2026-43640: Missing authentication in JetBrains TeamCity, 8.2 rating 🔥

Vulnerability in JetBrains TeamCity allows an authenticated user to expose server API to unauthorized access.

Search at Netlas.io:
👉 Link: https://nt.ls/7tWNf
👉 Dork: http.headers.set_cookie:TCSESSIONID OR http.title:"teamcity" OR http.unknown_headers.key:"teamcity_node_id" OR http.meta:"teamcity"

Read more:
https://www.jetbrains.com/privacy-security/issues-fixed/
  • 🔥 5
  • ❤ 2
  • 👍 1
Post #564 617
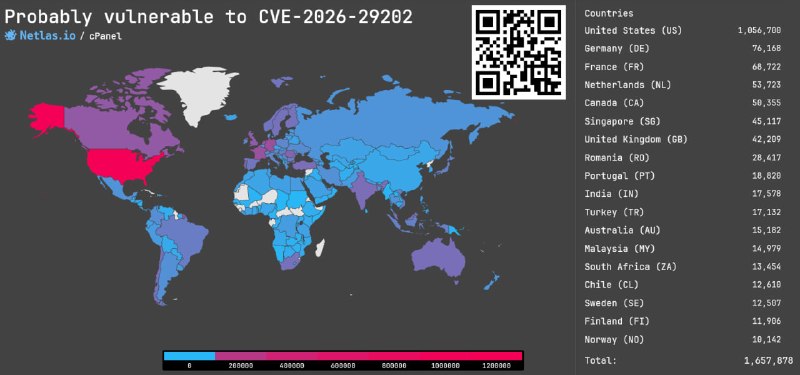
CVE-2026-29202 & CVE-2026-29203: Two vulnerabilities in cPanel, 8.8 rating 🔥

The first vulnerability in cPanel allows an attacker to execute arbitrary commands directly on the server via Perl injection (CVE-2026-29202). The second one (CVE-2026-29203) leads to denial of service and possible privilege escalation.

Search at Netlas.io:
👉 Link: https://nt.ls/2en2n
👉 Dork: http.title:cpanel OR http.headers.set_cookie:"cprelogin" OR http.headers.set_cookie:"cpsession"

Vendor's advisory: https://support.cpanel.net/hc/en-us/articles/40311426610327-Security-CVE-2026-29202-cPanel-WHM-WP2-Security-Update-May-08-2026
https://support.cpanel.net/hc/en-us/articles/40311543760407-Security-CVE-2026-29203-cPanel-WHM-WP2-Security-Update-May-08-2026
  • 🔥 6
  • ❤ 1
  • 👍 1
Post #561 713
CVE-2026-0204 and other: Several vulnerabilities in SonicWall SonicOS, up to 8.0 rating 🔥

Several vulnerabilities in SonicWall SonicOS allow attacker to bypass access controls, to interact with usually restricted services, or to crash a firewall.

Search at Netlas.io:
👉 Link: https://nt.ls/H8DoW
👉 Dork: http.favicon.hash_sha256:6bb6f64adaa6a7ed4da10a2fe4edf4cb4d9914aa742c7ad607ca4ca678dcd3f1 OR certificate.subject_dn:"HTTPS Management Certificate for SonicWALL (self-signed)"

Vendor's advisory: https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0004
  • 🔥 5
  • ❤ 2
  • 👍 2
Post #560 664
🚀 Introducing the Netlas Docs MCP Server

We believe most of you already use AI agents in your daily work, so we decided to make Netlas easier to use with them.

Meet the Netlas Docs MCP Server — a simple way to give AI assistants direct access to the latest Netlas documentation and reference data.

Now your assistant can:
• find exact field names for queries
• explain how data is indexed and searched
• check API endpoints and formats
• pull up-to-date plan and feature details

If you rely on Netlas for research, automation, or bug bounty work, this helps your AI tools stay accurate and up to date.

👉 Get started: https://docs.netlas.io/knowledge-base/mcp-server/
  • 🔥 7
  • ❤‍🔥 2
  • 👍 2
  • ❤ 1
Post #559 567
CVE-2026-42208: SQL Injection in LiteLLM, 9.3 rating 🔥

Pre-authentication SQL Injection in LiteLLM allows an attacker to read data from the proxy's database and modify it. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 https://nt.ls/4MNkt
👉 Dork: http.title:LiteLLM OR http.favicon.hash_sha256:26e3e882e76c2dc171b1bda49455641e812b3524f1692729b1fde849b7d52a6f

Read more: https://webflow.sysdig.com/blog/cve-2026-42208-targeted-sql-injection-against-litellms-authentication-path-discovered-36-hours-following-vulnerability-disclosure
  • ❤ 2
  • 👍 2
  • 🔥 2
  • 🥰 2
Post #558 558
CVE-2026-42231 and CVE-2026-42232: Two Prototype Pollution vulnerabilities in n8n, 9.4 & 10.0 rating 🔥🔥

Two recently disclosed Prototype Pollution vulnerabilities in n8n allow an authenticated attacker to execute arbitrary code on the server.

Search at Netlas.io:
👉 https://nt.ls/beZWa
👉 Dork: http.title:"n8n.io - Workflow Automation"

Read more: https://github.com/n8n-io/n8n/security
  • ❤ 4
  • 🔥 3
  • 👍 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →