TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.31K
Photos
432
Videos
3
Links
573

Showing posts older than #558 · Back to latest

Older Posts 20 shown
Post #557 645
CVE-2026-3844: Unrestricted Arbitrary File Upload in Breeze WordPress plugin, 9.8 rating 🔥

Unrestricted Arbitrary File Upload in Breeze WordPress plugin allows an unauthenticated attacker to upload web shell and execute it remotely. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 https://nt.ls/61VeQ
👉 Dork: http.body:"plugins/breeze"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/breeze/breeze-cache-244-unauthenticated-arbitrary-file-upload-via-fetch-gravatar-from-remote
  • 🔥 5
  • 👍 2
  • ❤ 1
Post #556 552
🚧 Planned Maintenance

Netlas will be unavailable for up to two hours on the weekend of April 26, 2026, starting at 08:00 UTC.

We will be reconfiguring our network. We expect the downtime to be no longer than two hours and will work to complete it as quickly as possible.

Thank you for your understanding and patience. We are sorry for any inconvenience this may cause.
  • 😢 2
  • ❤ 1
  • 👍 1
  • 🥰 1
Post #554 564
CVE-2026-21571: OS Command Injection in Atlassian Bamboo Data Center, 9.4 rating 🔥

RCE vulnerability in Atlassian Bamboo Data Center allows an authenticated attacker to execute commands on affected servers. It may cause to full server compromise.

Search at Netlas.io:
👉 https://nt.ls/KqPWl

Vendor's advisory: https://jira.atlassian.com/browse/BAM-26364
  • 🔥 5
  • 👍 3
  • 👏 3
Post #553 545
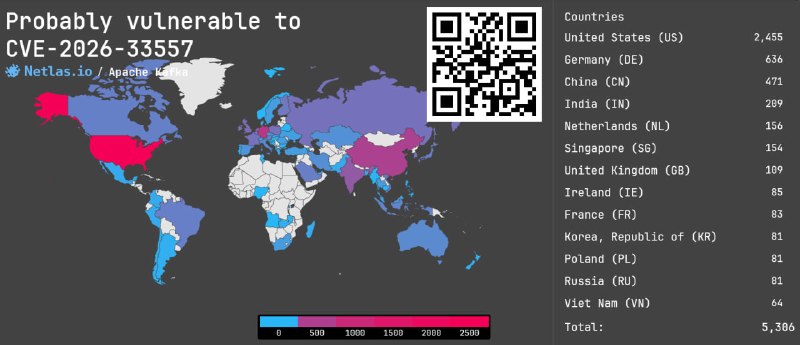
CVE-2026-33557, and CVE-2026-33558: Vulnerabilities in Apache Kafka, up to 9.1 rating 🔥

Two new vulnerabilities in Apache Kafka: the first allows attacker to generate their own JWT from any issuer, the second flow is the sensitive information disclosure, if the NetworkClient component is set to the DEBUG log level.

Search at Netlas.io:
👉 Link: https://nt.ls/M6oTa
👉 Dork: http.title:”kafka” OR http.title:”Apache Kafka” OR http.body:”kafka” OR http.body:”Apache Kafka”

Read more: https://kafka.apache.org/community/cve-list/
  • 🔥 4
  • 👍 3
  • ❤ 2
Post #552 547
Netlas v1.7 is out

📊 Private Scanner Reports — summarized scan results for quick review and comparison.
🧩 Datasets now use NDJSON/JSONL format — easier to stream from archives.
🛠 Improved discovery & mapping UI, mobile experience, and host view.

Details at https://docs.netlas.io/changelog/
docs.netlas.io Changelog - Netlas Docs Explore the latest updates, enhancements, and fixes on the Netlas platform. Stay informed with our Changelog for all product and feature developments.
  • 🔥 4
  • ❤ 2
Post #551 605
CVE-2026-40530, CVE-2026-4036, and others: Vulnerabilities in Synology DSM, up to 8.0 rating 🔥

Several vulnerabilities in Synology DiskStation Manager (DSM) allow remote authenticated attacker to read or write files, conduct denial-of-service attacks, and obtain information, including arbitrary sharing files.

Search at Netlas.io:
👉 Link: https://nt.ls/Ap4pz
👉 Dork: http.favicon.hash_sha256:b8f4bb2e2ba81cb86875fb89db4571278d6e23fd888313d0f4152b1adbc8bd08

Vendor's advisory: https://www.synology.com/en-us/security/advisory/Synology_SA_26_06
  • 🔥 5
  • ❤ 3
  • 👍 2
Post #550 682
🤖 Abuse of Telegram Bot API

Exploring how attackers misuse Telegram bots in real-world campaigns.

• Learn how attackers use Telegram for C2, telemetry, and data exfiltration
• See detailed case studies with real IOCs
• Understand stable detection patterns that work beyond hashes and domains

⏱️ 15 min read

👉🏼 Read the post:
https://netlas.io/blog/abuse_of_telegram_bot_api/
netlas.io Telegram Bot API Abuse - Netlas Blog How threat actors abuse Telegram Bot API for phishing, telemetry, and malware delivery. Hunting techniques and case studies.
  • ❤ 5
  • 🔥 5
Post #549 615
CVE-2026-32201: Microsoft SharePoint Server Spoofing Vulnerability, 6.5 rating ❗️

Improper input validation in Microsoft SharePoint Server allows an unauthorized attacker to perform spoofing over a network and view sensitive internal data or make unauthorized changes. This vulnerability is already being actively exploited in the wild!

Search at Netlas.io:
👉 Link: https://nt.ls/DjQpd
👉 Dork: http.headers.microsoftsharepointteamservices:*
👉 Dork (MS subdomains filtered): http.headers.microsoftsharepointteamservices:* !host:*.sharepoint.com

Vendor's advisory: https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-32201
  • 👍 5
  • 🔥 4
  • ❤ 3
Post #547 636
CVE-2026-5173, CVE-2026-1092, CVE-2025-12664 and other: Vulnerabilities in GitLab CE and EE, up to 8.5 rating 🔥

Several vulnerabilities in GitLab could compromise code integrity and allow an unauthenticated user to cause denial of service.

Search at Netlas.io:
👉 Link: https://nt.ls/QGxUF
👉 Dork: http.title:"GitLab" OR http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef

Vendor's advisory: https://about.gitlab.com/releases/2026/04/08/patch-release-gitlab-18-10-3-released/
  • ❤ 2
  • 👍 2
  • 🔥 2
Post #546 608
CVE-2026-4112 and other: SQL injection and TOTP vulnerabilities in SonicWall SMA 1000 Series, up to 7.2 rating ❗️

The most severe vulnerability (SQL injection) allows remote authenticated attacker with read-only administrator privileges to escalate privileges to primary administrator.

Search at Netlas.io:
👉 Link: https://nt.ls/mzseI
👉 Dork: http.favicon.hash_sha256:6bb6f64adaa6a7ed4da10a2fe4edf4cb4d9914aa742c7ad607ca4ca678dcd3f1 OR certificate.subject_dn:"HTTPS Management Certificate for SonicWALL (self-signed)"

Vendor's advisory: https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0003
  • ❤ 4
  • 🔥 4
Post #545 562
Post #544 617
CVE-2026-0740: Vulnerability in Ninja Forms WordPress plugin, 9.8 rating

The vulnerability allows unauthenticated attackers to upload arbitrary files to a vulnerable site and achieve remote code execution.

Search at Netlas.io:
👉 Link: https://nt.ls/rkM7h
👉 Dork: http.body:"plugins/ninja-forms"

Read more: https://www.wordfence.com/blog/2026/04/50000-wordpress-sites-affected-by-arbitrary-file-upload-vulnerability-in-ninja-forms-file-upload-wordpress-plugin/
  • 🔥 8
Post #542 934
⭐️ Ever wondered how professional threat intelligence feeds are actually built?

Our partners at RST Cloud pull back the curtain on their approach to threat hunting — revealing how they identify, track, and expand command-and-control (C2) infrastructure at scale.

🔍 Inside the post:
• How RST Cloud discovers malicious infrastructure in the wild
• Techniques for linking isolated IoCs into meaningful threat clusters
• The methodology behind building reliable, high-quality threat intelligence feeds
• How Netlas data helps enrich and accelerate investigations

This is a rare look into the real workflows behind modern threat intelligence — straight from a team doing it every day.

🕒 5 min read

👉 https://netlas.io/blog/с2_hunting_by_rst_cloud/
netlas.io How we hunt C2 infrastructure at RST Cloud using Netlas - Netlas Blog RST Cloud's C2 hunting workflow with Netlas: use JARM, HTTP headers, certificates, and domain pivots to detect active malicious infrastructure early.
  • 👍 3
  • ❤ 2
  • 🔥 2
Post #539 1.14K
Netlas v1.6 is out

🔍 Private Scanner now supports “Scan all ports” — non-intrusive scans across 65,536 TCP ports.
🆕 Added CWMP protocol support.
⚠️ Breaking change: updated Discovery API response format for groups.

Details at https://docs.netlas.io/changelog/
docs.netlas.io Changelog - Netlas Docs Explore the latest updates, enhancements, and fixes on the Netlas platform. Stay informed with our Changelog for all product and feature developments.
  • 🔥 5
  • ❤ 4
  • 👍 3
Post #538 962
CVE-2026-1490: Vulnerability in CleanTalk WordPress plugin, 9.8 rating 🔥

The vulnerability allows attackers to install any plugin on an affected website, which could be the first step in any attack chain.

Search at Netlas.io:
👉 Link: https://nt.ls/wZ4Qu
👉 Dork: http.body:"plugins/cleantalk-spam-protect"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/cleantalk-spam-protect/spam-protection-honeypot-anti-spam-by-cleantalk-671-authorization-bypass-via-reverse-dns-ptr-record-spoofing-to-unauthenticated-arbitrary-plugin-installation
  • ❤ 3
  • 👍 3
  • 👾 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →