TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.32K
Photos
432
Videos
3
Links
573

Showing posts older than #518 · Back to latest

Older Posts 20 shown
Post #517 811
Netlas is back online 🚀

We’ve just finished rolling out Netlas v1.4.0 — a major upgrade that took a bit longer than expected, but it’s now live and ready to use.

Here’s what’s new:

🧭 Discovery Tool: significantly improved UI and reworked flow — discovery now runs in the background so you can keep exploring your attack surface while data is being fetched.
🌐 Port coverage: public scans now cover 1,000+ ports for broader visibility into exposed services.
🔍 Tech detection: improved HTTP software detection; the next public scan will include 6,000+ application and technology names.
📊 CVE mapping: completely redesigned mapping via CPEs and product names, plus a new sortable, filterable vulnerabilities table in the UI.
📦 Private Scanner: major data storage redesign after a year of intensive use, improving reliability and paving the way for future features.
🔁 API change: when using the indices parameter, you now pass the scan label instead of its numeric ID.

Thanks a lot for your patience and support — it helped us get this release over the line.

👉 Full changelog and migration details: https://docs.netlas.io/changelog/
docs.netlas.io Changelog - Netlas Docs Explore the latest updates, enhancements, and fixes on the Netlas platform. Stay informed with our Changelog for all product and feature developments.
  • ❤ 3
  • 🔥 3
  • 🎉 2
  • 👾 2
Post #516 684
Netlas.io 🚧 Planned Maintenance 🚧 An application will be unavailable for a period of time❗️ On Thursday, November 27, 2025, at 09:00 UTC ⏰, a major update will be implemented, which will also require changes to the structure of the Netlas databases. This will take…
❗️ Maintenance Update ❗️

Due to additional testing, the update has been postponed to Friday, November 28, 2025, at 08:00 UTC ⏰.

Please remember to save your work before this time.
  • 🕊 3
Post #515 763
CVE-2024-9183, -12571, and other: Multiple vulnerabilities in GitLab, 2.4 - 7.7 rating❗️

In a recent advisory, GitLab reports several vulnerabilities, including Race Conditions, DoS, and Authentication Bypass.

Search at Netlas.io:
👉 Link: https://nt.ls/IH1NS
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/11/26/patch-release-gitlab-18-6-1-released/
  • 👾 4
  • 👍 1
Post #514 629
🚧 Planned Maintenance 🚧
An application will be unavailable for a period of time❗️

On Thursday, November 27, 2025, at 09:00 UTC ⏰, a major update will be implemented, which will also require changes to the structure of the Netlas databases. This will take several hours, during which time the service will be down. Our team will do everything possible to complete this task as quickly as possible.

Please remember to save your work before this time.
  • 🕊 3
Post #513 663
CVE-2025-64656, -64657: Two vulnerabilitites in Azure Application Gateway, 9.4 - 9.8 rating 🔥

Among the vulnerabilities recently published by Microsoft are Stack-based Buffer Overflow and Out-of-bounds Read, which allow an attacker to escalate privileges.

Search at Netlas.io:
👉 Link: https://nt.ls/2xeMm
👉 Dork: http.headers.server:"Azure Application Gateway"

Vendor's advisory: https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-64657
  • 👾 4
  • 🔥 1
Post #512 794
From Starlink to Star Wars: The Real Cyber Threats in Space 🛸

Satellites now prop up navigation, finance, aviation, weather, even battlefields — and that makes them prime targets. Our new piece maps how space systems are attacked across the ground, link, and space segments, what went wrong in real incidents, and which controls actually help. No, it’s not the Death Star you should fear — it’s the dish on your roof. These are not the packets you’re looking for.

What’s inside:

🌌 Mega-constellations & dependencies: why thousands of LEO nodes + private networks raise systemic risk.
🛰 Anatomy of a satellite: bus, payload, TT&C — and where command hijack, unpatched firmware, and telemetry tampering creep in.
📡 Ground first: supply-chain compromise, phishable ops networks, and user-terminal takeover.
🎚RF attacks: jamming, spoofing, and cheap SDR eavesdropping turning “space-only” data into low-cost targets.
📝Case studies you can brief with: Viasat KA-SAT (AcidRain) and Landsat/Terra ground-station intrusions — play-by-play included.

👉 Read now: https://netlas.io/blog/space_cyber_threats/
netlas.io From Starlink to Star Wars - The Real Cyber Threats in Space - Netlas Blog Explores how AI, cyber attacks and megaconstellations turn satellites into critical targets — and why securing space infrastructure is urgent.
  • 🔥 3
  • 👾 3
  • 👍 2
  • ❤ 1
Post #511 755
We are currently experiencing a full service outage caused by a major Cloudflare CDN failure.

At the moment, Netlas App, API, and documentation portal are unavailable.

Our backend systems are running, but Cloudflare’s outage prevents any traffic from reaching our infrastructure.

We are actively monitoring Cloudflare’s incident and will restore service as soon as connectivity is back.
  • 🙏 7
  • 🗿 2
Post #509 740
CVE-2025-64500: Authorization Bypass in Symfony, 7.3 rating❗️

The vulnerability allows attackers to bypass certain access restrictions based on the leading "/" character.

Search at Netlas.io:
👉 Link: https://nt.ls/yxfE1
👉 Dork: http.body:"Symfony Web Debug Toolbar" OR http.title:"Welcome to Symfony!" OR http.title:"symfony project"

Vendor's advisory: https://symfony.com/blog/cve-2025-64500-incorrect-parsing-of-path-info-can-lead-to-limited-authorization-bypass
  • 👾 5
  • 👍 1
Post #507 699
CVE-2025-11224 and other: Multiple vulnerabilities in GitLab, 3.1 - 7.7 rating❗️

In a new bulletin, GitLab described nine vulnerabilities for CE and EE. These include XSS, Information Disclosure, Prompt Injection, and others.

Search at Netlas.io:
👉 Link: https://nt.ls/7x1Mf
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/11/12/patch-release-gitlab-18-5-2-released/
  • 👾 6
  • 👍 1
Post #505 1.4K
📌 LLM Vulnerabilities: how AI apps break — and how to harden them

This piece maps the most common ways LLM-powered systems fail in the real world and turns them into a practical hardening plan. From prompt and indirect injection to over-privileged tools, leaky RAG pipelines, data poisoning, jailbreaks, and supply-chain traps — plus the guardrails that actually help in production.

Key takeaways:
1️⃣ Prompt & indirect injection: attackers hide instructions in web pages, files, or retrieved notes; the model obeys them and exfiltrates secrets or performs unwanted actions.
2️⃣ Jailbreaks & policy evasion: harmless-looking reformulations bypass safety layers; outputs become unsafe or operationally risky.
3️⃣ RAG data leaks: sloppy retrieval exposes internal docs, customer data, and system prompts; cross-tenant bleed is a real risk.
4️⃣ Over-privileged tools/agents: broad filesystem, network, or payment permissions turn one prompt into a breach.
5️⃣ Poisoning & supply chain: tainted datasets, third-party prompts, and unpinned models/extensions undermine trust.
6️⃣ Output trust & hallucinations: fabricated facts sneak into workflows, tickets, or code — and humans often rubber-stamp them.
7️⃣ Telemetry gaps: without red-team sims and runtime monitoring, you won’t see injection attempts until damage is done.

👉 Read here: https://netlas.io/blog/llm_vulnerabilities/
netlas.io LLM Vulnerabilities: Why AI Models Are the Next Big Attack Surface - Netlas Blog LLM vulnerabilities explained: prompt injection, data leaks, RAG risk, supply chain, and real incidents — plus OWASP guidance, mitigations, and testing tactics.
  • 👾 4
  • ❤ 2
  • 🔥 1
Post #503 770
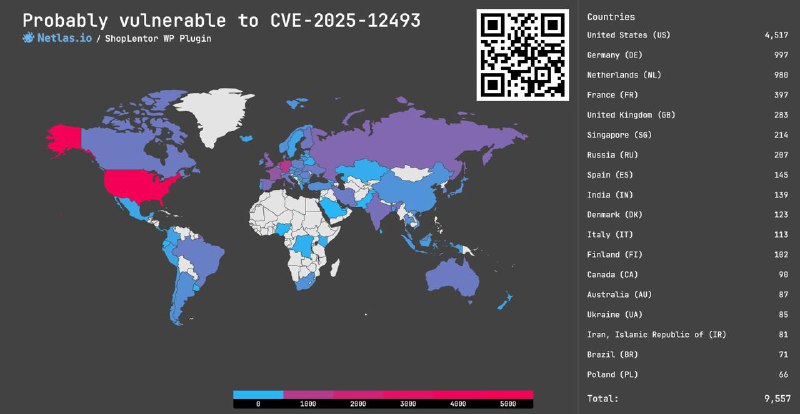
CVE-2025-8489: Path Traversal in ShopLentor WordPress Plugin, 9.8 rating 🔥

A recent vulnerability in the ShopLentor (formerly WooLentor) plugin allows unauthenticated attackers to execute any code from PHP files on the server.

Search at Netlas.io:
👉 Link: https://nt.ls/wKuHH
👉 Dork: http.body:"plugins/woolentor-addons"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/woolentor-addons/shoplentor-325-unauthenticated-local-php-file-inclusion-via-load-template
  • 👾 5
  • 🤔 2
  • 👍 1
Post #500 627
📌 When AI Turns Criminal: deepfakes, voice-cloning & LLM-powered malware

Today we unpack how attackers weaponize generative AI — sharper spear-phishing, real-time voice/video fakes, and malware that models can write and refactor on the fly — plus what defenders can do today.

What’s inside:
🤖 How deepfakes and voice clones short-circuit trust, approvals, and even MFAs.
🔎 AI-scaled social engineering: personalized, context-aware outreach at volume.
🦠 LLM-assisted malware chains and why detection misses “AI fingerprints.”
🛡 Concrete playbooks: out-of-band verification, liveness checks, device fingerprinting, intent-aware filtering, tabletop drills.

👉 Read now: https://netlas.io/blog/ai_turns_criminal/
netlas.io When AI Turns Criminal: Deepfakes, Voice-Cloning & LLM Malware - Netlas Blog Explore how AI fuels deepfakes, voice-cloning, AI-written malware and spear-phishing — real incidents and actionable defenses for organizations and teams.
  • ❤ 3
  • 👾 3
  • 👍 1
Post #499 505
⚠️ Service Maintenance Notice
Please note that Netlas will experience brief service interruptions several times today and tomorrow due to maintenance. We appreciate your understanding and patience while we work to improve our system performance.
  • 💊 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →