TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.32K
Photos
433
Videos
3
Links
574

Showing posts older than #498 · Back to latest

Older Posts 20 shown
Post #497 619
CVE-2025-55752, -55754, -61795: Multiple vulnerabilites in Apache Tomcat, 5.3 - 9.6 rating 🔥

Three new vulnerabilities in Apache Tomcat allow attackers to perform DoS, RCE, and ANSI Injection.

Search at Netlas.io:
👉 Link: https://nt.ls/OLbr7
👉 Dork: http.favicon.hash_sha256:64a3170a912786e9eece7e347b58f36471cb9d0bc790697b216c61050e6b1f08 OR http.headers.server:"Apache-Coyote"

Vendor's advisory: https://lists.apache.org/thread/38vqp0v1fg4gr8c6lvm15wj6k67hxzxd
  • 🔥 3
  • 👾 3
  • 👍 2
Post #496 599
CVE-2024-9234, CVE-2024-9707, and CVE-2024-11972: Actively exploited vulnerabilities in WordPress plugins, 9.8 rating 🔥

Researchers at Wordfence have noted widespread attempts to exploit three last year vulnerabilities in the GutenKit and Hunk Companion plugins.

Search at Netlas.io:
👉 Link: https://nt.ls/6LlSh
👉 Dork: http.body:"plugins/gutenkit-blocks-addon" OR http.body:"plugins/hunk-companion"

Read more: https://www.wordfence.com/blog/2025/10/mass-exploit-campaign-targeting-arbitrary-plugin-installation-vulnerabilities/
  • 👍 3
  • 👾 3
Post #495 658
📌 Zero-Click Exploits — silent, interactionless compromises

Our new article explains how zero-click chains work, why they evade classic defenses, and what engineers and incident responders should prioritise.

Good and bad news alternate:

1️⃣ Bad: Zero-clicks are real and high-impact — real chains (iMessage, WhatsApp, Pegasus-style attacks) have been used to silently breach high-value targets.
2️⃣ Good: Many successful mitigations are practical — stricter input validation for parsers and media handlers reduces the attack surface.
3️⃣ Bad: End-to-end encryption and sandboxing remove traditional inspection points, so network sensors often can’t see malicious payloads.
4️⃣ Good: Layered telemetry, anomaly detection and ready IR playbooks can shorten dwell time and limit damage when interactionless compromises occur.
5️⃣ Bad: Zero-day economics + slow patching turn single flaws into long-running risks — many chains leave little forensic trace.
6️⃣ Good: Engineering fixes (fuzzing, careful protocol parsing, faster patch rollout) plus threat-informed testing make devices measurably safer.

The full article contains case studies, attack anatomy and concrete defensive recommendations.

👉 Worth a focused read: https://netlas.io/blog/zero_click_exploits/
netlas.io Zero-Click Exploits - Netlas Blog Explore zero-click exploits — stealthy, interactionless chains that evade defenses. Case studies reveal patch gaps and the need for stronger validation.
  • 👾 6
Post #494 616
CVE-2025-11702, -10497, -6601 and other: Multiple vulnerabilities in GitLab, 3.8 - 8.5 rating❗️

GitLab published a new advisory disclosing several vulnerabilities, including Improper Access Control, DoS, Incorrect Authorization, and others.

Search at Netlas.io:
👉 Link: https://nt.ls/ECfGM
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/10/22/patch-release-gitlab-18-5-1-released/
  • 🔥 2
  • 👾 1
Post #493 631
CVE-2025-62506: Privilege Escalation in MinIO, 8.1 rating❗️

A privilege escalation vulnerability allows service accounts and STS (Security Token Service) accounts with restricted session policies to bypass their inline policy restrictions when performing "own" account operations, specifically when creating new service accounts for the same user.

Search at Netlas.io:
👉 Link: https://nt.ls/yVIu7
👉 Dork: http.favicon.hash_sha256:7a2d79d4a5801b848bf2d577c6c3d16598d69fd78bc9d2399dcc4ac2497b0759 OR http.headers.server:"MinIO" OR http.meta:"MinIO" OR http.favicon.hash_sha256:052d1670e36345713bd69e405403034f69b3a0adab8fa7d6f178faac4406199a

Vendor's advisory: https://github.com/minio/minio/security/advisories/GHSA-jjjj-jwhf-8rgr
  • 👾 7
Post #492 691
🚨 When Patches Fail — why fixes get bypassed and what to check after an update

Patches often fix a symptom, not the root cause. This analysis walks through real bypass timelines (SharePoint, SAP, NTLM, Grafana), shows how NVD/KEV delays and PoC/IOC flows speed exploitation, and gives compact checks teams should run immediately.

Quick highlights:
🧩 Concrete case studies with timelines and residual CVEs.
⚖️ Why many vendor patches are incomplete — root-cause vs surface fixes.
⏳ How disclosure delays and fast PoC/AI tooling narrow your window.
🛠️ Actionable post-patch checklist: test alternative code paths, validate root issue, chain input tests, and apply virtual patches (WAF/IPS).
🔍 Netlas-based telemetry and simple queries to measure internet exposure.

👉 Read the full analysishttps://netlas.io/blog/when_patches_fail/
netlas.io When Patches Fail: An Analysis of Patch Bypass and Incomplete Security - Netlas Blog Patches fix bugs, not always the attack. This article shows how fixes get bypassed — and what quick checks defenders should run after updates.
  • 👍 3
  • 👾 2
Post #490 643
CVE-2025-42944, -42937, -42910, and other: Multiple vulnerabilities in SAP NetWeaver, 5.3 - 10.0 🔥🔥🔥

In its October bulletin, SAP published a list of 13 new vulnerabilities affecting NetWeaver, NetWeaver AS Java, and other products. These vulnerabilities include Insecure Deserialization, Information Disclosure, etc.

Search at Netlas.io:
👉 Link: https://nt.ls/aBHGg
👉 Dork: http.headers.server:"NetWeaver"

Vendor's advisory: https://support.sap.com/en/my-support/knowledge-base/security-notes-news/october-2025.html
  • 👍 2
  • 🔥 2
  • 👾 2
Post #489 828
🔍 3 Million Databases Later: Mapping Internet Exposure with Netlas

A data-driven investigation of 3.2 million internet-facing databases — MySQL, MongoDB, PostgreSQL, MSSQL, Oracle, and Elasticsearch — revealing how exposed they really are, which controls fail most often, and where the global weak spots hide.

What you’ll learn in 20 minutes:
🧩 How Netlas scans were used to get millions of database banners and metadata worldwide.
⚙️ The pipeline behind the study — from raw banners to per-service risk scoring and global aggregation.
📊 Who’s most exposed: MySQL leads with 2.53 M instances, MongoDB still leaks metadata, PostgreSQL flunks TLS at scale.
🪜 Practical remediation steps — per-service hardening tips and global trends that shape today’s attack surface.

For security engineers, analysts, and anyone mapping the exposed-data landscape — this is a rare, quantified look at how misconfiguration still fuels risk in 2025, written by a cool researcher in collaboration with Netlas.

👉 Read the full research: https://netlas.io/blog/exposed_databases/
netlas.io I Analysed Over 3 Million Exposed Databases Using Netlas - Netlas Blog Analysing 3.2M exposed databases with Netlas to reveal global risks, failed controls, and exposure trends across major DB systems
  • ❤ 4
  • 👾 4
Post #488 645
CVE-2025-11340, CVE-2025-10004, and other: Multiple vulnerabilities in GitLab, 4.3 - 7.7 rating❗️

In a recent bulletin, GitLab reported four vulnerabilities, including Missing Authorization, DoS, and Incorrect Authorization.

Search at Netlas.io:
👉 Link: https://nt.ls/vHRRQ
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/10/08/patch-release-gitlab-18-4-2-released/
  • ❤ 2
  • 👾 2
Post #486 678
CVE-2025-49844, -46817, -46818, -46819: Multiple vulnerabilities in Redis, 6.0 - 10.0 rating 🔥🔥🔥

Four recently disclosed vulnerabilities in Redis include Use After Free, Code Injection, and Integer Overflow. All versions that support the Lua language are vulnerable.

Search at Netlas.io:
👉 Link: https://nt.ls/gZwyS
👉 Dork: redis.memory_info.used_memory_lua:>0

Vendor's advisory: https://github.com/redis/redis/security/advisories/GHSA-4789-qfc9-5f9q
  • 🔥 4
  • 👾 3
Post #485 855
📌 Post-Quantum Now: from AES & RSA to ML-KEM Hybrids

A crisp, practical guide to navigating the quantum shift: how today’s crypto stack really works, what breaks with quantum, what survives (hello, AES-256), and how to roll in ML-KEM/Dilithium without breaking prod.

Highlights you’ll get in 10 minutes:
1️⃣ A little tour of the “digital trust” stack — AES modes, nonce pitfalls (GCM vs SIV), and why key-derivation details matter.
2️⃣ Quantum threat & HNDL explained: keep symmetric strong (AES-256), plan to replace public-key (RSA/ECDSA/curves).
3️⃣ What NIST is standardizing now: ML-KEM (Kyber) for key establishment and ML-DSA (Dilithium) for signatures — with libraries you can use today (liboqs/pyoqs).
4️⃣ Hands-on hybrid recipe: X25519 + ML-KEM, transcript-bound HKDF, and a minimal Python snippet to derive a shared session key.
5️⃣ Migration roadmap you can copy-paste: Shadow Mode → Hybrid Mode → Audit & Logging → Policy flags → Crypto agility best practices.

If you’re a security engineer, architect, or CISO planning 2025 rollouts, this is your field guide to ship PQC with confidence — not someday, but now.

👉 Read the full post: https://netlas.io/blog/post_quantum_cryptography/
netlas.io Post-Quantum Now: From AES & RSA to ML-KEM Hybrids - Netlas Blog A Practical Guide to Post-Quantum Cryptography: Algorithms, Migration Roadmap, Risks, and Metrics
  • 👍 8
  • 👾 4
  • ❤ 3
Post #484 573
CVE-2021-43798: The reborn Path Traversal in Grafana, 7,5 rating❗️

Researchers at GreyNoise have discovered a large-scale malware campaign that exploits a relatively old vulnerability. It allows attackers to access local files on a server, thereby compromising privacy.

Search at Netlas.io:
👉 Link: https://nt.ls/5RrJ3
👉 Dork: http.favicon.hash_sha256:80a7f87a79169cf0ac1ed3250d7c509368190a97bc7182cd4705deb8f8c70174 AND http.title:"Grafana"

Read more: https://www.greynoise.io/blog/coordinated-grafana-exploitation-attempts
  • 🔥 2
  • 👾 2
Post #482 807
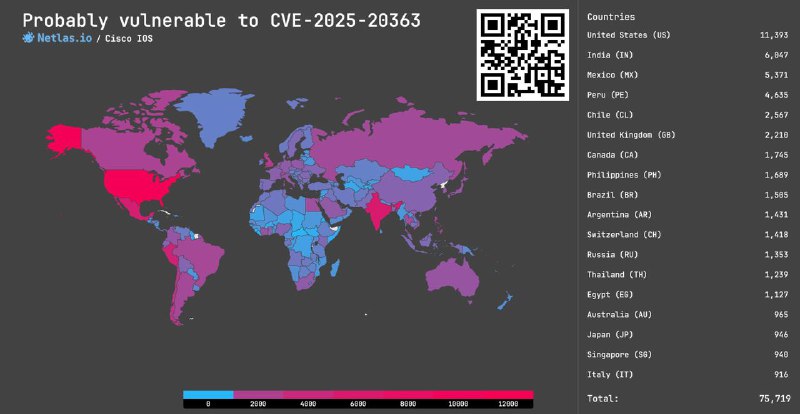
CVE-2025-20363: Buffer Overflow (again) in Cisco IOS (again), 9.0 rating 🔥

Another vulnerability has been discovered in Cisco products, including IOS. This time, an attacker can execute code without having high privileges!

Search at Netlas.io:
👉 Link: https://nt.ls/NQLA2
👉 Dork: certificate.issuer_dn:"IOS-Self-Signed-Certificate"

Vendor's advisory: https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-http-code-exec-WmfP3h3O
  • 👾 4
Post #479 703
🚧 Planned Maintenance 🚧
The Private Scanner will be unavailable for a period of time❗️

We remind you that in some minutes, planned Scanner servicing will begin. It is expected to take a full day, but we will do our best to complete it as quickly as possible.

Please remember to save your work before this time.
  • 🕊 1
Post #478 764
🚧 Planned Maintenance 🚧
The Private Scanner will be unavailable for a period of time❗️

On Sunday, September 21, 2025, at 08:00 UTC ⏰, we will be servicing the Netlas Private Scanner. This may take all day, but our team will do everything possible to complete this task as quickly as possible.

Please remember to save your work before this time.
  • 🔥 2
  • 👾 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →